Open navigation menu - Kieri Solutions
Why the DoD Wants Security Protection Data Protected Like CUI

Why the DoD Wants Security Protection Data Protected Like CUI

Abstract data network tied to security protection data and CMMC scope assessed by Kieri

In this article

The CMMC proposed rule introduces a concept some defense contractors find puzzling. Security protection data.

This category includes vulnerability scan results, system security plans, network diagrams, firewall configurations, and endpoint security settings. Under 32 CFR Part 170, when an external service provider handles security protection assets but doesn’t process, store, or transmit CUI directly, those services are assessed as part of the contractor’s own CMMC assessment. ESPs can also choose to obtain their own CMMC Level 2 certification, which reduces the assessment burden. Certified ESPs are listed on the MSP Collective.

Some contractors have questioned why security information gets this level of attention.

The answer comes from real-world patterns that show exactly the threat the DoW is trying to prevent.

The Intelligence Value of Security Data

When you work with any third party on cybersecurity, you share detailed information about your security posture.

Your System Security Plan describes how you protect CUI. Where it’s stored. How it’s encrypted. Who has access. What controls are in place.

Your network diagrams show what systems connect to what. Where your boundary is. What’s exposed to the internet. How traffic flows through your environment.

Your firewall rules reveal permitted and blocked network traffic. Your vulnerability scan results show exactly where your weaknesses are.

Your physical security documentation describes locks, access controls, camera placements, guard rotations, and facility layouts.

For an adversary wanting to access your CUI, this information is invaluable. It’s a roadmap for attack. It identifies the weakest points. It shows what defenses they’ll need to bypass.

Patterns Worth Watching in the Provider Ecosystem

As CMMC has matured, the ecosystem of consultants, RPOs, and supporting service providers has grown quickly. Most are legitimate. Some warrant a closer look.

A few patterns are worth watching for.

  • US business addresses that resolve to mailbox services or strip malls with no actual office presence
  • Ownership traceable to foreign jurisdictions
  • Principals whose social media or public profiles place them outside the country
  • No verifiable consultant backgrounds, clearances, or US-based staff records
  • Vague answers about where data is stored or who has administrative access

These signals don’t automatically mean a provider is illegitimate. They do mean a contractor should ask harder questions before sharing security documentation.

The business model is straightforward from an intelligence perspective. Defense contractors need help. They’ll share sensitive security information with helpers. Position yourself as a helper, and contractors voluntarily hand over exactly the information an intelligence service would want.

GRC Platforms Present Similar Risks

In 2020 to 2021, as CMMC requirements were emerging, numerous GRC platforms launched to serve the market.

These platforms let contractors enter their System Security Plans, upload artifacts, store vulnerability scan results, and manage compliance documentation. Convenient tools that centralize exactly the information that creates intelligence value.

One platform in particular was among the top three or four in the market. It specifically advertised for CMMC compliance. It targeted US defense contractors.

Research revealed the platform’s ownership traced to foreign interests. The company was positioned to collect vulnerability data and security documentation from defense contractors across the industry.

When publicly questioned about this, the company threatened legal action, then disappeared.

https://youtu.be/naQfeSmrPug

Why This Matters for the CMMC Rule

The CMMC proposed rule’s treatment of security protection data makes more sense in this context.

The DoW isn’t being paranoid or bureaucratic. Foreign adversaries are actively trying to gather security information from the Defense Industrial Base, and the rule is designed to acknowledge that reality.

Posing as a CMMC consultant or GRC platform is efficient.

  • Legitimate-appearing business relationship
  • Contractors voluntarily share data
  • Complete picture of security posture
  • Direct access to vulnerability information
  • Scalable across many contractors

Treating ESPs that handle security protection assets as part of the contractor’s CMMC scope, or pointing contractors toward Level 2 certified ESPs through the MSP Collective, raises the bar. It doesn’t eliminate all risk, but it gives contractors a clearer way to evaluate who they’re trusting with sensitive information.

The Current State of Provider Certification

The pool of certified providers is still small. The organizations authorized as C3PAOs have all passed CMMC Level 2 assessment by DCMA DIBCAC, but their numbers are modest compared to the overall cybersecurity service provider market.

RPOs have even less demonstrated compliance. Some have been working toward Level 2 for years and likely operate at that level internally. Third-party verified assessments are rare.

GRC platforms present particular challenges. Many aren’t FedRAMP authorized. Their data centers may be anywhere. Their administrative access may be uncontrolled. The platforms that look most concerning from an intelligence perspective often lack any independent security verification.

Due Diligence Recommendations

Before sharing security protection data with any external party, conduct thorough due diligence.

Verify ownership and location. Research the company. Who owns it? Where are they actually located? Does the US address resolve to an actual office?

Research company background. How long have they existed? What’s their track record? Can you verify their claims?

Check consultant credentials. Are the people you’ll work with actually qualified? Can you verify their backgrounds?

Evaluate platform security. For GRC tools, are they FedRAMP authorized? Where are their data centers? Who has administrative access?

Ask about their own compliance. If they handle security protection data, what’s their own CMMC status? Have they been assessed? Are they listed on the MSP Collective?

Trust your instincts. If something feels off, it probably is. Red flags exist for a reason.

The Broader Lesson

The security protection data requirement isn’t arbitrary bureaucracy. It reflects real threats to the Defense Industrial Base.

Foreign intelligence services have recognized that CMMC creates opportunities. Contractors need help. They’ll share sensitive information with helpers. Position yourself as a helper, and collection becomes easy.

The DoW is trying to close that vector. Treating security protection assets as part of the CMMC scope creates accountability. It doesn’t solve everything, but it raises the bar.

Defense contractors should welcome this protection, even when it creates inconvenience. The alternative is voluntarily handing intelligence to adversaries while thinking you’re getting compliance help.


Kieri Solutions is one of few authorized C3PAOs in the United States. We passed our own CMMC Level 2 assessment with DCMA DIBCAC. When we discuss security protection data requirements, we’ve demonstrated compliance ourselves.

Working with consultants or platforms? Verify their credentials and security posture before sharing sensitive information.

Schedule a consultation to discuss whether the KCD fits your compliance needs. kieri.com/schedule-consultation
Cybersecurity data analysis supporting CMMC Level 2 audit preparation for defense contractors

Talk to an Expert

Tell us where you are with compliance and we’ll map out the next steps for your team.

Don't miss these

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan
Is Your Security Plan Telling the Truth?
What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.
What Does the Government Actually Require of You Today?
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
CMMC Backup Requirements and The Myths Worth Ignoring
Server backup drives in a dark data center supporting CMMC backup requirements for a defense contractor
CMMC Backup Requirements and The Myths Worth Ignoring
How to Prepare for a DIBCAC High Assessment
Analyst reviewing evidence on dark dual monitors while preparing for a DIBCAC High assessment
How to Prepare for a DIBCAC High Assessment
Out of Scope Assets - What the Final Rule Actually Changed
Abstract data cityscape tied to out of scope assets in a CMMC assessment by Kieri Solutions
Out of Scope Assets - What the Final Rule Actually Changed
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
Dark cybersecurity image with glowing data illustrating CMMC final rule compliance for defense contractors
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
Analyst reviewing code while working toward CMMC and NIST 800-171 compliance
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
CUI Assets - What Assessors Actually Evaluate
Abstract network of nodes tied to CUI assets and CMMC scope assessed by Kieri Solutions
CUI Assets - What Assessors Actually Evaluate
Do I Even Have CUI? Understanding What You Need to Protect
Abstract data network tied to finding CUI on a defense contractor network with Kieri
Do I Even Have CUI? Understanding What You Need to Protect
Why the DoD Wants Security Protection Data Protected Like CUI
Abstract data network tied to security protection data and CMMC scope assessed by Kieri
Why the DoD Wants Security Protection Data Protected Like CUI
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Cybersecurity professional conducting CMMC gap analysis for a defense contracting organization
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Network architecture visualization for a CMMC Level 2 reference architecture built on Microsoft 365 GCC High
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Why Most CMMC Documentation Fails and How to Fix It
CMMC compliance documentation policies and procedures
Why Most CMMC Documentation Fails and How to Fix It
What Passed a DOD Assessment for System Baselining and Inventories
CMMC system inventory and baseline configuration monitoring dashboard
What Passed a DOD Assessment for System Baselining and Inventories
How to Implement Mobile Code Requirements for CMMC Level 2
CMMC mobile code security controls and technical implementation
How to Implement Mobile Code Requirements for CMMC Level 2
What Does "Monitor" Actually Mean in CMMC Requirements?
CMMC monitoring requirements - access control and password security verification
What Does "Monitor" Actually Mean in CMMC Requirements?
The Version 20 Problem and How to Avoid It
CMMC compliance documentation sequence - cybersecurity program management
The Version 20 Problem and How to Avoid It
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
CMMC Level 2 compliant environment security controls and access management
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
Inside the KCD - What Makes This Documentation Different
CMMC compliance documentation templates digital security
Inside the KCD - What Makes This Documentation Different
How the Kieri Compliance Documentation and Reference Architecture Work Together
Kieri Compliance Documentation and Reference Architecture working together for CMMC Level 2 compliance
How the Kieri Compliance Documentation and Reference Architecture Work Together
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC compliance documentation and reference architecture security controls - fingerprint scanning and access management
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC Assessments by Kieri Solutions
Global cybersecurity compliance support for defense contractors under DFARS
CMMC Assessments by Kieri Solutions
CMMC Education: User vs Network Session Termination
Secure IT infrastructure design supporting CMMC Level 2 compliance for defense contractors
CMMC Education: User vs Network Session Termination
CMMC Proposed Rule has been released! 
Cybersecurity threat - CMMC compliance
CMMC Proposed Rule has been released! 
Interested in the Kieri Compliance Documentation?
Secure data transmission within CMMC compliant network architecture
Interested in the Kieri Compliance Documentation?
How to fix Outlook missing Friday January 13 2023
Interconnected defense contractor networks requiring CMMC Level 2 cybersecurity certification
How to fix Outlook missing Friday January 13 2023
C3PAO Meeting - July 26, 2021 12-1 pm EDT
NIST SP 800-171 DoD Self Assessment Services
DFARS 252.204-7012 and NIST SP 800-171 requirements
NIST SP 800-171 DoD Self Assessment Services
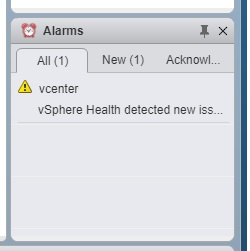
vSphere Health detected new issues in your environment 6.7
vcenter 6.7 alarm displays vsphere health detected new issue
vSphere Health detected new issues in your environment 6.7
vCenter Health Warning: External Platform Services Controller
Synology storage latency and disconnects on VMware
Windows Stuck in Recovery Mode Datto driver signing
Office 365 MFA App Password Missing Fix
Microsoft Teams Conference Calls & Dial-In Numbers
C: Drive Full Exchange
Exchange server very slow, services and network blank
Exchange 2016 DAG - 3 servers 2 sites
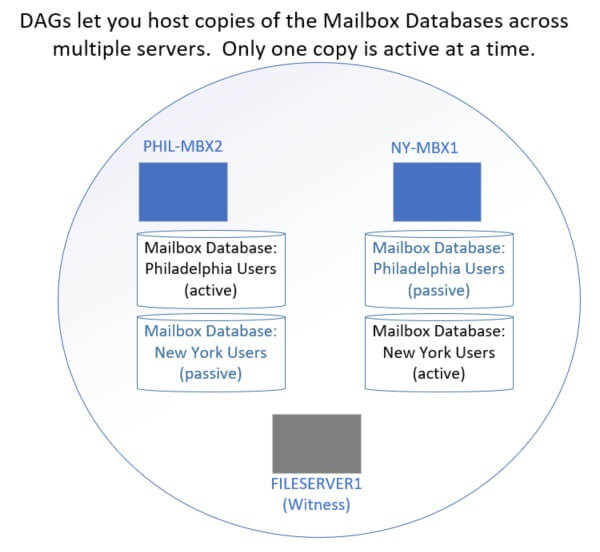
Diagram showing mailbox servers with active and passive databases. Each database is only active on one server.
Exchange 2016 DAG - 3 servers 2 sites
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
Kieri Solutions partnering with defense contractors to achieve CMMC Level 2 certification
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
warning vsphere health detected new issue memory exhaustion 6.7 vcenter
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
Step by Step: Upgrade vCenter VCSA 6.0 (or 6.5) to 6.7
How to prepare for a DoD CMMC audit and certification
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
How to prepare for a DoD CMMC audit and certification
Fix Expired vCenter Root Password (6.5 & 6.7)
How to rename Windows Server 2016 Domain Controller
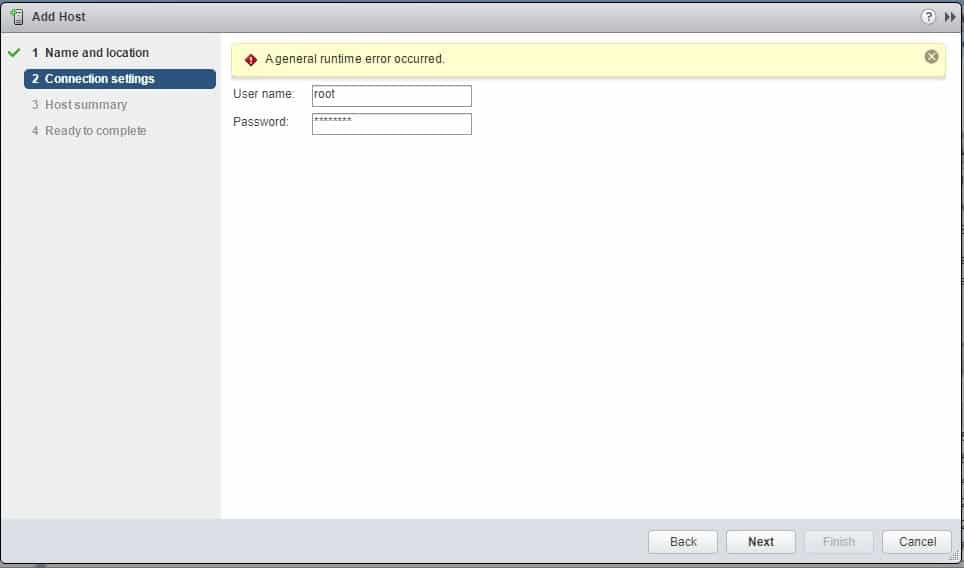
Runtime Error Adding Host in VMware vCenter & ESXi
add host a general runtime error occurred vcenter 6.5 6.7
Runtime Error Adding Host in VMware vCenter & ESXi
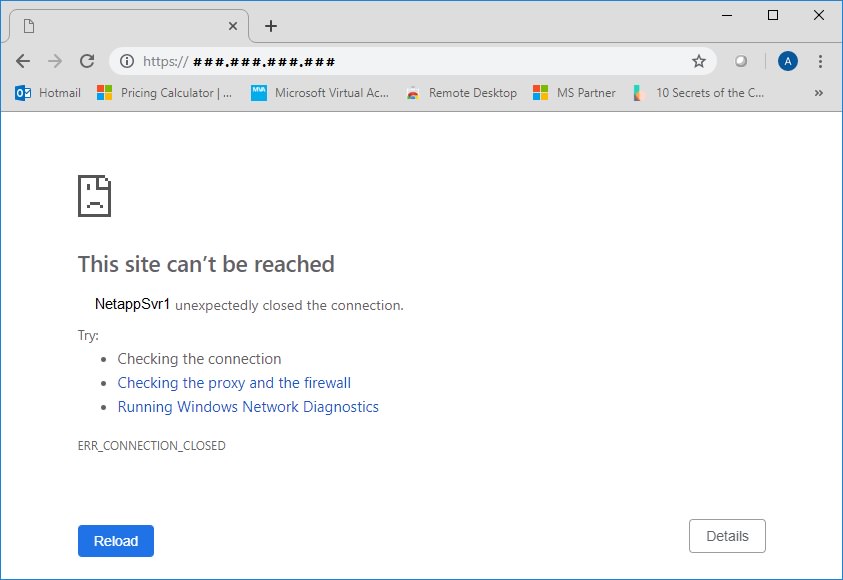
How to fix Netapp expired self-signed certificate by creating a new one
netapp certificate expired install site cant be reached
How to fix Netapp expired self-signed certificate by creating a new one
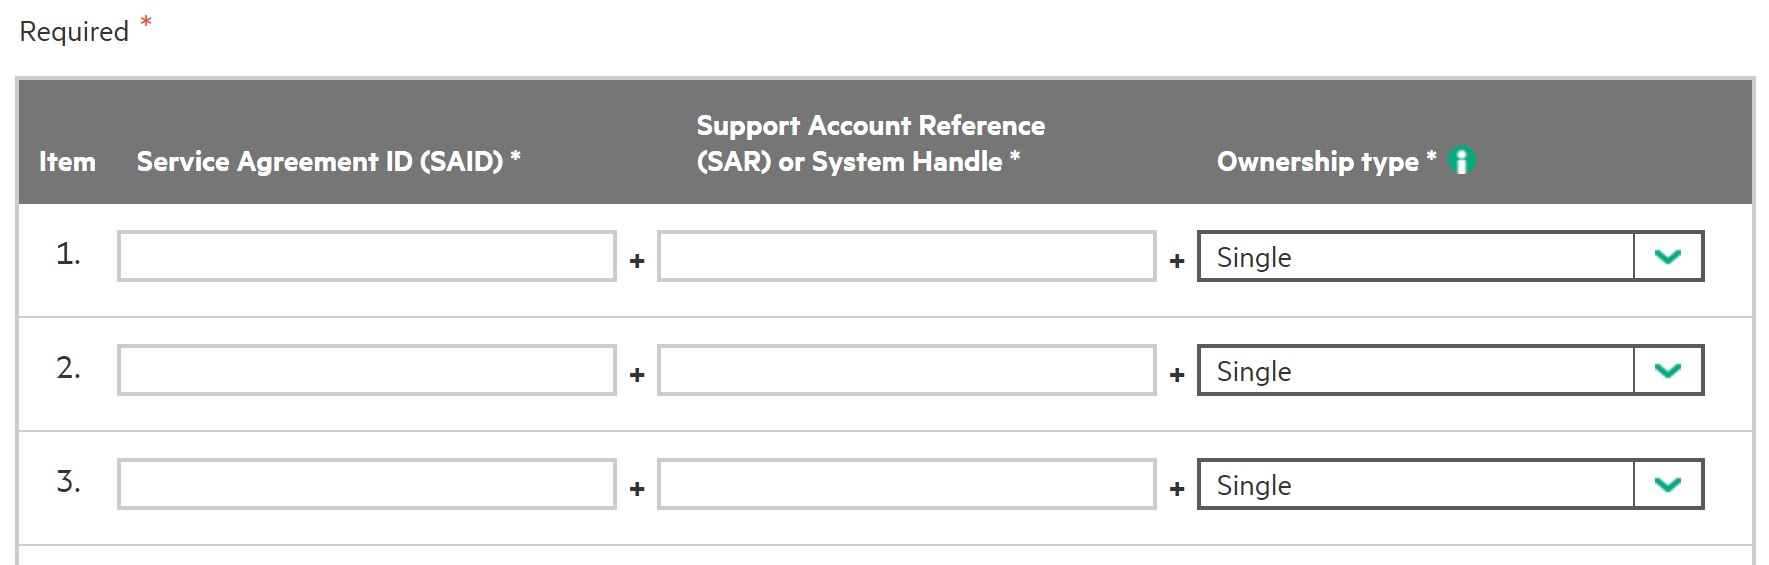
How to register a warranty or service agreement on HPE website
hpe hp register account SAR ID service agreement warranty how accept
How to register a warranty or service agreement on HPE website
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
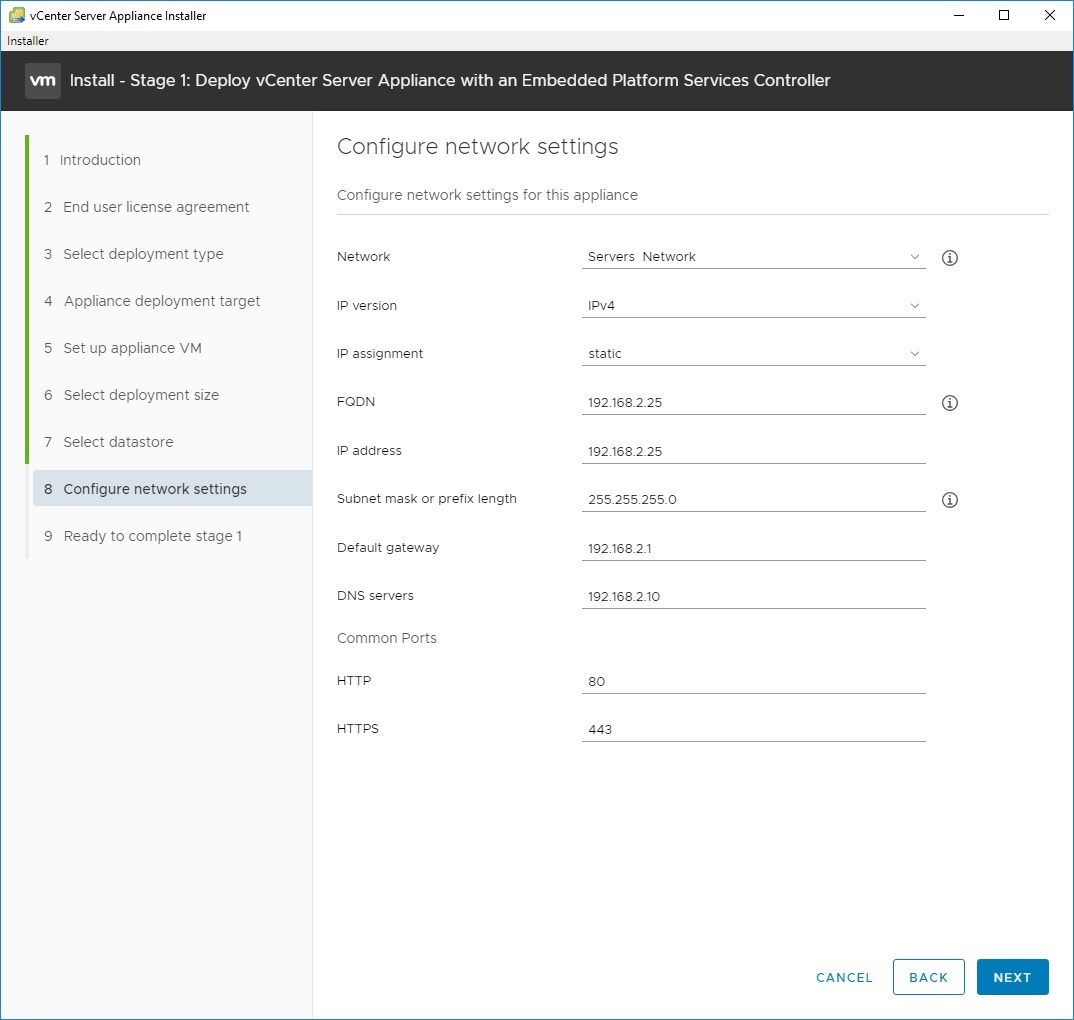
vcenter ip address no dns
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
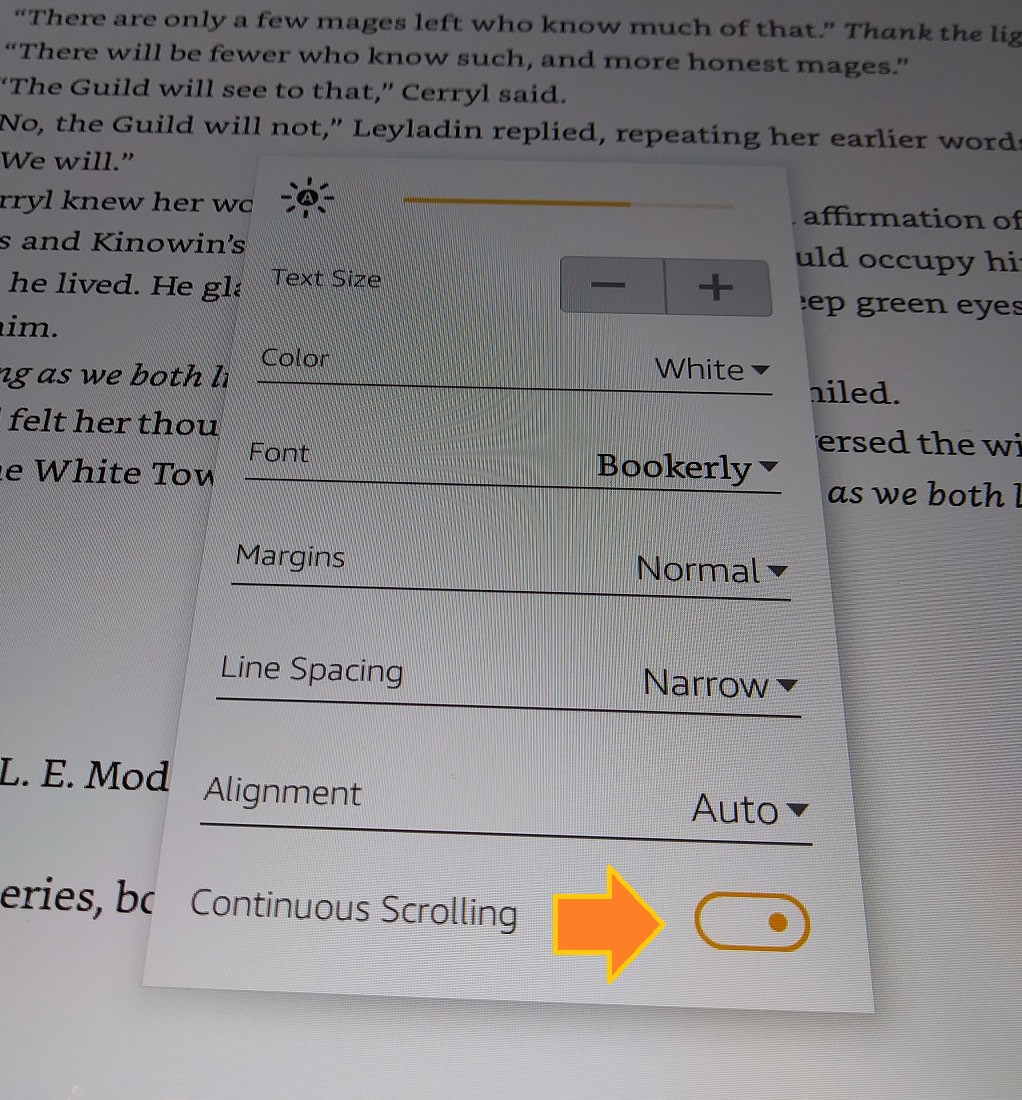
How to disable continuous scrolling on Kindle - turn on page flip
disable continuous scrolling option displays
How to disable continuous scrolling on Kindle - turn on page flip
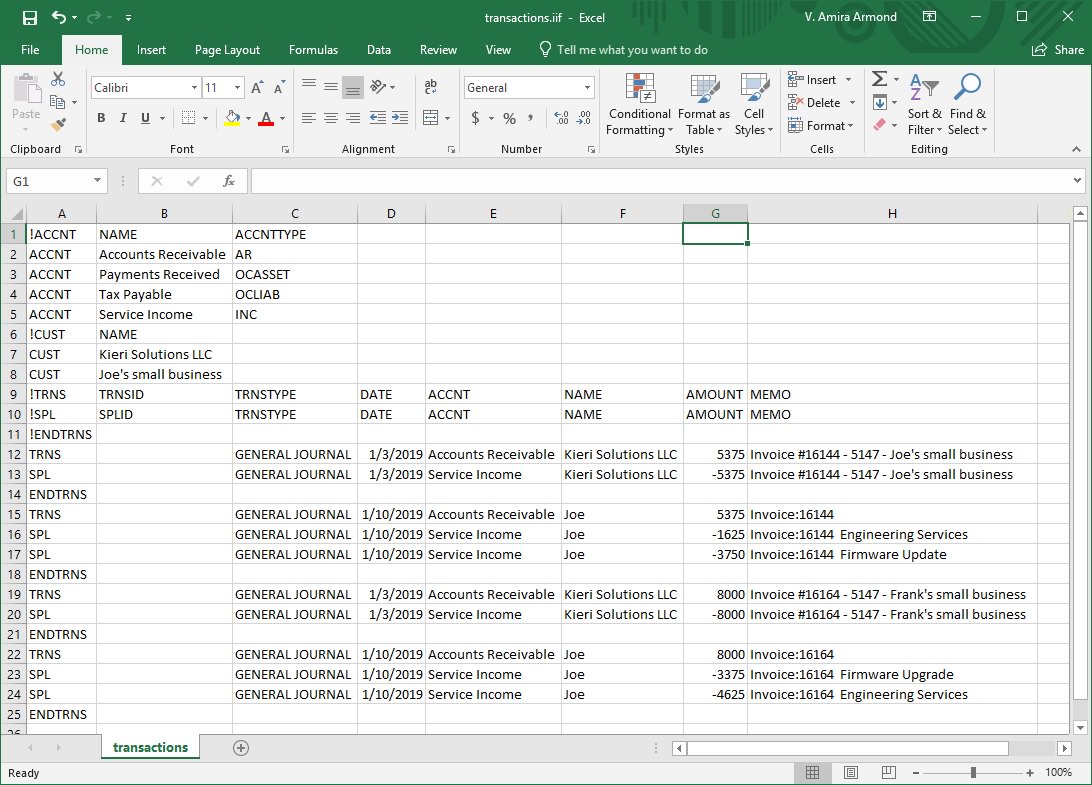
17hats how to export or convert to Excel CSV TAB XLS workbook
17hats export convert iff to csv tab excel
17hats how to export or convert to Excel CSV TAB XLS workbook
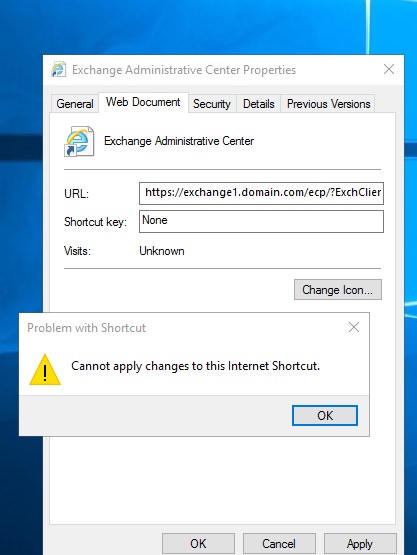
How to fix "Cannot apply changes to this Internet Shortcut" Windows
cannot apply changes to this internet shortcut 2016 2019
How to fix "Cannot apply changes to this Internet Shortcut" Windows
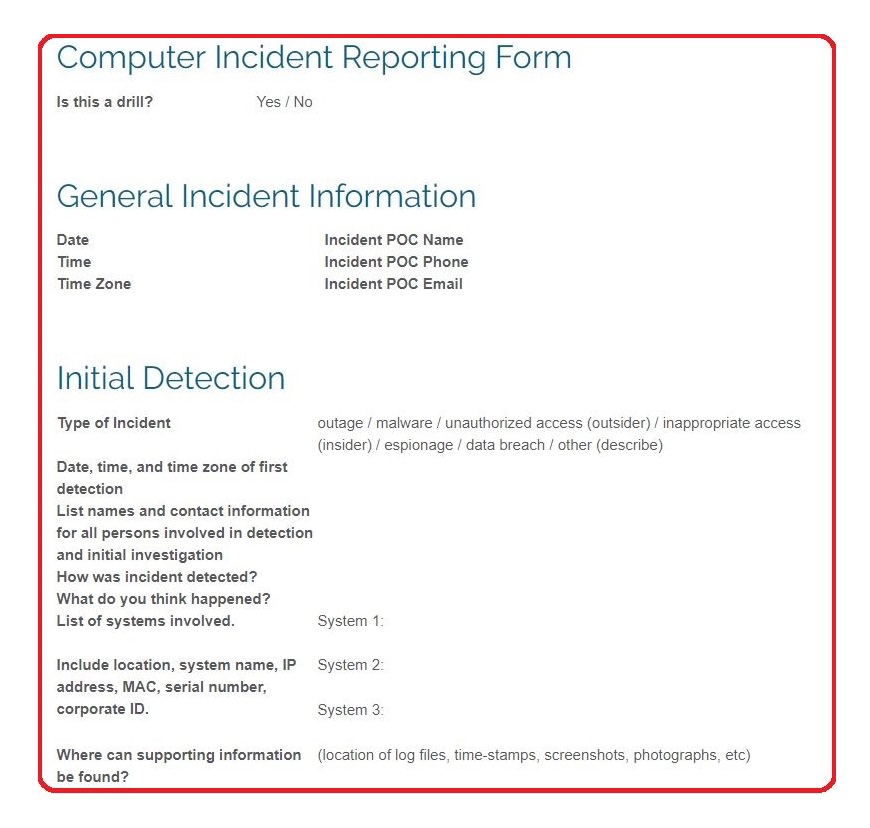
Best Free Computer Incident Response Templates and Scenarios
best free incident response reporting form cybersecurity IT
Best Free Computer Incident Response Templates and Scenarios
Firmware & System Patching Services | DC & Maryland
poweredge server raid reconfigure add disks 1 5
Firmware & System Patching Services | DC & Maryland
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
Best practice network segmentation and hardening prevents pivot attacks NIST
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Best practices and how to install esxi vsphere vcenter vmware and troubleshooting problems during the migration
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Disaster Recovery & Business Continuity in DC & Maryland
disaster recovery drp bcp hipaa frederick columbia gaithersburg baltimore rockville
Disaster Recovery & Business Continuity in DC & Maryland
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
installation services netapp disk shelf baltimore columbia rockville
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
SBDC - Intro to GDPR training - Frederick MD
intro gdpr overall sbdc fitci frederick
SBDC - Intro to GDPR training - Frederick MD
GDPR and Human Resources
cybersecurity cyber security hardening compliance firewall design frederick
GDPR and Human Resources
No, your computer isn't slow.
why slow computer pc repair frederick damascus mt airy md
No, your computer isn't slow.
Why you should consider a credit freeze - EquiFax hack
credit freeze equifax hack how to breach innovis
Why you should consider a credit freeze - EquiFax hack
Virtual Servers, Storage, and SAN - Why your servers are slow
cybersecurity compliance design consulting engineering
Virtual Servers, Storage, and SAN - Why your servers are slow
How to un-freeze your laptop like a pro
pc or computer problem repair damascus lisbon mt airy laytonsville
How to un-freeze your laptop like a pro
Upgrade your IT Services for the New Year
managed services it department outsource company frederick columbia germantown gaithersburg
Upgrade your IT Services for the New Year
Dell PowerEdge R730 PERC RAID online reconfiguration
poweredge server raid reconfigure add disks 1 5
Dell PowerEdge R730 PERC RAID online reconfiguration
Dreamhost HTTP error Wordpress media upload and library
dreamhost http error picture disappear upload shared wordpress
Dreamhost HTTP error Wordpress media upload and library
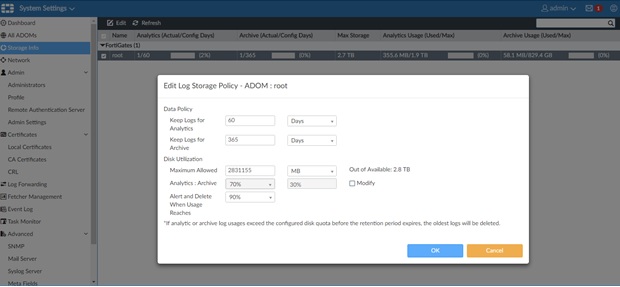
FortiAnalyzer Configuration problems after initial deploy
FortiAnalyzer 5.4 Storage Quota Limits for ADOM root
FortiAnalyzer Configuration problems after initial deploy
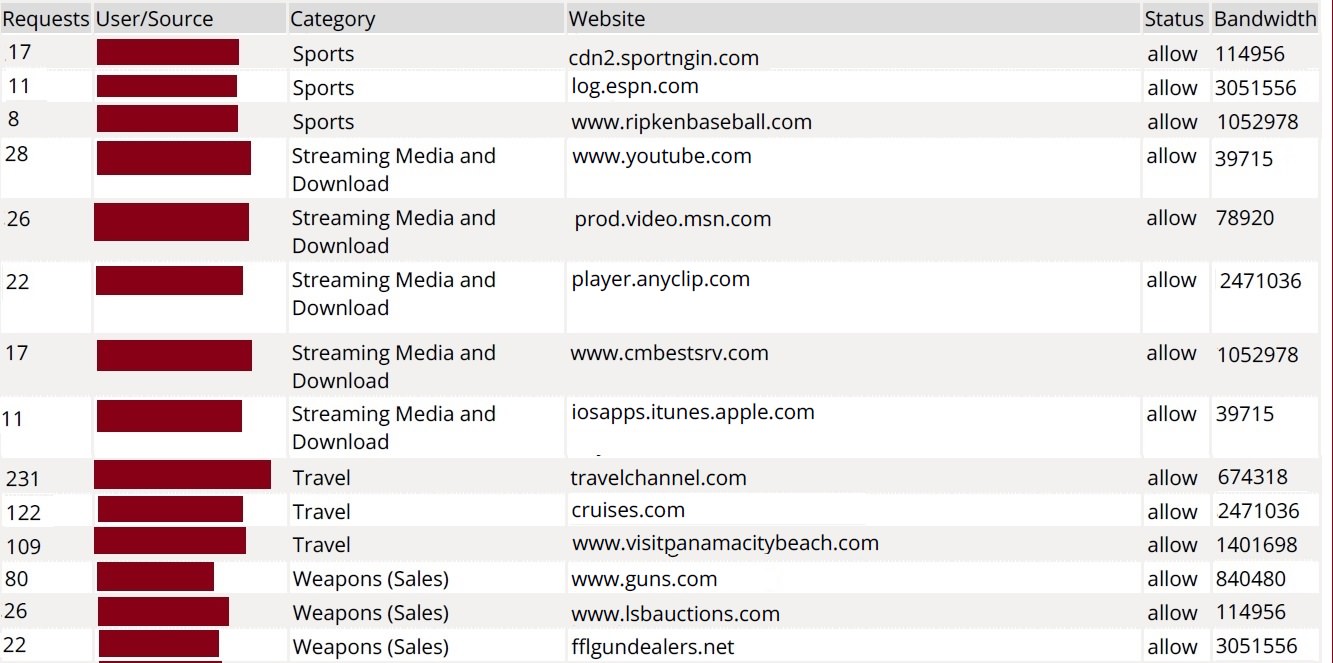
FortiAnalyzer Report: User Web Browsing by Category
fortianalyzer custom report users by category who is browsing web goofing off
FortiAnalyzer Report: User Web Browsing by Category
GDPR Consulting - What you need to know
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
GDPR Consulting - What you need to know
The #1 Computer Security Threat Just Evolved - RCE Worm
cybersecurity cyber security compliance firewall frederick md
The #1 Computer Security Threat Just Evolved - RCE Worm
Fix vSphere & vCenter Datastore Size Reverting
security design cybersecurity consulting services compliance
Fix vSphere & vCenter Datastore Size Reverting
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
conflicting vibs error vsphere upgrade metadata consultant vmware
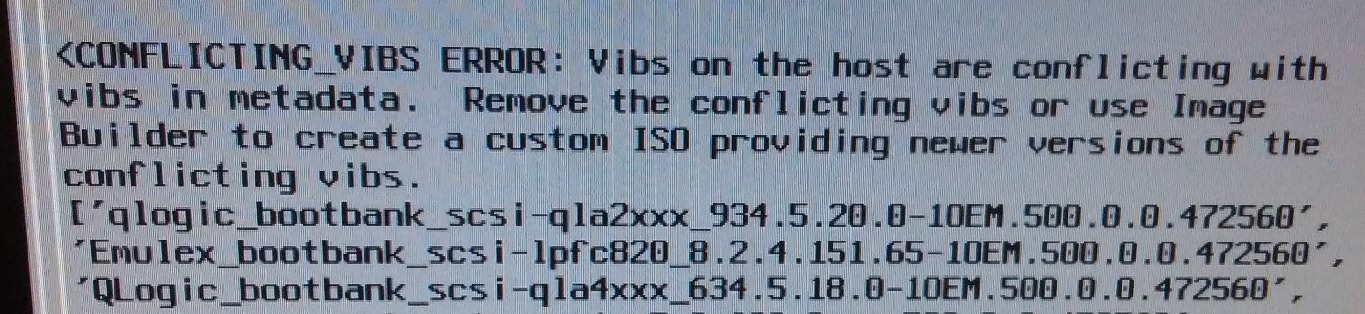
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
Is your IT person holding the network hostage?
Server Upgrade Cybersecurity Consultant SAN Netapp Frederick
Is your IT person holding the network hostage?
4 Hiring Mistakes When Choosing an IT Company
mistakes when hire IT consultant MSP managed service provider computer support outsourcing
4 Hiring Mistakes When Choosing an IT Company
What you should know about Cloud Computing and Office 365
cloud IT department migration Office 365 Frederick Baltimore Columbia MD
What you should know about Cloud Computing and Office 365
Can You Make Our Nation Safe from Hackers?
The Ultimate Way to Protect Against Computer Theft
Kieri Solutions site icon
The Ultimate Way to Protect Against Computer Theft
Small / medium business security concerns
managed services it department outsource company frederick columbia germantown gaithersburg
Small / medium business security concerns
Approaches to security policy
cybersecurity cyber security hardening compliance firewall design frederick
Approaches to security policy

Article

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan

Article

What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.

Article

NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3

No one wants to start from blank templates.

No one wants to start from
blank templates.

Stop starting from blank templates. Get documentation proven through actual CMMC Level 2 assessment.