Open navigation menu - Kieri Solutions
How to prepare for a DoD CMMC audit and certification

How to prepare for a DoD CMMC audit and certification

cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53

In this article

Ms. Katie Arrington (Special Assistant to the Assistant Secretary of Defense for Acquisition for Cyber) gave a presentation to small DoD contractors on May 23, 2019 to announce a new program which will require cyber-security audits and certification for all DoD contractors.

The proposed program is called the Cybersecurity Capability Model Certification (CMMC).

Here are my notes from the presentation.

Background

Per Federal Acquisition Regulations (FAR), federal contractors must comply with a list of cyber-security best practices.   Currently, contractors are required to self-certify that their computer systems follow cyber-security best practices if they deal withh Controlled Unclassified Information (CUI).

What is CUI?

Controlled Unclassified Information is data that needs to be protected against release, but has not been classified by the United States Government. For example, military vehicle design schematics could be considered Controlled Unclassified Information. This information may be shared with federal contractors in order to manufacture replacement parts, or for reference while performing maintenance contracts. CUI also includes well-known sensitive categories such as personally identifiable information and health records for service members.

The proposed CMMC will now require every DoD contractor to have their computer systems certified in order to bid on RFPs. The contractor does not need to be handling CUI.

The problem identified by Ms. Katie Arrington is that the self-certification requirement for cybersecurity is not working. Theft of sensitive information from federal contractor systems has increased over time, not decreased. As a solution, her office (DoD Cyber, Acquisitions) is leading an initiative called the Cybersecurity Maturity Model Certification (CMMC).

The CMMC initiative will require DoD contractor information systems to be certified compliant by an outside auditor. This solves an issue where some businesses self-certify compliance without fully implementing (or understanding) needed security controls.

CMMC predecessor – NIST SP 800-171

In 2016, the National Institute of Standards and Technology (NIST) released a document named “Special Publication 800-171”. This lists 110 cyber-security best practices that contractors with access to CUI must comply with. An example of an individual best practice is requiring strong passwords for any account that can access CUI.

While compliance with NIST 800-171 is a requirement in order to win new contracts, there is no auditing or certification program in place yet. Government contractors are allowed to self-certify that they meet the security requirements.

Highlights of the CMMC

  • A single standard used across all DoD contracts starting in 2020-2021
  • Considered a “go/no-go” requirement
  • Based on the NIST 800-171 controls
  • Identifies five levels of data security so that contractors can implement reasonable security for the data they deal with. Encourages government contract officers to pick an appropriate tier (not everything requires level 5)
  • Provide automated tool which automatically gathers data to simplify reporting efforts
  • Required CMMC level will be contained in RFP sections L & M
  • Authorizes a non-profit organization to oversee the program and accredit private-sector auditors
  • Makes cybersecurity an “allowable cost” in DoD contracts
  • DoD contractors will need to be certified at a specific security level before they qualify to bid on contracts.

Timeline for CMMC enforcement

Ms. Katie Arrington described the following timeline for CMMC:

Mid 2019 – Working groups and creation of automated assessment tools.

Early 2020 – Begin developing oversight and certifier accreditation program, processes.

Mid 2020 – Test the certification program and revise it.

Mid/late 2020 – Accredit third-party certifiers.

Future – Begin adding CMMC requirement to all new DoD RFPs

Updated: How to become a CMMC auditor

Check this article on cmmcaudit.org which gives the latest info on the CMMC Accreditation Body and what is still needed to accredit auditors and certifiers.


Next are my thoughts about what DoD contractors should be doing to prepare. These steps are my recommendations as a cyber-security consultant and are not from Kate Arrington’s presentation.

Opinion: How is cyber security an allowable cost when your company doesn’t get the contract?

How many hours to prepare for CMMC or 800-171?

There are three factors for estimating the cost and work involved with compliance.

  1. How complex is the network you are evaluating?
  2. Does your network already have secure configurations and security programs installed?
  3. What CMMC level are you trying to meet?

This Reddit thread has a frank discussion of the effort involved with a NIST 800-171 or 800-53 compliance project. The original poster thought that 60 hours to do a “gap analysis” (no fixes, just finding out what is wrong) was insane. Almost all responses agreed that that estimate was low. Many people gave estimates for the full effort involved (which includes fixes) – this was between 1,000 and 2,000 hours by a knowledgeable consultant.

CMMC level 1 and 2 should take less effort than the above estimates, but it will still be significant.

DoD Contractors – How to Prepare for the CMMC

My recommendations below are going to be a mixture of NIST SP 800-171 and the newer CMMC draft requirements. Remember that if your company deals with CUI, you should already be compliant with 800-171…start there. If not, then skip straight to the draft CMMC requirements and begin reviewing your network.

1. Ask these questions first

What security level applies to my company’s network? If you manage Controlled Unclassified Information (CUI) in any way, you have to meet at least security level 3.

Not all government contractors deal with CUI. If you aren’t sure, ask your contracting officer or read the RFP. Examples of CUI are personally identifiable information, schematics of military equipment, sensitive information about schedules and personnel, and configuration documentation for government networks.

It looks like most subcontractors won’t need the same security level as primes. But the latest news is that every DoD contractor will need to be at least CMMC level 1 in order to bid on RFPs.

As time progresses toward 2021, RFPs will specify the CMMC level requirement for bid. For existing contracts, you may be able to ask the contract officer to identify which CMMC level will apply to the renewal.

Is it possible to isolate your information to fewer systems, fewer networks, or fewer users, while still fulfilling the terms of your contract? You don’t need to secure ALL computer systems for the entire company. You just need to secure the systems that store data about the contract. Make the job easier by reducing your footprint.

Companies dealing with CUI

Is the CUI stored or accessed on your contractor information systems right now? If you have CUI on your systems now, you need to protect it according to NIST SP 800-171 requirements. It will take time before CMMC comes into effect. 800-171 is in effect now.

If you are a subcontractor – ask your prime to identify what information is CUI, and whether you NEED to store or access it using your information systems (as opposed to government systems or your prime’s systems). If you can avoid storing CUI on your own systems, do so! It reduces risk to your company (and probably will protect the data better) if you can store it elsewhere.

If you are a prime – ask your contract officer to identify what information is CUI, and whether you NEED to store or access it using your information systems (as opposed to government systems). Government systems have to adhere to very stringent requirements for cyber security. This is the best place to store CUI if you have an option.

2. Perform a Risk Assessment

Work with a cybersecurity professional who currently specializes in NIST 800-171 and have them perform a risk assessment. This assessment will review your progress toward compliance with the NIST 800-171 controls and list the ones that are deficient. Some form of vulnerability scanning and penetration testing will normally be included, with a report of findings.

Draft CMMC requirements are starting to be posted for review. While the details may change, and you might lose some work, if you want an early advantage, you should a use recent draft to audit your network.

For example, a reseller company with no CUI and very little proprietary data will probably need to attain CMMC level 1. If you review the draft requirements, they aren’t very hard to implement, but you still need to create policies, write plans, and gather evidence for your audit.

Using the NIST SP 800-171 document templates is still a valid move. If you prepare for this standard, you should have about 95% of the work done toward CMMC levels 1-3.

3. Write a Systems Security Plan

NIST provides a template for this plan here. You should describe how your information systems are secured and what policies are in place that relate to cybersecurity. This plan should give a POA&M (Plan of Action & Milestones) to resolve each deficient control. Note that you do not need to be 100% compliant with all security controls. You do need to have the most critical 17 addressed (as defined in DFARS 252.204-7012), a plan to fix the rest or explain why they don’t apply, and show progress over time.

4. Prepare for Incident Management

Make sure that you have a high quality Incident Management plan and practice it regularly. Besides implementing security controls, you are also expected to report security incidents to the DoD within 72 hours.

Make sure to register with the DoD reporting website ahead of time. The DoD will want to issue you a certificate to verify your identity, which can take a few days. The reporting website is https://dibnet.dod.mil

5. Follow Up and Continual Improvements

Ensure that your policies are realistic. Many organizations write policies that state that they will keep all systems fully patched at all times. If the organization then fails to patch systems for two months, and has an incident as a result, their failure to follow their own policy will count doubly against them. To the converse, if you have a really good reason to only patch every three months, and have written that into your policy, it might protect you against liability if there is an incident at the two month mark.

Next article: Free Incident Response template, definitions, and training scenarios

CMMC Audit Preparation Home

The CMMC Audit Preparation website is a good community resource for news and information. https://www.cmmcaudit.org/

References

NIST Special Publication 800-171 Website https://csrc.nist.gov/publications/detail/sp/800-171/rev-1/final

Federal Contractor Incident Reporting Website https://dibnet.dod.mil

System Security Plan Template https://csrc.nist.gov/CSRC/media/Publications/sp/800-171/rev-1/final/documents/CUI-SSP-Template-final.docx
Cybersecurity data analysis supporting CMMC Level 2 audit preparation for defense contractors

Talk to an Expert

Tell us where you are with compliance and we’ll map out the next steps for your team.

Don't miss these

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan
Is Your Security Plan Telling the Truth?
What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.
What Does the Government Actually Require of You Today?
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
CMMC Backup Requirements and The Myths Worth Ignoring
Server backup drives in a dark data center supporting CMMC backup requirements for a defense contractor
CMMC Backup Requirements and The Myths Worth Ignoring
How to Prepare for a DIBCAC High Assessment
Analyst reviewing evidence on dark dual monitors while preparing for a DIBCAC High assessment
How to Prepare for a DIBCAC High Assessment
Out of Scope Assets - What the Final Rule Actually Changed
Abstract data cityscape tied to out of scope assets in a CMMC assessment by Kieri Solutions
Out of Scope Assets - What the Final Rule Actually Changed
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
Dark cybersecurity image with glowing data illustrating CMMC final rule compliance for defense contractors
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
Analyst reviewing code while working toward CMMC and NIST 800-171 compliance
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
CUI Assets - What Assessors Actually Evaluate
Abstract network of nodes tied to CUI assets and CMMC scope assessed by Kieri Solutions
CUI Assets - What Assessors Actually Evaluate
Do I Even Have CUI? Understanding What You Need to Protect
Abstract data network tied to finding CUI on a defense contractor network with Kieri
Do I Even Have CUI? Understanding What You Need to Protect
Why the DoD Wants Security Protection Data Protected Like CUI
Abstract data network tied to security protection data and CMMC scope assessed by Kieri
Why the DoD Wants Security Protection Data Protected Like CUI
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Cybersecurity professional conducting CMMC gap analysis for a defense contracting organization
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Network architecture visualization for a CMMC Level 2 reference architecture built on Microsoft 365 GCC High
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Why Most CMMC Documentation Fails and How to Fix It
CMMC compliance documentation policies and procedures
Why Most CMMC Documentation Fails and How to Fix It
What Passed a DOD Assessment for System Baselining and Inventories
CMMC system inventory and baseline configuration monitoring dashboard
What Passed a DOD Assessment for System Baselining and Inventories
How to Implement Mobile Code Requirements for CMMC Level 2
CMMC mobile code security controls and technical implementation
How to Implement Mobile Code Requirements for CMMC Level 2
What Does "Monitor" Actually Mean in CMMC Requirements?
CMMC monitoring requirements - access control and password security verification
What Does "Monitor" Actually Mean in CMMC Requirements?
The Version 20 Problem and How to Avoid It
CMMC compliance documentation sequence - cybersecurity program management
The Version 20 Problem and How to Avoid It
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
CMMC Level 2 compliant environment security controls and access management
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
Inside the KCD - What Makes This Documentation Different
CMMC compliance documentation templates digital security
Inside the KCD - What Makes This Documentation Different
How the Kieri Compliance Documentation and Reference Architecture Work Together
Kieri Compliance Documentation and Reference Architecture working together for CMMC Level 2 compliance
How the Kieri Compliance Documentation and Reference Architecture Work Together
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC compliance documentation and reference architecture security controls - fingerprint scanning and access management
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC Assessments by Kieri Solutions
Global cybersecurity compliance support for defense contractors under DFARS
CMMC Assessments by Kieri Solutions
CMMC Education: User vs Network Session Termination
Secure IT infrastructure design supporting CMMC Level 2 compliance for defense contractors
CMMC Education: User vs Network Session Termination
CMMC Proposed Rule has been released! 
Cybersecurity threat - CMMC compliance
CMMC Proposed Rule has been released! 
Interested in the Kieri Compliance Documentation?
Secure data transmission within CMMC compliant network architecture
Interested in the Kieri Compliance Documentation?
How to fix Outlook missing Friday January 13 2023
Interconnected defense contractor networks requiring CMMC Level 2 cybersecurity certification
How to fix Outlook missing Friday January 13 2023
C3PAO Meeting - July 26, 2021 12-1 pm EDT
NIST SP 800-171 DoD Self Assessment Services
DFARS 252.204-7012 and NIST SP 800-171 requirements
NIST SP 800-171 DoD Self Assessment Services
vSphere Health detected new issues in your environment 6.7
vcenter 6.7 alarm displays vsphere health detected new issue
vSphere Health detected new issues in your environment 6.7
vCenter Health Warning: External Platform Services Controller
Synology storage latency and disconnects on VMware
Windows Stuck in Recovery Mode Datto driver signing
Office 365 MFA App Password Missing Fix
Microsoft Teams Conference Calls & Dial-In Numbers
C: Drive Full Exchange
Exchange server very slow, services and network blank
Exchange 2016 DAG - 3 servers 2 sites
Diagram showing mailbox servers with active and passive databases. Each database is only active on one server.
Exchange 2016 DAG - 3 servers 2 sites
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
Kieri Solutions partnering with defense contractors to achieve CMMC Level 2 certification
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
warning vsphere health detected new issue memory exhaustion 6.7 vcenter
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
Step by Step: Upgrade vCenter VCSA 6.0 (or 6.5) to 6.7
How to prepare for a DoD CMMC audit and certification
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
How to prepare for a DoD CMMC audit and certification
Fix Expired vCenter Root Password (6.5 & 6.7)
How to rename Windows Server 2016 Domain Controller
Runtime Error Adding Host in VMware vCenter & ESXi
add host a general runtime error occurred vcenter 6.5 6.7
Runtime Error Adding Host in VMware vCenter & ESXi
How to fix Netapp expired self-signed certificate by creating a new one
netapp certificate expired install site cant be reached
How to fix Netapp expired self-signed certificate by creating a new one
How to register a warranty or service agreement on HPE website
hpe hp register account SAR ID service agreement warranty how accept
How to register a warranty or service agreement on HPE website
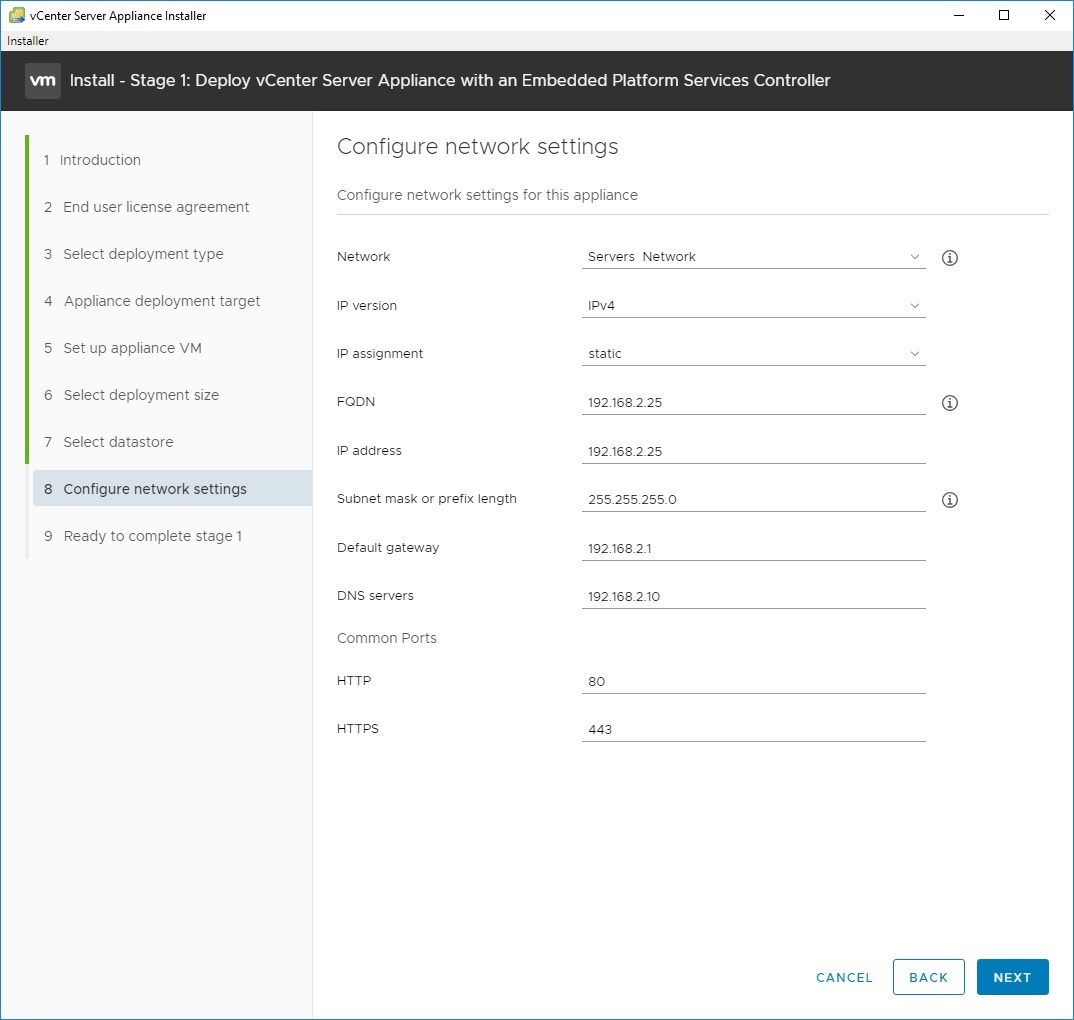
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
vcenter ip address no dns
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
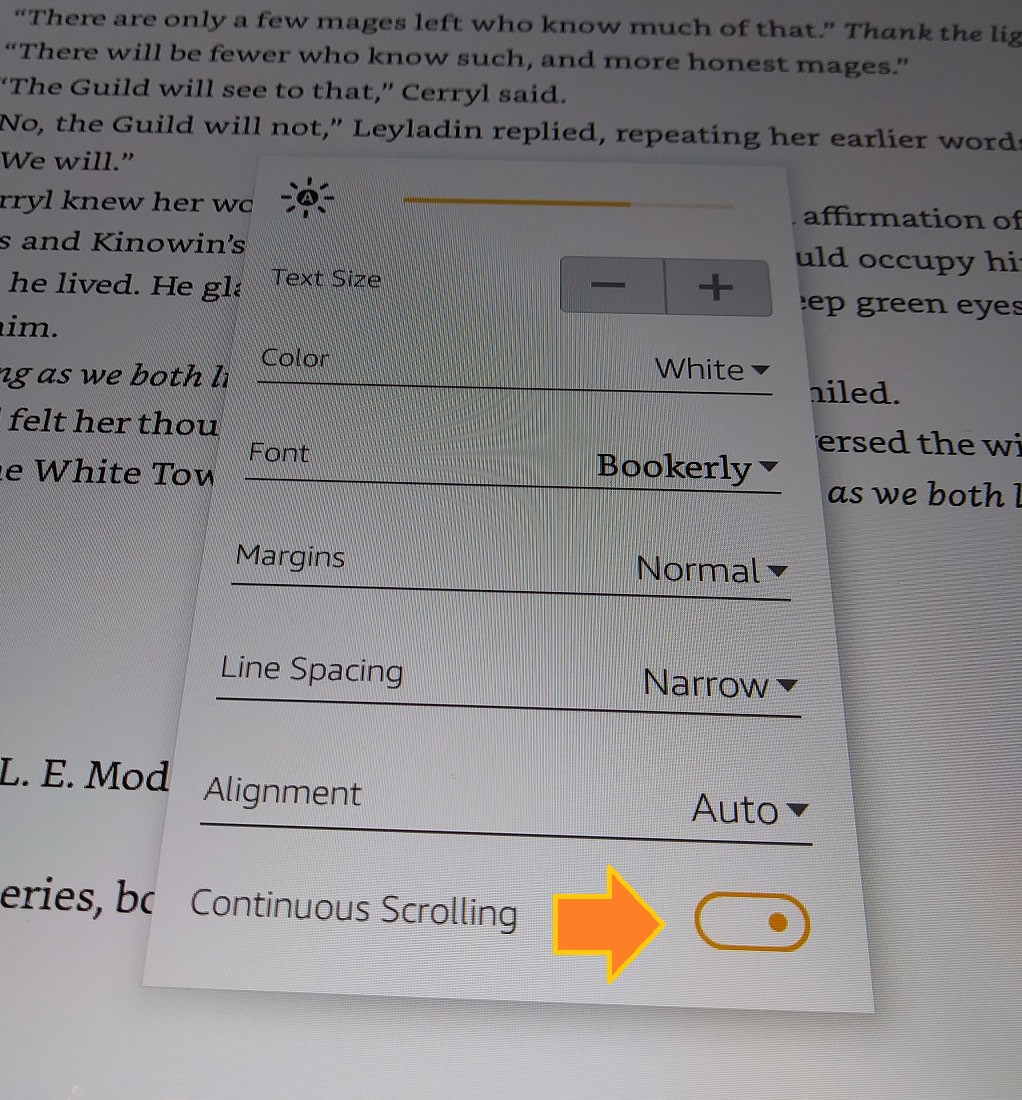
How to disable continuous scrolling on Kindle - turn on page flip
disable continuous scrolling option displays
How to disable continuous scrolling on Kindle - turn on page flip
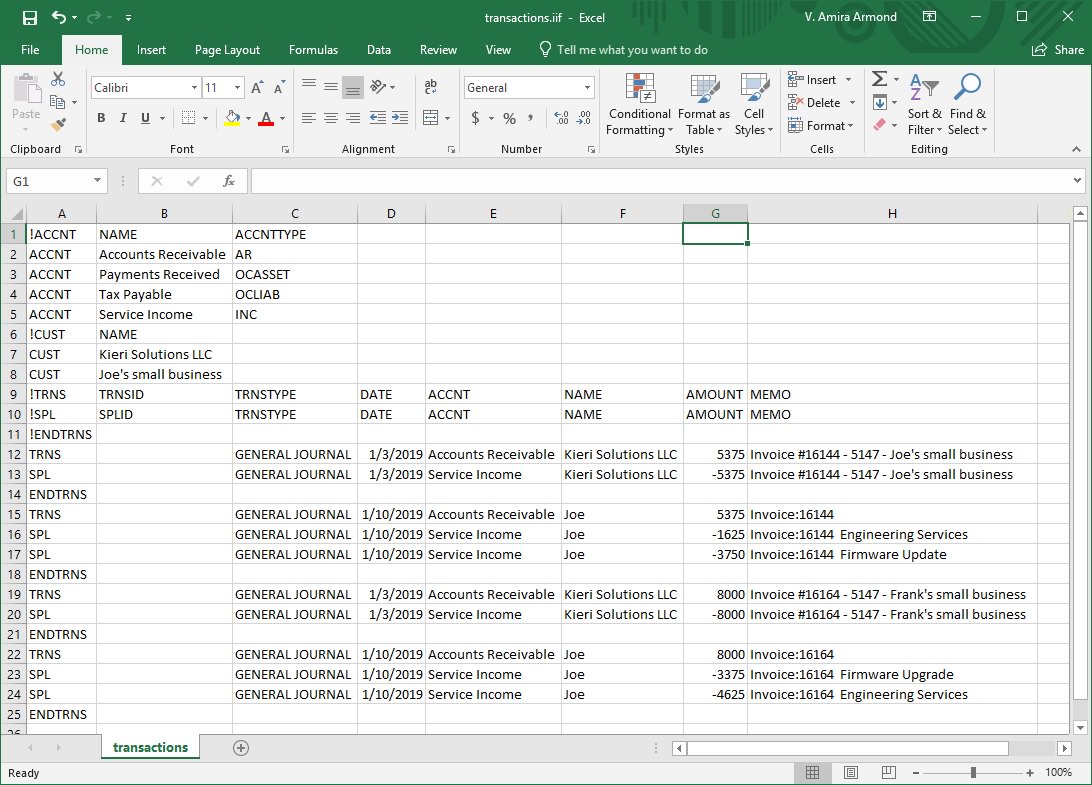
17hats how to export or convert to Excel CSV TAB XLS workbook
17hats export convert iff to csv tab excel
17hats how to export or convert to Excel CSV TAB XLS workbook
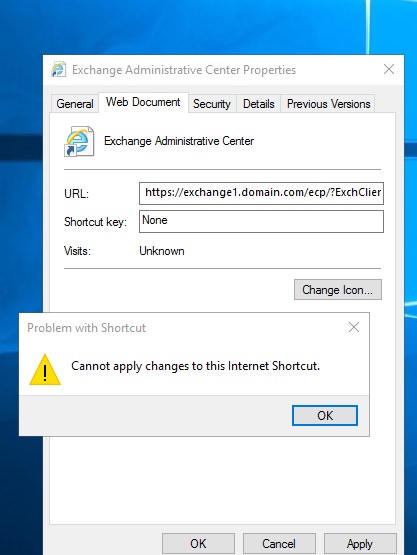
How to fix "Cannot apply changes to this Internet Shortcut" Windows
cannot apply changes to this internet shortcut 2016 2019
How to fix "Cannot apply changes to this Internet Shortcut" Windows
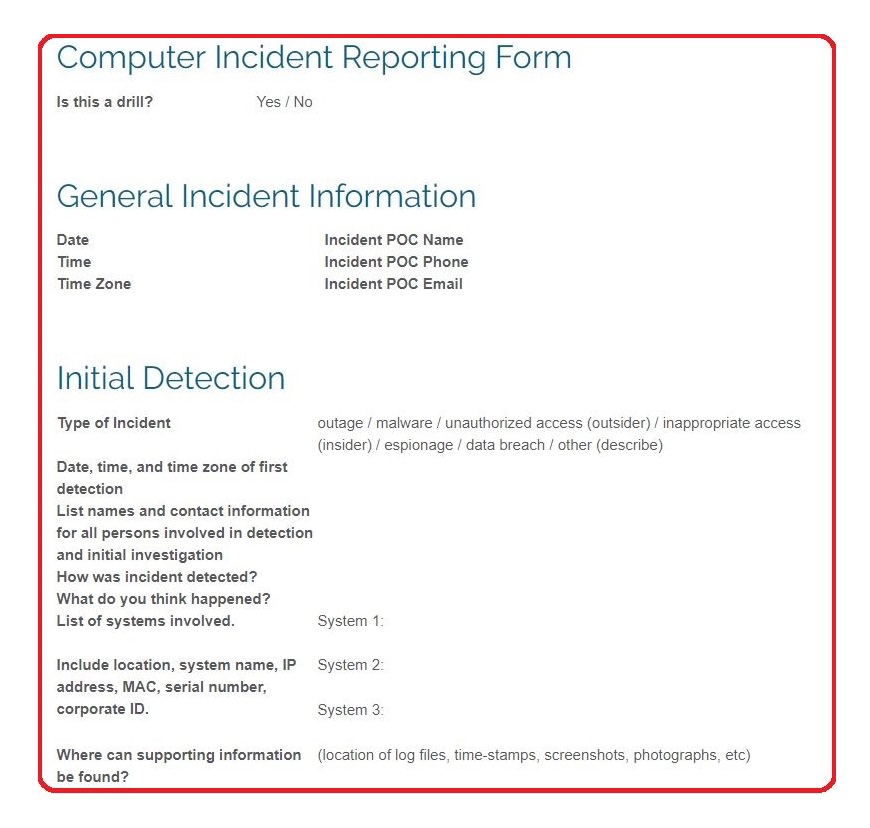
Best Free Computer Incident Response Templates and Scenarios
best free incident response reporting form cybersecurity IT
Best Free Computer Incident Response Templates and Scenarios
Firmware & System Patching Services | DC & Maryland
poweredge server raid reconfigure add disks 1 5
Firmware & System Patching Services | DC & Maryland
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
Best practice network segmentation and hardening prevents pivot attacks NIST
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Best practices and how to install esxi vsphere vcenter vmware and troubleshooting problems during the migration
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Disaster Recovery & Business Continuity in DC & Maryland
disaster recovery drp bcp hipaa frederick columbia gaithersburg baltimore rockville
Disaster Recovery & Business Continuity in DC & Maryland
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
installation services netapp disk shelf baltimore columbia rockville
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
SBDC - Intro to GDPR training - Frederick MD
intro gdpr overall sbdc fitci frederick
SBDC - Intro to GDPR training - Frederick MD
GDPR and Human Resources
cybersecurity cyber security hardening compliance firewall design frederick
GDPR and Human Resources
No, your computer isn't slow.
why slow computer pc repair frederick damascus mt airy md
No, your computer isn't slow.
Why you should consider a credit freeze - EquiFax hack
credit freeze equifax hack how to breach innovis
Why you should consider a credit freeze - EquiFax hack
Virtual Servers, Storage, and SAN - Why your servers are slow
cybersecurity compliance design consulting engineering
Virtual Servers, Storage, and SAN - Why your servers are slow
How to un-freeze your laptop like a pro
pc or computer problem repair damascus lisbon mt airy laytonsville
How to un-freeze your laptop like a pro
Upgrade your IT Services for the New Year
managed services it department outsource company frederick columbia germantown gaithersburg
Upgrade your IT Services for the New Year
Dell PowerEdge R730 PERC RAID online reconfiguration
poweredge server raid reconfigure add disks 1 5
Dell PowerEdge R730 PERC RAID online reconfiguration
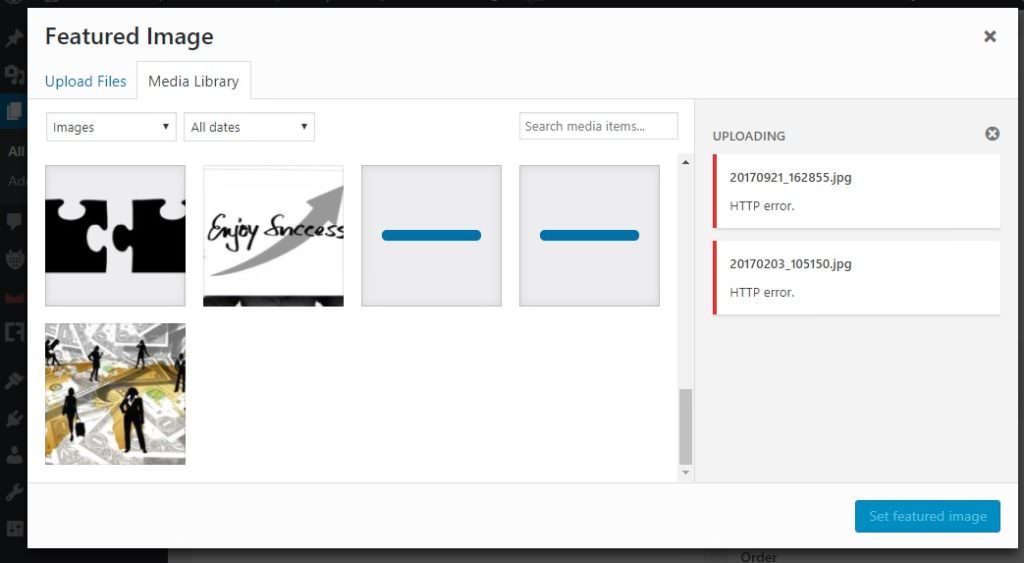
Dreamhost HTTP error Wordpress media upload and library
dreamhost http error picture disappear upload shared wordpress
Dreamhost HTTP error Wordpress media upload and library
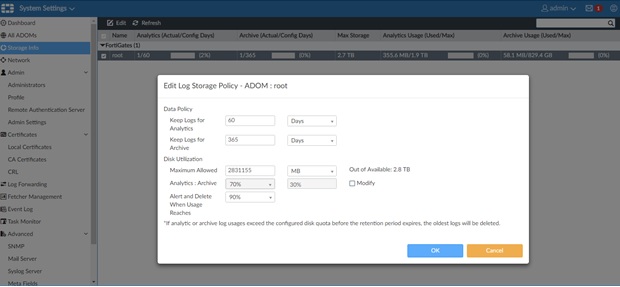
FortiAnalyzer Configuration problems after initial deploy
FortiAnalyzer 5.4 Storage Quota Limits for ADOM root
FortiAnalyzer Configuration problems after initial deploy
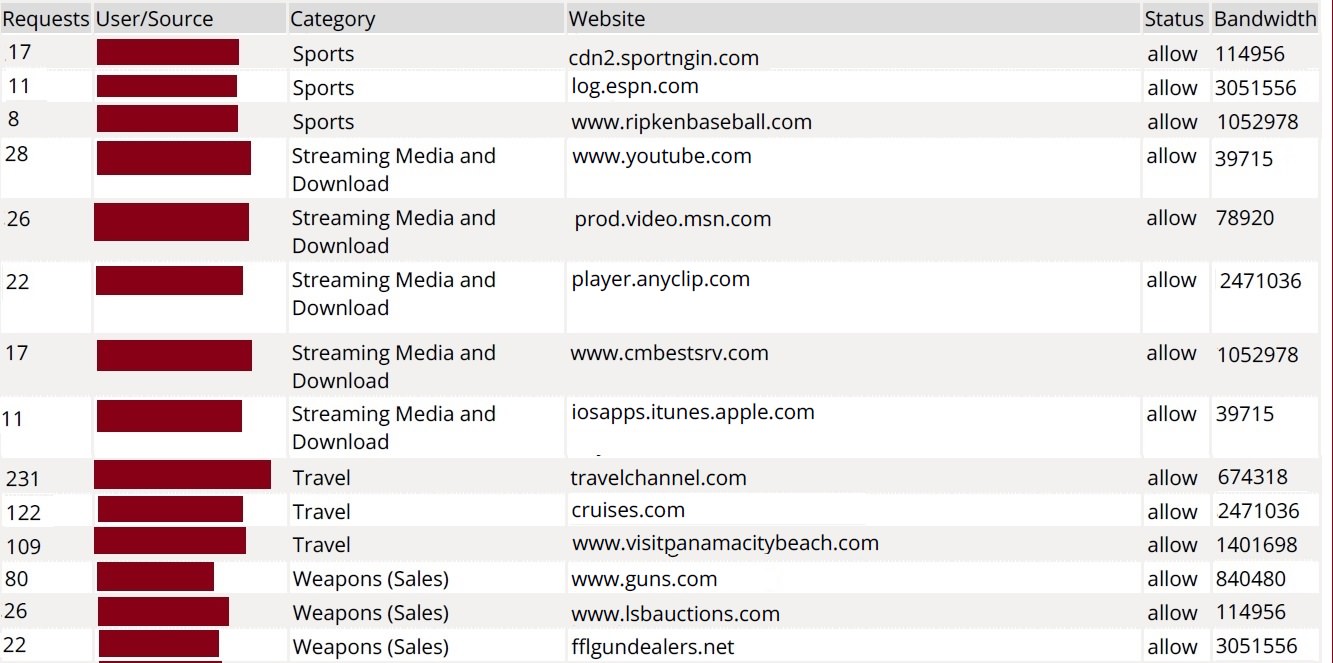
FortiAnalyzer Report: User Web Browsing by Category
fortianalyzer custom report users by category who is browsing web goofing off
FortiAnalyzer Report: User Web Browsing by Category
GDPR Consulting - What you need to know
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
GDPR Consulting - What you need to know
The #1 Computer Security Threat Just Evolved - RCE Worm
cybersecurity cyber security compliance firewall frederick md
The #1 Computer Security Threat Just Evolved - RCE Worm
Fix vSphere & vCenter Datastore Size Reverting
security design cybersecurity consulting services compliance
Fix vSphere & vCenter Datastore Size Reverting
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
conflicting vibs error vsphere upgrade metadata consultant vmware
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
Is your IT person holding the network hostage?
Server Upgrade Cybersecurity Consultant SAN Netapp Frederick
Is your IT person holding the network hostage?
4 Hiring Mistakes When Choosing an IT Company
mistakes when hire IT consultant MSP managed service provider computer support outsourcing
4 Hiring Mistakes When Choosing an IT Company
What you should know about Cloud Computing and Office 365
cloud IT department migration Office 365 Frederick Baltimore Columbia MD
What you should know about Cloud Computing and Office 365
Can You Make Our Nation Safe from Hackers?
The Ultimate Way to Protect Against Computer Theft
Kieri Solutions site icon
The Ultimate Way to Protect Against Computer Theft
Small / medium business security concerns
managed services it department outsource company frederick columbia germantown gaithersburg
Small / medium business security concerns
Approaches to security policy
cybersecurity cyber security hardening compliance firewall design frederick
Approaches to security policy

Article

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan

Article

What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.

Article

NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3

No one wants to start from blank templates.

No one wants to start from
blank templates.

Stop starting from blank templates. Get documentation proven through actual CMMC Level 2 assessment.