
The #1 Computer Security Threat Just Evolved – RCE Worm
Let me tell you a story about a worm.
This worm’s name was Welchia, and it came into the world late one night in mid-2003.
I was early career IT at that time, working Tier 2 Helpdesk in a very large (hundreds of thousands of users) enterprise. We had server farms across the world and I did normal things like resetting user profiles, fixing file shares, and repairing programs.
One morning, I was managing a server overseas when it abruptly went offline. I tried to reach the other servers at that site and none of them responded. Other employees around me confirmed that the network link was down.
About one minute later, I lost my connection to the server farm on the west coast. At this point, we started to get alarmed.
Then a few seconds later, server farms in the mid-USA went offline.
We are now in full panic mode. Is this World War III? Are we under attack?
And then two things happened simultaneously – our own computers lost connection to…
And then two things happened simultaneously – our own computers lost connection to our local servers, and a red flashing warning appeared on every screen in the building simultaneously: “VIRUS DETECTED: welchia.worm”
It took months to get our network back to normal.
That story is typical for what happens when a worm is released into the public. Worms are a very special type of virus which don’t need any human interaction to spread. They use un-patched vulnerabilities in computer software to inject themselves into a computer, take it over, then send copies to other computers. The spread is very fast. Too fast for antivirus definitions to update. Too fast to shut off your computer.
In the case of Welchia, this worm was actually a “friendly” program. It did nothing harmful except to propagate itself. But when you have thousands of computers trying to send copies of a worm to each other, it overwhelms the network circuits.
Can you imagine the destruction if the worm wasn’t friendly? If it told each computer to shred its own files? There would have been a lot of companies in complete shutdown.
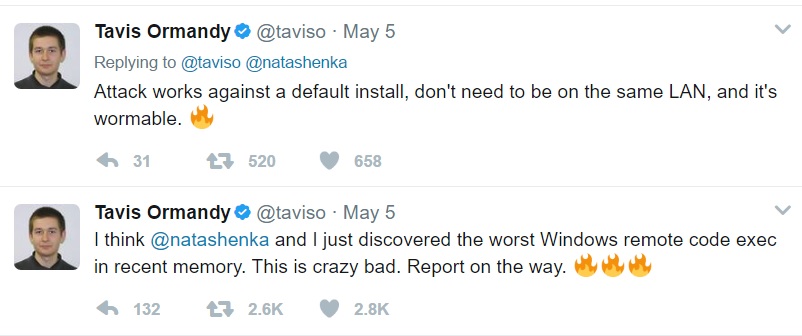
Last week a pair of Google Project Zero researchers found a vulnerability in all Windows 7, 8.1, and 10 computers that could be exploited by a worm. They reported it to Microsoft and a patch was developed in three days (beating all speed records). But only people who have automatic updates working, or those who know how to manually pull patches, will get the patch.
If your business doesn’t have an IT person watching out for patching, I would be very alarmed about this vulnerability. Now that it is public knowledge, it is only a matter of time before a worm is released. Get patched!
Link to Microsoft patch for the RCE vulnerability: https://technet.microsoft.com/en-us/library/security/4022344.aspx
Link to TheHackerNews article about the vulnerability and patch release: http://thehackernews.com/2017/05/windows-defender-rce-flaw.html
Link to TheHackerNews article about the initial vulnerability finding: http://thehackernews.com/2017/05/windows-rce-exploit.html