Why logging isn’t enough and what assessors actually look for
The word “monitor” appears approximately 250 times in the CMMC Level 2 assessment guide. That’s twice as many times as “logging.”
Yet many defense contractors treat these terms as interchangeable. They capture logs and assume they’re monitoring. They’re not.
This distinction matters because assessors specifically verify monitoring capability. Having logs isn’t enough. You need to demonstrate that someone or something is actually watching those logs and can react when problems appear.
The Fundamental Difference Between Logging and Monitoring
Logging means capturing data. Your systems record events, your firewalls track traffic, your servers document who logged in and what they accessed.
Monitoring means acting on that data. Someone reviews the logs. Something scans for anomalies. When bad activity appears, it gets escalated.
Think of it this way: a security camera recording to a hard drive is logging. A guard watching the monitors is monitoring.
You can log everything perfectly and still fail monitoring requirements. If nobody ever looks at those logs, if no process exists to detect and respond to issues, you’re not monitoring.
Due Care Means Knowing What’s Happening
One of our assessors describes monitoring as due care and due diligence. You care about security, so you want to see what’s actually happening. You don’t just assume everything is fine.
There’s an old saying that applies perfectly here: don’t expect what you don’t inspect.
If you expect your access controls to work but never verify them, you might be surprised to learn they’ve been misconfigured for months. If you expect users to follow security policies but never check, you might discover widespread violations when it’s too late.
Monitoring is the inspection. It’s how you verify that your expectations match reality.
What Assessors Actually Look For
During assessments, we verify monitoring in a specific way. We ask to see your monitoring process. We ask you to demonstrate it.
Here’s what reveals whether you actually monitor: can you pull up the monitoring screen quickly?
If you check something daily, you know exactly where to find it. You don’t hesitate. You don’t search through menus. You go directly to the dashboard or report you use every day.
If you struggle to find where monitoring happens, that tells us you don’t actually look at it regularly. The process might exist on paper. The capability might be configured. But nobody is using it.
This is a telltale sign assessors watch for. Familiarity demonstrates practice. Hesitation suggests the monitoring exists only for the assessment.
If You See Something, Say Something
Monitoring isn’t just observation. It’s observation with the capacity to respond.
Capturing network traffic is logging. Having someone review that traffic and escalate suspicious patterns is monitoring. The difference is the human element, the decision-making, the ability to act.
This applies whether you use human eyes or automated systems. A SIEM that scans logs and generates alerts counts as monitoring if someone responds to those alerts. A dashboard that displays information but triggers no action when problems appear isn’t really monitoring.
The key question: if something bad happened, would your monitoring detect it and get it escalated?
Identify, Control, and Monitor Are Three Separate Things
Assessment objectives often include three components: identify how you’re doing something, control it, and monitor it.
These aren’t redundant. They’re three distinct activities that might involve three different people.
Identify means documenting your approach. This is often your compliance lead or GRC team explaining policies and procedures.
Control means implementing technical or administrative measures. This is often your IT team configuring Group Policy, firewalls, or access permissions.
Monitor means verifying controls work and detecting when they don’t. This is often your security operations or incident response team reviewing logs and dashboards.
When scheduling assessment interviews, make sure the right person is available for each component. The person who wrote the policy might not be the person who configured the control or the person who monitors its effectiveness.
Why “We Control It So We Don’t Need to Monitor” Fails
This is one of the most common mistakes we see.
Organizations say they don’t need to monitor certain activities because they’ve controlled them. USB drives are disabled through Group Policy. Users can’t enable WiFi on managed devices. Macros are blocked in Office applications.
Therefore, they argue, there’s nothing to monitor. The bad thing can’t happen.
This misses the point entirely.
Controls can fail. Group Policy can be misconfigured. Exceptions can be granted and forgotten. Devices can fall out of management. Users can find workarounds.
Monitoring verifies that controls remain effective. It answers the question: how do you know your controls are actually working?
Even if you expect zero violations, you need a process that would detect violations if they occurred. You need to periodically confirm that zero violations is the reality, not just the assumption.
Showing Monitoring Capability with Zero Results
This raises a practical question. If your controls are effective and violations don’t occur, how do you demonstrate monitoring?
The answer is showing the monitoring function, not the results.
If you have a query that would detect USB device connections, show the query. Run it. If it returns zero results, that’s fine. The point is that the query exists and you run it regularly.
If you have a dashboard that would display WiFi enablement attempts, show the dashboard. If it’s empty, that’s fine. The point is that you check it.
You don’t need to disable security controls and create violations just to have something to monitor. You need to demonstrate that your monitoring capability exists and would work if violations occurred.
Document when you run these checks. Keep records showing the date, what you checked, and what you found (even if the finding is “no issues detected”). This creates evidence that monitoring actually happens.
Human Eyes vs Computer Eyes
Monitoring doesn’t require a person staring at a screen constantly. Automated monitoring counts if it’s configured properly.
A SIEM that analyzes logs and generates alerts for suspicious patterns is monitoring. An automated script that runs queries and emails results to security staff is monitoring. A cloud service that watches for specific events and creates tickets is monitoring.
The key is that someone receives notification when problems appear and has responsibility to respond.
What doesn’t count: logs accumulating on a server that nobody ever reviews. Dashboards that display information nobody looks at. Alerts that go to an inbox nobody checks.
Automation can do the watching. Humans need to handle the response.
How do you know who accessed your server room? How do you verify visitor logs are accurate? How do you detect unauthorized access attempts to sensitive areas?
The same principles apply. Logging physical access isn’t enough. Someone needs to review those logs, look for anomalies, and respond when something seems wrong.
Badge access systems generate logs automatically. Monitoring means reviewing those logs periodically, investigating unexpected after-hours access, and following up on access attempts by people who shouldn’t be in certain areas.
Personnel Security Monitoring
Monitoring also applies to people. How do you detect insider threats? How do you identify users who might be violating security policies?
This might involve reviewing access patterns for unusual behavior. Checking if users are accessing systems or data they don’t need for their jobs. Watching for large data transfers or unusual working hours.
The assessment objectives mention monitoring for user misbehavior. You need some mechanism to detect when users behave in ways that could indicate security problems.
This is sensitive territory. Balance security monitoring with privacy and employee trust. But some level of monitoring for unusual activity is expected.
Making Monitoring Sustainable
Daily monitoring sounds exhausting. How do you actually sustain it?
Automate What You Can
Configure systems to alert you when specific conditions occur. You don’t need to review every log entry manually. You need to be notified when something unusual happens.
Set thresholds that trigger alerts. Multiple failed login attempts. Access outside normal hours. Large file transfers. Connections to unusual destinations.
Create Dashboards for Regular Review
Build dashboards that summarize what matters. Instead of scrolling through thousands of log entries, view aggregated metrics that highlight anomalies.
Review dashboards daily or weekly depending on the metric. Document your reviews to create evidence.
Assign Clear Responsibility
Someone specific needs to own each monitoring activity. “Everyone is responsible” means nobody does it.
Assign names to monitoring tasks. Include them in job descriptions. Track completion.
Build Monitoring into Routine
Monitoring works best as habit, not special activity. Check the security dashboard when you start work each morning. Review access logs during weekly staff meetings. Include monitoring status in monthly reports.
Regular routines are sustainable. Special efforts for assessments are not.
Evidence That Demonstrates Monitoring
What evidence should you prepare for assessment?
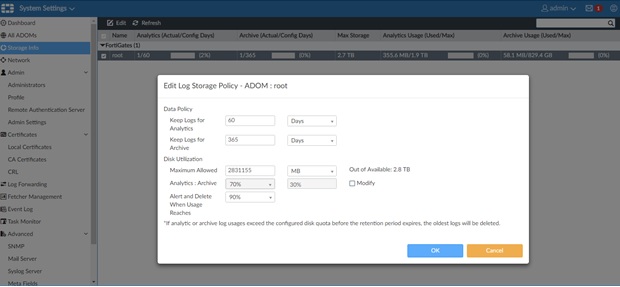
Screenshots of dashboards and reports you regularly review. Include dates showing ongoing activity, not just assessment preparation.
Documented procedures for monitoring activities. Who does what, how often, and what they look for.
Records of completed monitoring activities. Logs showing when dashboards were accessed, reports were run, or reviews were completed.
Examples of issues detected and escalated. If monitoring found something, show how you responded.
Evidence of monitoring even when nothing was found. Records showing you checked and found no issues still demonstrate active monitoring.
Common Monitoring Mistakes
Confusing Logging with Monitoring
Logs exist but nobody reviews them. The capability is there. The practice isn’t.
Monitoring Only During Assessments
Suddenly everyone checks dashboards when assessors arrive. That’s not monitoring. That’s performing for an audience.
No Documentation of Monitoring Activities
You review logs daily but have no record of it. When assessors ask for evidence, you can’t prove ongoing monitoring.
Wrong Person at the Interview
The compliance lead explains monitoring but can’t demonstrate it because the security team actually does it. Make sure the right people are available.
Assuming Controls Eliminate Monitoring Need
Controls reduce risk. Monitoring verifies controls work. Both are required.
Getting Your Monitoring Processes Right
Monitoring requirements run throughout CMMC. Getting this right requires understanding what assessors actually verify and building sustainable processes.
Download the free KCD brochure at kieri.com/kcd for documentation templates that address monitoring requirements correctly.
Watch our full discussion to hear how assessors evaluate monitoring during real assessments.
Kieri Solutions is one of 54 authorized C3PAOs in the United States. Our team conducts real CMMC assessments and knows exactly what we look for when verifying monitoring capabilities.