Open navigation menu - Kieri Solutions
Disaster Recovery & Business Continuity in DC & Maryland

Disaster Recovery & Business Continuity in DC & Maryland

disaster recovery drp bcp hipaa frederick columbia gaithersburg baltimore rockville

In this article

โ€œ

โ€œTwo out of every five companies struck with a major disaster are unable to recover. Of the survivors, one third go out of business within the next two years.ย โ€

โ€” Gartner Study โ€“ 1996


Availability and Integrity โ€“ why you need Business Continuity Plans and Disaster Recovery Plans.

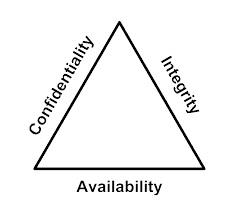
Did you know that Information Security considers โ€œAvailabilityโ€ and โ€œIntegrityโ€ to be just as important as โ€œConfidentialityโ€?ย  ย  If your IT systems go down or your data is lost, it will be just as serious for your business as if you were โ€˜hackedโ€™.

Availability means โ€œYour users can access your systemsโ€. They are able to work. Without availability, you have nothing. Failover, redundancy, and quality systems design affects your availability.

Integrity means โ€œYou have data, and it is good data.โ€ Some cyber-attackers focus on corrupting business data, then demand a โ€œransomโ€ to restore it. If your data is destroyed, will you be able to perform work? Backups and segmenting your sensitive data from the rest of the network are big ways to improve integrity.

Confidentiality means โ€œOnly the right people are accessing your systems.โ€ This is the focus of most cyber-security efforts, and ironically, has the least impact on whether your business can function.

Do you see how availability and integrity are just as important, or more important, than confidentiality? We focus on availability and integrity for this reason.
integrity confidentiality availability cybersecurity triad

What are these plans for?

We write this plan to be used when you are having a very bad day.

โ€“ Amira Armond, President of Kieri Solutions

During normal timesโ€ฆ

When there is no hurricane, these plans are used primarily to show that your business is being proactive about risks.ย 

They are a required component of many cyber-security compliance frameworks and are required by law for some types of businesses, particularly medical providers.ย 

Many businesses are asked by their customers to provide public-facing Business Continuity Plans (BCPs) to show that they are responsible partners and will be capable of operating in the future.ย 

The process of writing a plan and reviewing it will make your business more resilient.ย  Often we find issues such as missing backups, no identified alternative site, or lack of a communications plan.ย  Before finalizing the plan, we will work with your team to fix these issues.

During emergenciesโ€ฆ

When something goes horribly wrong, these plans are designed to help your staff respond appropriately, even if the lights are out.ย  ย 

The plan will remind you to do things like communicate with news organizations (depending on your business) or give contact information to reach your insurance company.ย 

The plan will either have step-by-step instructions to perform recovery, or it will point you to the correct procedures document to use.ย 


The best way to get management excited about a disaster plan is to burn down the building across the street. โ€” Dan Erwin, Security Officer, Dow Chemical Co.ย 


What is the difference between a Business Continuity Plan and a Disaster Recovery Plan?

Business Continuity Plans cover more aspects of your operations.ย  ย Most IT compliance frameworks like HIPAA require a Business Continuity Plan, not a Disaster Recovery Plan.ย 

The business continuity plan will include getting your critical information systems online, ideally through fail-over, but also focuses on how your employees will be able to continue providing services.

A business continuity plan addresses these topics:

  • Description of your business operations and critical IT systems
  • Identifies risks that can impact your ability to do business.ย  If your business is considered critical infrastructure (such as a public utility or medical provider), we consider more risks.ย  Each risk is evaluated for likelihood and impact. Examples include:
    • Pandemic (for critical infrastructure)
    • Regional disruption such as flooding or hurricane, which causes your employees to evacuate
    • Building disruption such as fire or power outage
    • Physical attacker or bomb threat (depending on type of business)
    • Information system disruption such as ransomware or cyber-attack
  • Identifies plans and procedures to continue operations during several scenarios.ย  For example, a critical medical provider might coordinate with the police department and emergency medical services to set up temporary operations in a public space.
  • Communication plans for coordinating with internal employees, customers, and the public.
  • Contacts used during an emergency, such as police, hospitals, corporate insurance, and corporate attorneys.

Disaster Recovery Plans (DRPs) generally focus more on IT systems rather than overall business operations.

A disaster recovery plan addresses these topics:

  • Identify specific operations (normally IT systems) which are the focus.
  • Identify risks that impact your IT systems such as:
    • Specific system failures (such as a server crashing)
    • Server room disruption (fire, flooding, power outage)
    • Cyber-attack requiring rebuild of your IT systems
    • User error requiring recovery of data
  • Details about how your IT systems are backed up and procedures to perform backups and test these backups.
  • Plans for how to fail over operations, move to a new site, or recover your systems.

How much will downtime cost your business?

Check out this recovery calculator from Datto.com.ย  Enter your variables (average employee salary, revenue, etc) to find out how much a critical system outage can cost your business.
columbia rockville frederick baltimore md disaster recovery

I do not fear computers. I fear the lack of them. โ€” Isaac Asimov


Stakeholders for your Business Continuity Plan

Why are we talking about stakeholders?ย  Isnโ€™t the IT guy responsible for disaster recovery?ย  ย  ย  The answer is no.ย  If you are leaving all responsibility on your IT person, you are being unfair to them.ย  ย Making your business resilient takes C-level input because it is highly dependent on corporate strategy, goals, and budgeting.

Officers

Your corporate officers should identify how important IT systems are to the company.ย  Can the business survive without them for a week?ย  How about a day?ย  Would it cause front-page news if customers couldnโ€™t access their services?ย  What about losing data?ย  Could your company survive if the last 8 hours of changes to the data were lost?ย  ย These questions are highly dependent on the company type.ย  Amazon Web Services cannot afford to lose data or have even a few minutes of outage.ย  A construction company might be able to absorb a few days of outage without their customerโ€™s noticing.

Other departments

In larger companies, it is common for IT to maintain a server that they donโ€™t know much about.ย  The โ€œmarketing department uses itโ€.ย  Without input from each department, you wonโ€™t know how critical a system is, and what level of continuity is needed.ย  This feedback should go up the chain to the corporate officers for prioritization.

CIO

You also need a leadership role for your IT department, such as a CIO.ย  This person understands how much your IT department can do, and what it should be doing.ย  For example, it is entirely possible for a 100 person company to operate with just one (fast) IT person.ย  But if life get hectic, the first thing to fall through the cracks are the preventative tasks and maintenance.ย  Things like installing security patches, using processes to control system changes and document configurations, and backing up systems.ย  Your CIO can add staff, bring in consultants, or prioritize tasks to make sure that prevention work happens. In addition, your CIO should schedule irregular tasks like testing backups, performing failovers, and running incident response drills.ย  If leadership doesnโ€™t champion drills and testing, they tend to be forgotten.

IT Department

Finally, we get to the IT staff.ย  They do most of the heavy lifting; engineering and designing solutions to meet the corporate goals.ย  They are responsible for making sure that each system has a recovery plan, and updating it over time.ย  They should also periodically (quarterly or monthly) attempt to use these recovery procedures.ย  Your IT staff are responsible for making sure that the design and procedures are realistic.ย  Without this sanity check, a disaster recovery plan is much less effective.


Why choose Kieri Solutions to write your plan?

We are local to businesses in DC, Frederick, Baltimore. Rockville, Gaithersburg, and Columbia MD.

We think that Business Continuity Plans and Disaster Recovery Plans should be more than a piece of paper.ย  Your Disaster Recovery Plan should have detailed procedures to follow to get your operations running again.ย  Your Business Continuity Plan should have insurance policy numbers, contact information for your vendors, communications templates, and a well thought out risk assessment and response to a large number of possible incidents.

We research, train, prepare, and test the ability to recover from the unexpected.

Our staff just came back from a Cyber War Training event in North Virginia.ย  Our employees have been doing DoD-level disaster recovery and fail over (they call it โ€œContinuity Of Operationsโ€) planning, testing, and support since 2005.ย  In our careers, we have coordinated enterprise fail-overs, recovered hundreds of failed servers, and designed secure military networks to handle infrastructure attacks automatically.
rockville md business continuity frederick baltimore

We will suggest improvements

If there are glaring problems such as the backups are not enabled, or certain technologies are known to fail often, or if the proposed response to an incident would not be effective, we will give you a heads up.ย  If you want help, we can help implement most fixes.ย  For example, while writing recent a BCP, we discovered that two critical systems were not encrypted per HIPAA requirements, and one system wasnโ€™t being backed up.ย  We worked with company engineers to fix the problems before finalizing the BCP.


How does the DR / BCP process work?

A systems architect who specializes in โ€˜Resilient ITโ€™ will be assigned to your business.

There will be an initial call with your management to identify the scope of the plan (for example, do you only want to focus on one critical system, or all business operations?).ย  ย We will also work with management to identify key service levels such as the amount of time a system can be down and how much data can be lost.

We will brainstorm a list of possible business impacts (such as hardware failure, flood, cyber incident, and more).ย  This helps guide the questions later.

There will be several calls, in-person visits, or screen shares with your technical experts to gather data about how the system is designed, how it is backed up, and what failover or redundancies are configured.ย  We will also talk through various scenarios to see how the company would respond.

We will research the risk of each type of incident.ย  For example, we might check flood histories in your area or research the failure rate of your network devices.ย  We will also make architectural diagram(s) to show critical systems and dependencies for your operations to continue.

Through this process, we will be drafting a business continuity or disaster recovery plan.ย  ย The next step is normally identifying exact procedures to recover operations.ย  Your IT staff might provide these procedures, we might research vendor documentation to find them, or we might work with your IT staff to discover the best method.

Around now, your BCP or DRP is version 1.0.

We highly recommend testing the procedures and other information in the plan (such as contact numbers for your vendors) as soon as possible.ย  Invariably, testing will identify missing steps or faulty equipment.ย  The easiest form of testing is called a โ€œtabletop exerciseโ€.ย  This is where we run a scenario and talk through each step.ย  For example, we might move from discovery of a problem (who do you report it to?), to pulling in experts (internal and external), walking through how we would notify clients, and calling the insurance company.

If you are willing, we will work with your system administrators to performย  test fail-overs and restores from backup.ย  If gaps are found, we will help you solve them, either by updating the procedures or re-engineering systems.

Schrodingerโ€™s Backup: โ€œThe condition of any backup is unknown until a restore is attempted.โ€

Tip: Put โ€˜realโ€™ information in your plan.

This is information that is used if something really goes wrong (such as insurance policy information or procedures to restore from backup).ย  You may want to create a second, public-facing plan which has sensitive information removed.ย  This public facing plan can be provided to your clients to prove that your company is being responsible and diligent.

You will want to have copies of your plan printed out at multiple locations. If you canโ€™t get to the office, the plan will help you contact vendors and insurance. It will remind you to do things like communicate with your customers or news organizations. And it will guide you in recovery procedures when things have gone wrong.

kieri solutions IT consultant service provider cybersecurity logo

We have the experience with databases, cloud, virtualization, backups, SAN, networking, server hardware, and other technologies used by your business.

Kieri Solutions is at our heart a systems engineering company.ย  We are used to designing and implementing solutions for real companies that want Resilient IT.ย  So when we talk to your IT staff, it will be peer-to-peer, not a disappointing process of trying to explain concepts to a non-technical person.

We are local, and will be available to support in the future.

When you fly in a consultant from a big name company, you will probably never meet that person again.ย  ย In contrast, once we have performed a project for you, we stand by our work and will respond if you have problems later on.ย  ย We will also remember you and your network โ€“ you wonโ€™t be starting from scratch with us.

Our rates are typically half that of a big-name company.

Since we donโ€™t need to fly our employees around, and because we have a smaller footprint, we donโ€™t need to charge crazy rates.ย  We will be glad to give you a no-risk estimate.R

Email us: info@kieri.com

Call us: (301) 253-5150

Examples of recent projects

  • Write HIPAA-compliant business continuity plans for medical providers.
  • Install Veeam Backup & Restore suite for VMware and Windows servers. Train staff to recover from various scenarios (file-level restore, server-level restore).
  • Design disaster recovery site and test ability to quickly recover from Ransomware and other scenarios.
  • Use Netapp SnapRestore and Snapshot technology to recover large (4TB+) virtual machines in 1-2 minutes.
  • Identify missing backups and lack of redundancy during SaaS business continuity planning, work with engineers to resolve before finishing BCP.
  • Configure and successfully test cloud restores using Datto and Office 365.
  • Create Continuity Of Operations Plans (COOP) (DoD specific disaster recovery plan) for US Navy deployed hospital systems.
Cybersecurity data analysis supporting CMMC Level 2 audit preparation for defense contractors

Talk to an Expert

Tell us where you are with compliance and weโ€™ll map out the next steps for your team.

Don't miss these

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan
Is Your Security Plan Telling the Truth?
What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.
What Does the Government Actually Require of You Today?
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
CMMC Backup Requirements and The Myths Worth Ignoring
Server backup drives in a dark data center supporting CMMC backup requirements for a defense contractor
CMMC Backup Requirements and The Myths Worth Ignoring
How to Prepare for a DIBCAC High Assessment
Analyst reviewing evidence on dark dual monitors while preparing for a DIBCAC High assessment
How to Prepare for a DIBCAC High Assessment
Out of Scope Assets - What the Final Rule Actually Changed
Abstract data cityscape tied to out of scope assets in a CMMC assessment by Kieri Solutions
Out of Scope Assets - What the Final Rule Actually Changed
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
Dark cybersecurity image with glowing data illustrating CMMC final rule compliance for defense contractors
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
Analyst reviewing code while working toward CMMC and NIST 800-171 compliance
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
CUI Assets - What Assessors Actually Evaluate
Abstract network of nodes tied to CUI assets and CMMC scope assessed by Kieri Solutions
CUI Assets - What Assessors Actually Evaluate
Do I Even Have CUI? Understanding What You Need to Protect
Abstract data network tied to finding CUI on a defense contractor network with Kieri
Do I Even Have CUI? Understanding What You Need to Protect
Why the DoD Wants Security Protection Data Protected Like CUI
Abstract data network tied to security protection data and CMMC scope assessed by Kieri
Why the DoD Wants Security Protection Data Protected Like CUI
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Cybersecurity professional conducting CMMC gap analysis for a defense contracting organization
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Network architecture visualization for a CMMC Level 2 reference architecture built on Microsoft 365 GCC High
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Why Most CMMC Documentation Fails and How to Fix It
CMMC compliance documentation policies and procedures
Why Most CMMC Documentation Fails and How to Fix It
What Passed a DOD Assessment for System Baselining and Inventories
CMMC system inventory and baseline configuration monitoring dashboard
What Passed a DOD Assessment for System Baselining and Inventories
How to Implement Mobile Code Requirements for CMMC Level 2
CMMC mobile code security controls and technical implementation
How to Implement Mobile Code Requirements for CMMC Level 2
What Does "Monitor" Actually Mean in CMMC Requirements?
CMMC monitoring requirements - access control and password security verification
What Does "Monitor" Actually Mean in CMMC Requirements?
The Version 20 Problem and How to Avoid It
CMMC compliance documentation sequence - cybersecurity program management
The Version 20 Problem and How to Avoid It
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
CMMC Level 2 compliant environment security controls and access management
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
Inside the KCD - What Makes This Documentation Different
CMMC compliance documentation templates digital security
Inside the KCD - What Makes This Documentation Different
How the Kieri Compliance Documentation and Reference Architecture Work Together
Kieri Compliance Documentation and Reference Architecture working together for CMMC Level 2 compliance
How the Kieri Compliance Documentation and Reference Architecture Work Together
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC compliance documentation and reference architecture security controls - fingerprint scanning and access management
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC Assessments by Kieri Solutions
Global cybersecurity compliance support for defense contractors under DFARS
CMMC Assessments by Kieri Solutions
CMMC Education: User vs Network Session Termination
Secure IT infrastructure design supporting CMMC Level 2 compliance for defense contractors
CMMC Education: User vs Network Session Termination
CMMC Proposed Rule has been released!ย 
Cybersecurity threat - CMMC compliance
CMMC Proposed Rule has been released!ย 
Interested in the Kieri Compliance Documentation?
Secure data transmission within CMMC compliant network architecture
Interested in the Kieri Compliance Documentation?
How to fix Outlook missing Friday January 13 2023
Interconnected defense contractor networks requiring CMMC Level 2 cybersecurity certification
How to fix Outlook missing Friday January 13 2023
C3PAO Meeting - July 26, 2021 12-1 pm EDT
NIST SP 800-171 DoD Self Assessment Services
DFARS 252.204-7012 and NIST SP 800-171 requirements
NIST SP 800-171 DoD Self Assessment Services
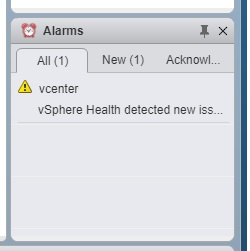
vSphere Health detected new issues in your environment 6.7
vcenter 6.7 alarm displays vsphere health detected new issue
vSphere Health detected new issues in your environment 6.7
vCenter Health Warning: External Platform Services Controller
Synology storage latency and disconnects on VMware
Windows Stuck in Recovery Mode Datto driver signing
Office 365 MFA App Password Missing Fix
Microsoft Teams Conference Calls & Dial-In Numbers
C: Drive Full Exchange
Exchange server very slow, services and network blank
Exchange 2016 DAG - 3 servers 2 sites
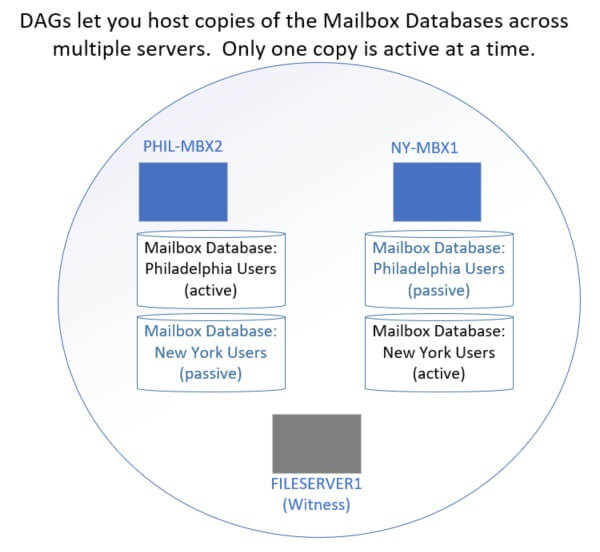
Diagram showing mailbox servers with active and passive databases. Each database is only active on one server.
Exchange 2016 DAG - 3 servers 2 sites
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
Kieri Solutions partnering with defense contractors to achieve CMMC Level 2 certification
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
warning vsphere health detected new issue memory exhaustion 6.7 vcenter
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
Step by Step: Upgrade vCenter VCSA 6.0 (or 6.5) to 6.7
How to prepare for a DoD CMMC audit and certification
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
How to prepare for a DoD CMMC audit and certification
Fix Expired vCenter Root Password (6.5 & 6.7)
How to rename Windows Server 2016 Domain Controller
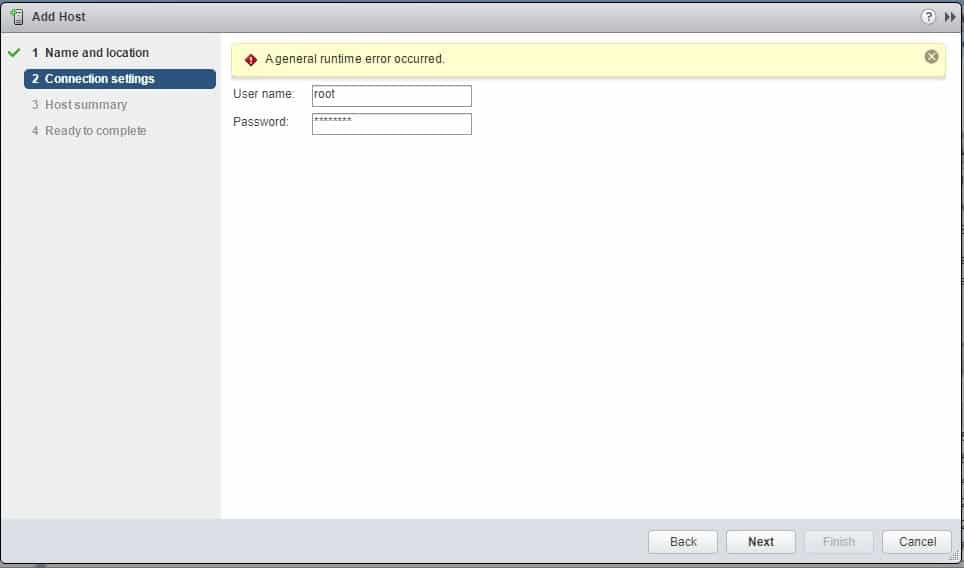
Runtime Error Adding Host in VMware vCenter & ESXi
add host a general runtime error occurred vcenter 6.5 6.7
Runtime Error Adding Host in VMware vCenter & ESXi
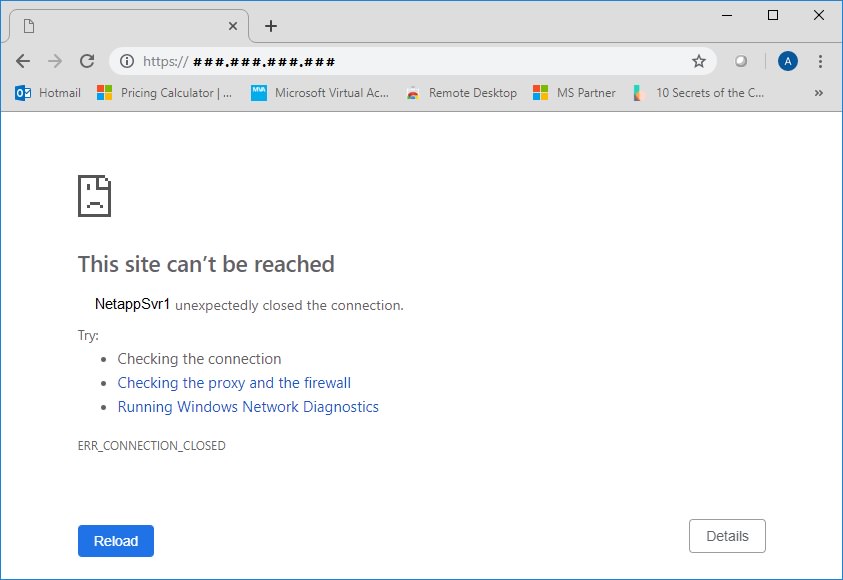
How to fix Netapp expired self-signed certificate by creating a new one
netapp certificate expired install site cant be reached
How to fix Netapp expired self-signed certificate by creating a new one
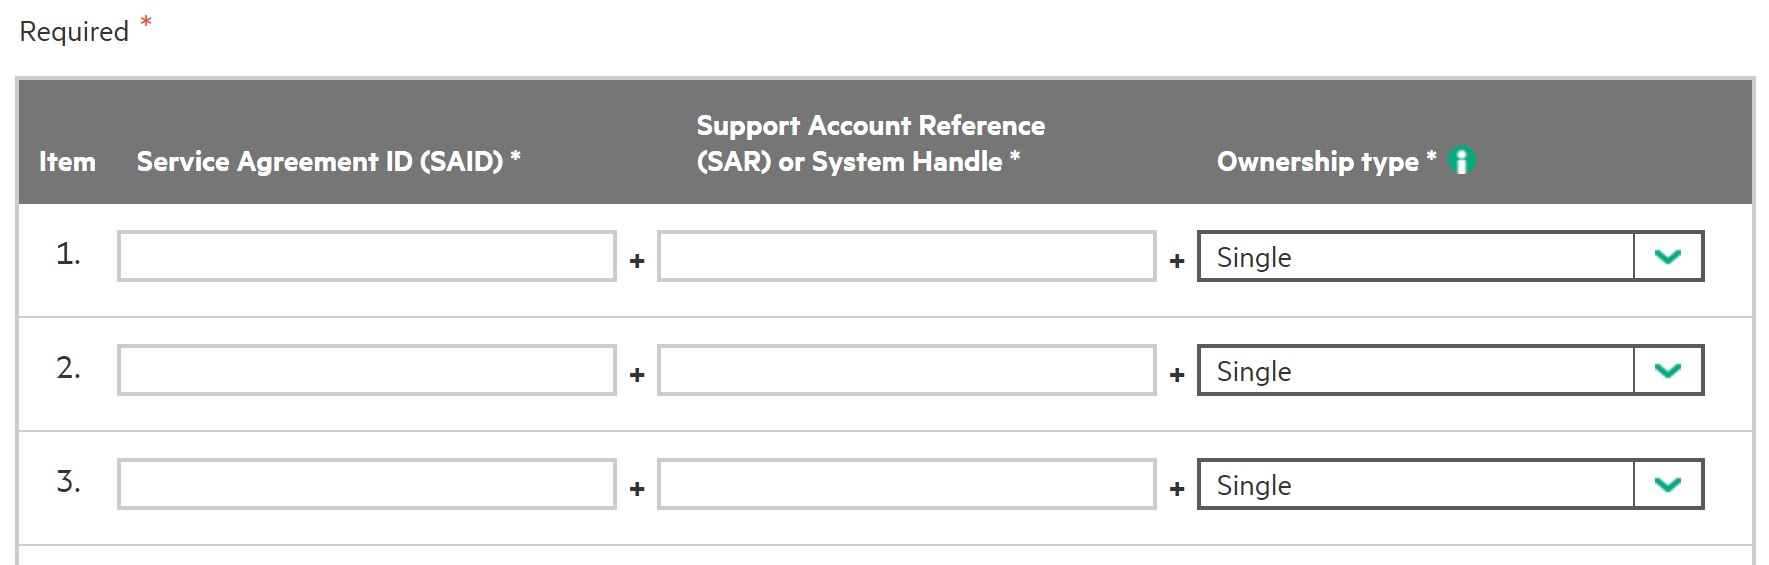
How to register a warranty or service agreement on HPE website
hpe hp register account SAR ID service agreement warranty how accept
How to register a warranty or service agreement on HPE website
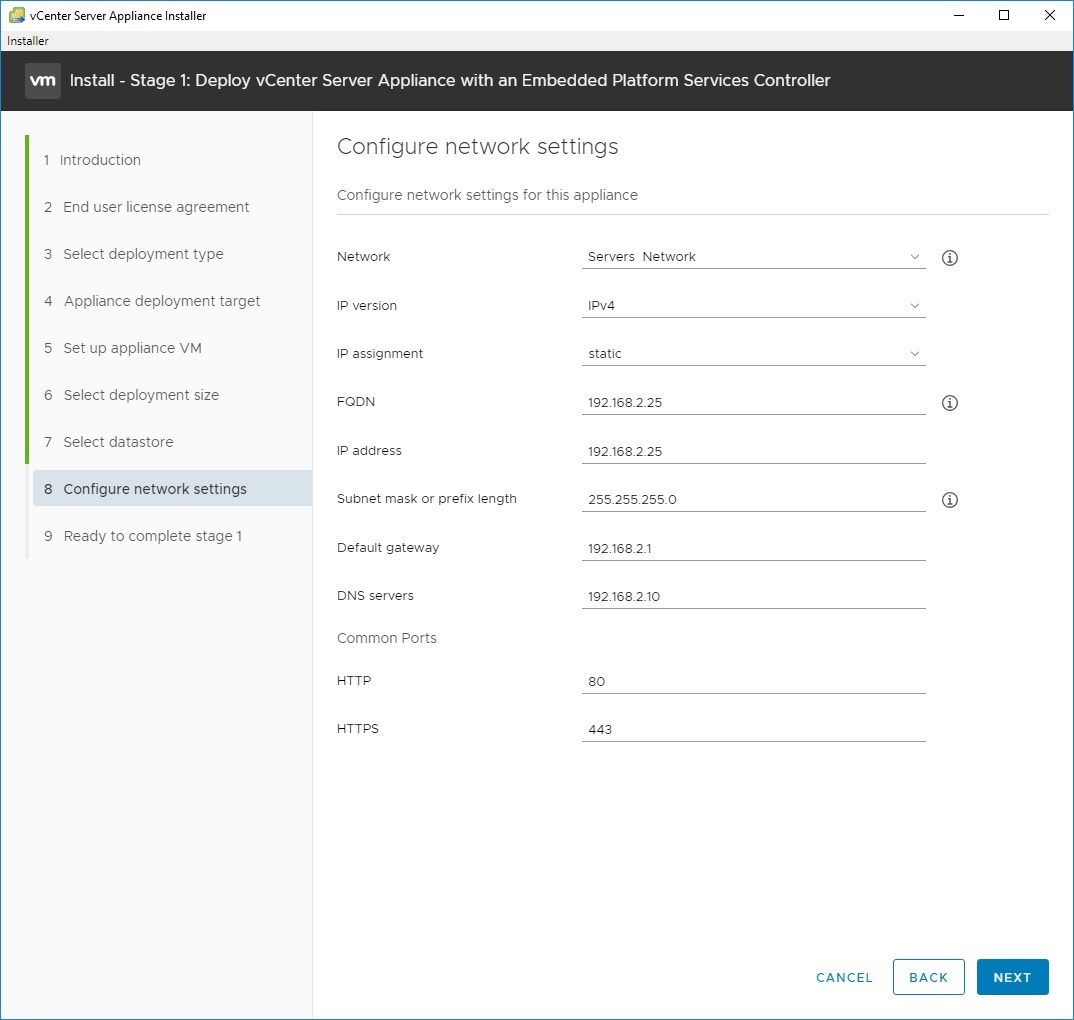
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
vcenter ip address no dns
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
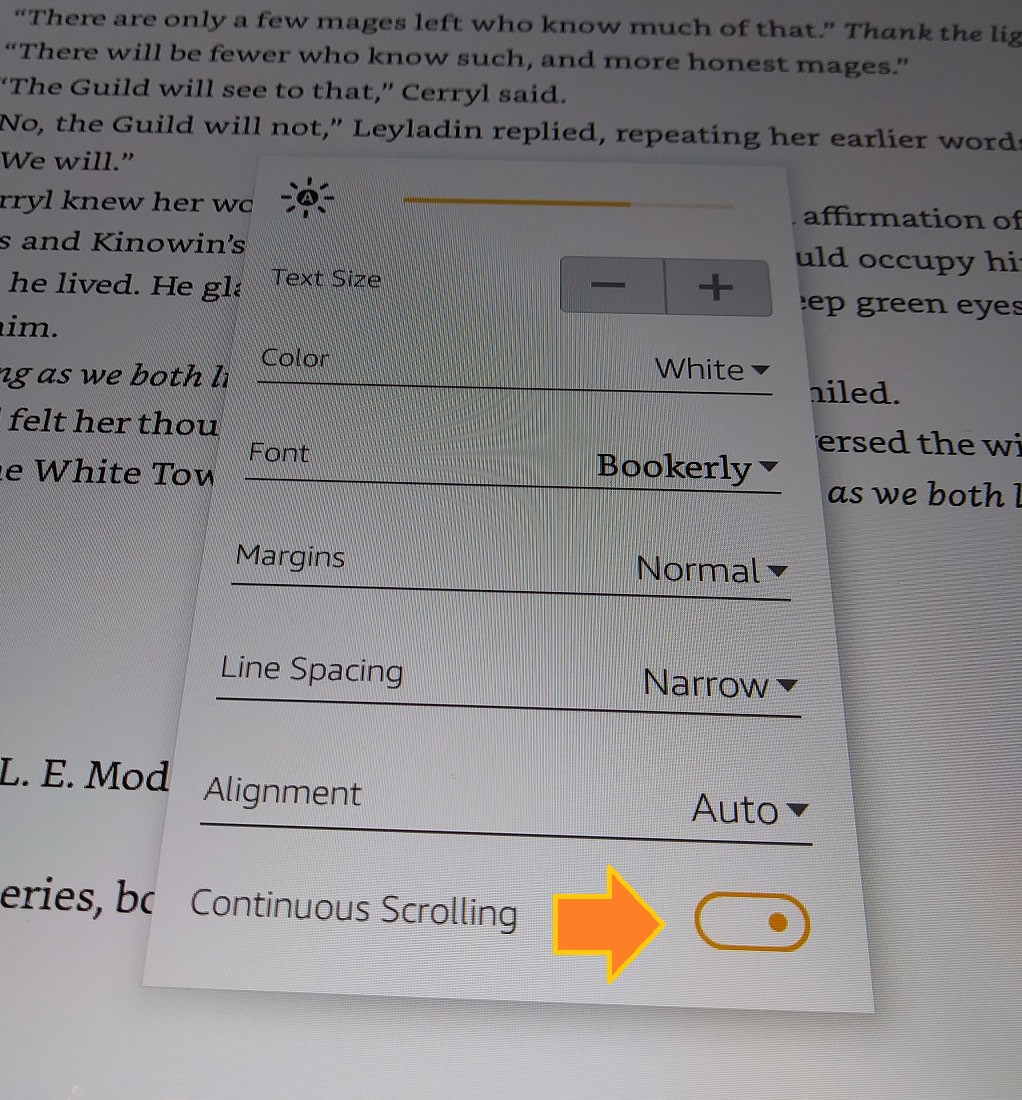
How to disable continuous scrolling on Kindle - turn on page flip
disable continuous scrolling option displays
How to disable continuous scrolling on Kindle - turn on page flip
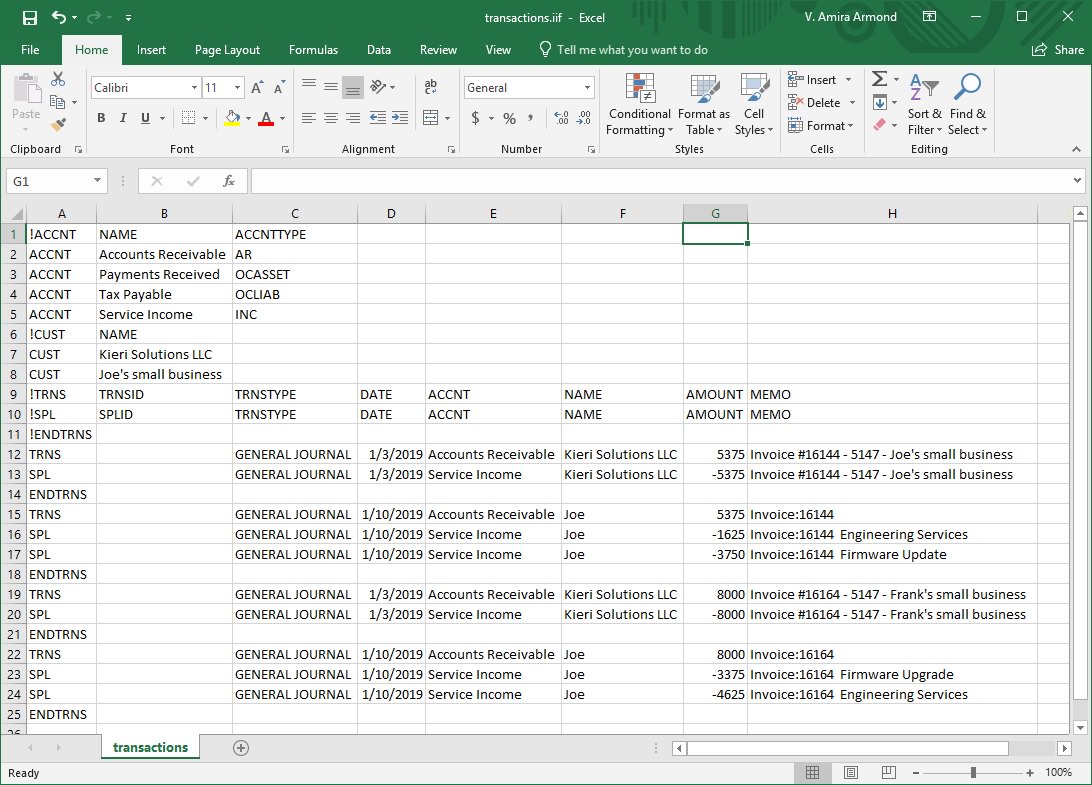
17hats how to export or convert to Excel CSV TAB XLS workbook
17hats export convert iff to csv tab excel
17hats how to export or convert to Excel CSV TAB XLS workbook
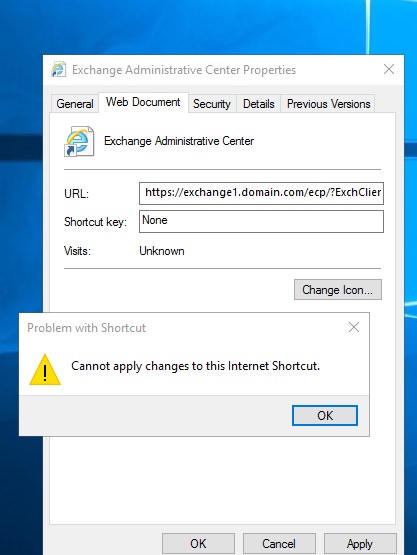
How to fix "Cannot apply changes to this Internet Shortcut" Windows
cannot apply changes to this internet shortcut 2016 2019
How to fix "Cannot apply changes to this Internet Shortcut" Windows
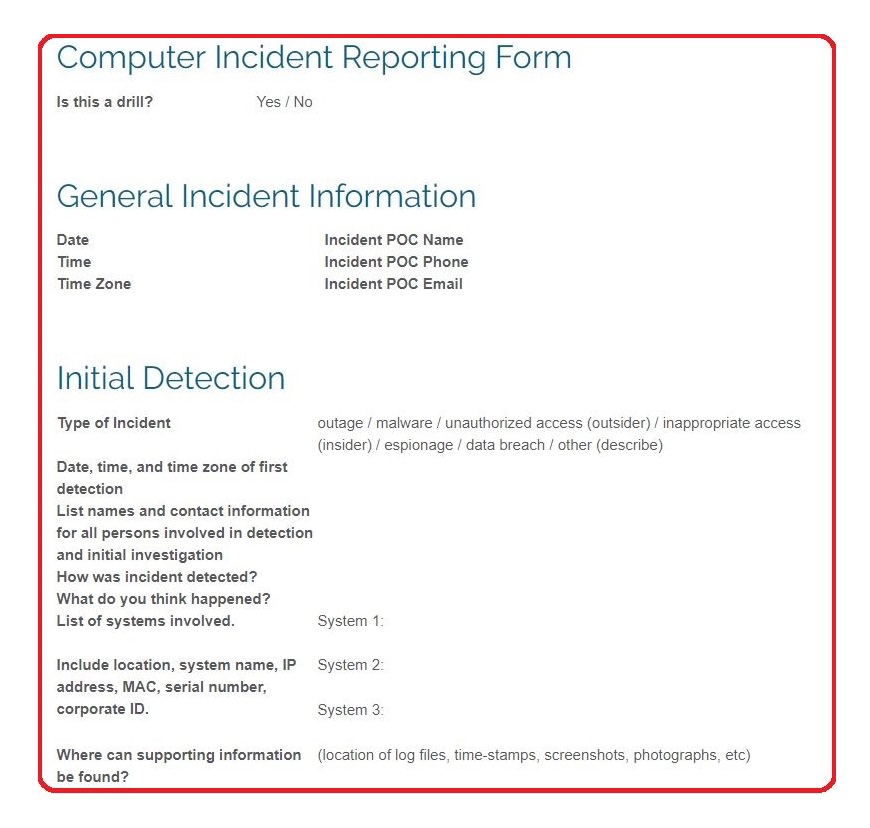
Best Free Computer Incident Response Templates and Scenarios
best free incident response reporting form cybersecurity IT
Best Free Computer Incident Response Templates and Scenarios
Firmware & System Patching Services | DC & Maryland
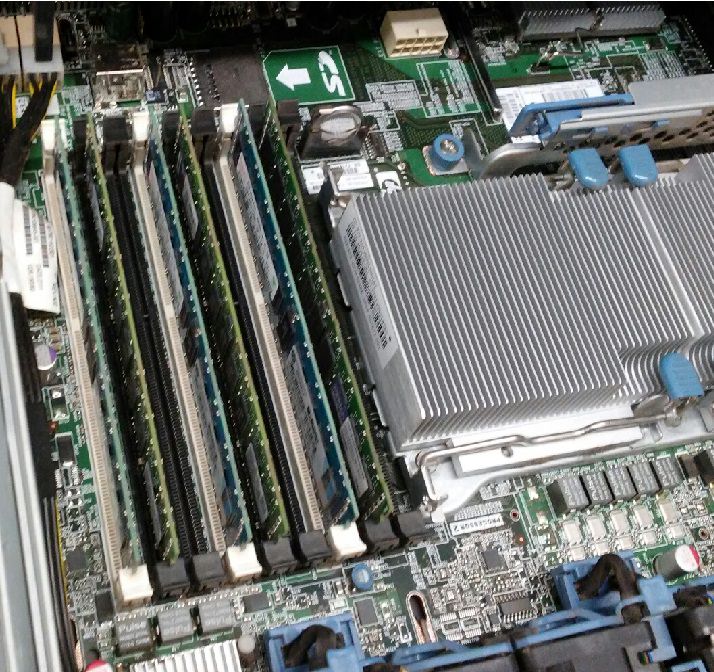
poweredge server raid reconfigure add disks 1 5
Firmware & System Patching Services | DC & Maryland
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
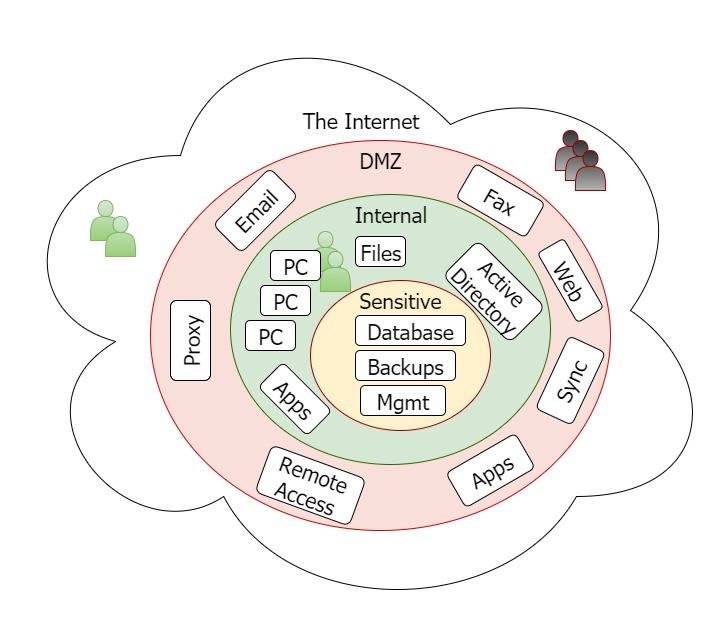
Best practice network segmentation and hardening prevents pivot attacks NIST
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Best practices and how to install esxi vsphere vcenter vmware and troubleshooting problems during the migration
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Disaster Recovery & Business Continuity in DC & Maryland
disaster recovery drp bcp hipaa frederick columbia gaithersburg baltimore rockville
Disaster Recovery & Business Continuity in DC & Maryland
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
installation services netapp disk shelf baltimore columbia rockville
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
SBDC - Intro to GDPR training - Frederick MD
intro gdpr overall sbdc fitci frederick
SBDC - Intro to GDPR training - Frederick MD
GDPR and Human Resources
cybersecurity cyber security hardening compliance firewall design frederick
GDPR and Human Resources
No, your computer isn't slow.
why slow computer pc repair frederick damascus mt airy md
No, your computer isn't slow.
Why you should consider a credit freeze - EquiFax hack
credit freeze equifax hack how to breach innovis
Why you should consider a credit freeze - EquiFax hack
Virtual Servers, Storage, and SAN - Why your servers are slow
cybersecurity compliance design consulting engineering
Virtual Servers, Storage, and SAN - Why your servers are slow
How to un-freeze your laptop like a pro
pc or computer problem repair damascus lisbon mt airy laytonsville
How to un-freeze your laptop like a pro
Upgrade your IT Services for the New Year
managed services it department outsource company frederick columbia germantown gaithersburg
Upgrade your IT Services for the New Year
Dell PowerEdge R730 PERC RAID online reconfiguration
poweredge server raid reconfigure add disks 1 5
Dell PowerEdge R730 PERC RAID online reconfiguration
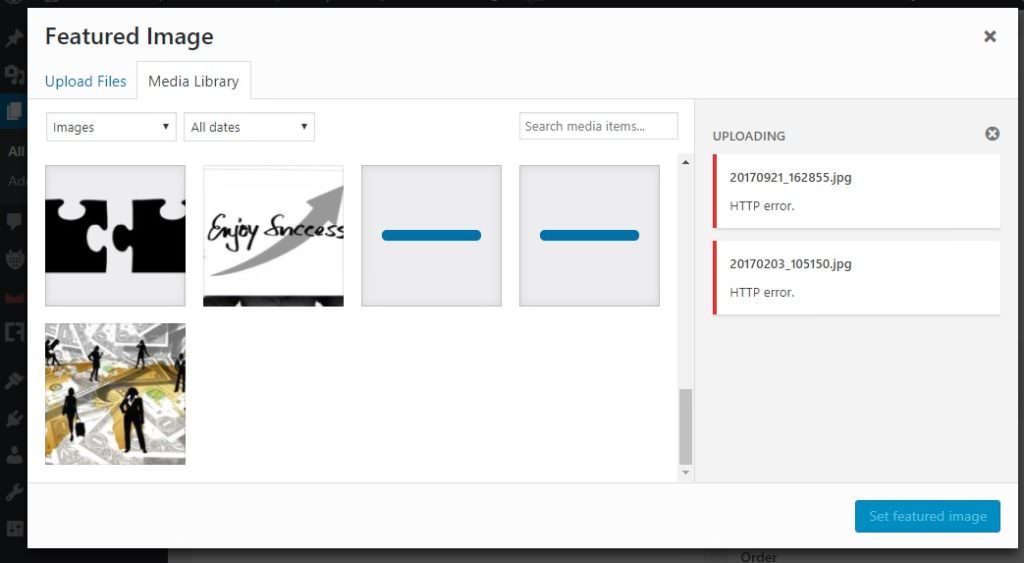
Dreamhost HTTP error Wordpress media upload and library
dreamhost http error picture disappear upload shared wordpress
Dreamhost HTTP error Wordpress media upload and library
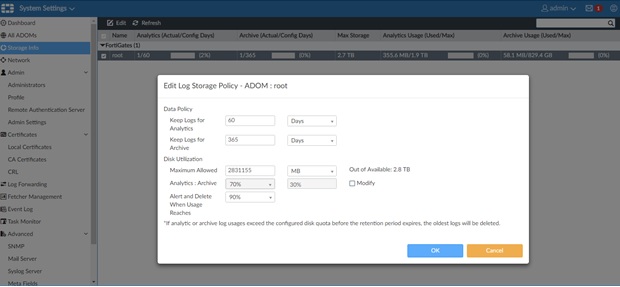
FortiAnalyzer Configuration problems after initial deploy
FortiAnalyzer 5.4 Storage Quota Limits for ADOM root
FortiAnalyzer Configuration problems after initial deploy
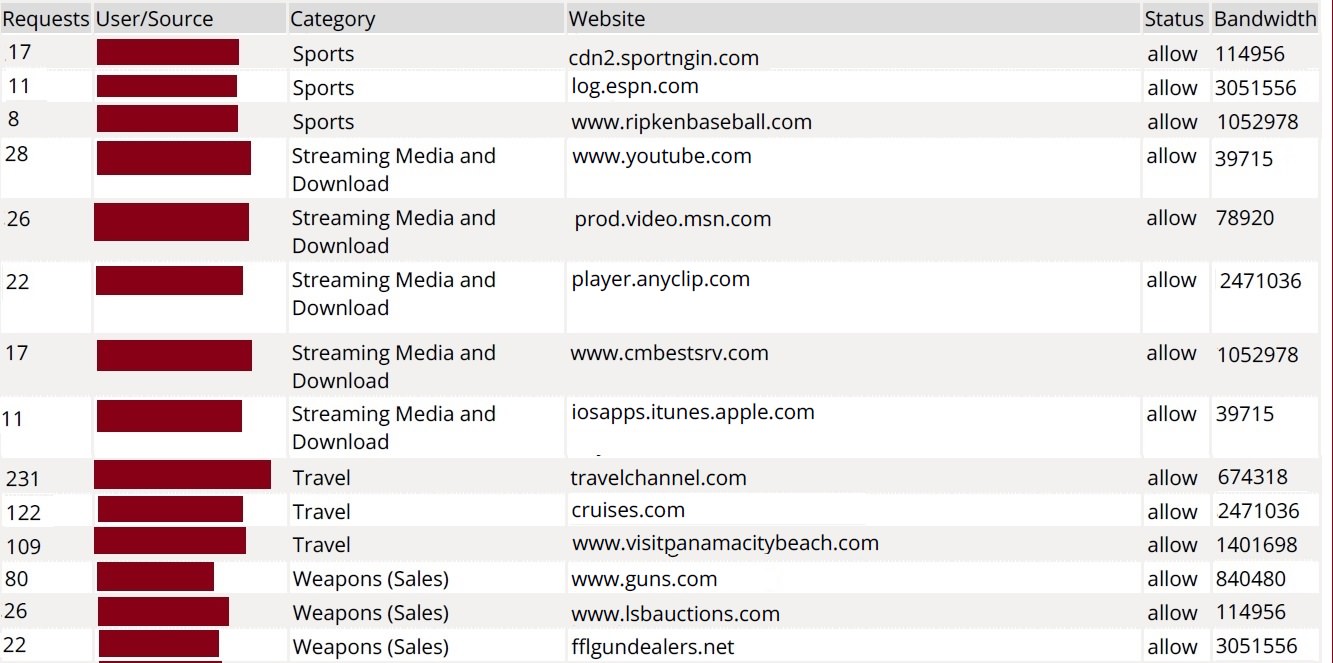
FortiAnalyzer Report: User Web Browsing by Category
fortianalyzer custom report users by category who is browsing web goofing off
FortiAnalyzer Report: User Web Browsing by Category
GDPR Consulting - What you need to know
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
GDPR Consulting - What you need to know
The #1 Computer Security Threat Just Evolved - RCE Worm
cybersecurity cyber security compliance firewall frederick md
The #1 Computer Security Threat Just Evolved - RCE Worm
Fix vSphere & vCenter Datastore Size Reverting
security design cybersecurity consulting services compliance
Fix vSphere & vCenter Datastore Size Reverting
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
conflicting vibs error vsphere upgrade metadata consultant vmware
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
Is your IT person holding the network hostage?
Server Upgrade Cybersecurity Consultant SAN Netapp Frederick
Is your IT person holding the network hostage?
4 Hiring Mistakes When Choosing an IT Company
mistakes when hire IT consultant MSP managed service provider computer support outsourcing
4 Hiring Mistakes When Choosing an IT Company
What you should know about Cloud Computing and Office 365
cloud IT department migration Office 365 Frederick Baltimore Columbia MD
What you should know about Cloud Computing and Office 365
Can You Make Our Nation Safe from Hackers?
The Ultimate Way to Protect Against Computer Theft
Kieri Solutions site icon
The Ultimate Way to Protect Against Computer Theft
Small / medium business security concerns
managed services it department outsource company frederick columbia germantown gaithersburg
Small / medium business security concerns
Approaches to security policy
cybersecurity cyber security hardening compliance firewall design frederick
Approaches to security policy

Article

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan

Article

What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.

Article

NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3

No one wants to start from blank templates.

No one wants to start from
blank templates.

Stop starting from blank templates. Get documentation proven through actual CMMC Level 2 assessment.