Open navigation menu - Kieri Solutions
What Does the Government Actually Require of You Today?

What Does the Government Actually Require of You Today?

A network of yellow lines connecting round nodes against a dark background.

In this article

Is this page for you?

Start here if any of these sound familiar:

  • You just won a defense contract, or you’re about to, and it has a cybersecurity clause you don’t fully understand.
  • You’re pursuing a defense contract and want to know what you’ll be asked to show.
  • You’re moving from commercial work into government contracting for the first time.
  • You won a research or innovation award, and now someone is asking about compliance.
  • You’ve heard “CMMC is on hold” and you’re not sure what that means for you.

You don’t need to know the acronyms yet. By the end of this page, you’ll know what applies to you today and where to start.

The short answer

Some headlines turned the July pause into “CMMC is dead.” It isn’t. And even if it were, most of what you owe never came from CMMC in the first place.

What changed in July 2026?

On July 13, 2026, the Department of War paused Phase 2 implementation of the Cybersecurity Maturity Model Certification program, known as CMMC. On November 10, 2025, Phase 1 was already implemented which slowly introduced the requirement for DIB contractors to be certified by CMMC Third-Party Assessment Organization (C3PAO) before winning contracts involving sensitive information. Phase 2, which merely expanded the scope of contractors required to be assessed at CMMC L2 by a C3PAO was scheduled to begin November 10, 2026 and has now been paused.

The Department also created a Reform Task Force to review the program and recommend changes. As of the date at the top of this page, its recommendations have not been made public.

What didn’t change?

Almost everything you owe today. These obligations come from your contract clauses, and they remain in force. CMMC did not go away, and the requirements are still applicable (Only the phase 2 portion is paused).

If you remember one thing: protect what the government gives you, and tell the truth about how you do it.

  • Protecting basic contract information. If your contract involves Federal Contract Information (non-public information the government gives you, or that you create for it), you must meet 15 basic safeguarding requirements. (FAR 52.204-21)
  • Protecting sensitive information. If you handle Controlled Unclassified Information (sensitive government information that requires protection), you must implement the 110 security requirements in NIST SP 800-171. You must also report cyber incidents to the Department within 72 hours and flow these requirements down to your subcontractors. (DFARS 252.204-7012)
  • Assessing yourself and reporting your score. You post your results in the Supplier Performance Risk System (SPRS), the government’s database of contractor cybersecurity scores. That score is based on your System Security Plan, the document that describes how you protect sensitive information. (DFARS 252.204-7019, -7020, -7021)
  • Signing an affirmation. Level 1 contractors self-assess and affirm every year. Level 2 self-assessments run every three years, with an affirmation every year. Each affirmation is a representation to the federal government by a named senior official at your company. (32 CFR Part 170)

Enforcement didn’t pause either. The Department of Justice has continued to resolve cybersecurity cases under the False Claims Act during the review. Civil Division | Fraud Section Press Releases | United States Department of Justice

What can a contracting officer put in a solicitation right now?

Current direction instructs contracting officers to remove third-party certification requirements from solicitations and contracts, and to allow self-assessment in their place. NIST SP 800-171 remains the baseline for protecting sensitive information and DFARS 252.204-7021 remains the requirement for assessing.

The certification requirement is paused. The security requirement and the self-assessment requirement are not.

What happens when the Task Force report comes out?

A task force report is advice. Your legal obligations change only through a formal action:

  • a class deviation,
  • a change to the defense acquisition rules (DFARS), or
  • an amendment to the CMMC rule itself (32 CFR Part 170).

Same day of report release, we’ll cover what it recommends, what it actually changes, and what it can’t change without formal rulemaking. Our approach won’t change with it: readiness now, certification when it’s required.

Where to start

Cybersecurity is the journey. Compliance is the outcome. Wherever you are on the journey, these steps come in this order.

  1. Know what you owe.
  • Read your contract clauses. Look for FAR 52.204-21 and DFARS 252.204-7012, -7019, -7020 and -7021. They tell you whether you handle basic contract information, sensitive information, or both.
  • Find out where that information lives: which systems, people and locations touch it. That scope decides how much work you actually have.
  1. Check what you’ve said.
  • Find out whether your company has posted an SPRS score, and whether it reflects what’s actually in place.
  • Read your System Security Plan and ask whether it describes your environment or a generic one. A score that overstates reality is a risk, not an asset.
  1. Plan the next step.
  • Write down the gaps and how you’ll close them. That’s what a plan of action is for.
  • Keep the security work and the people doing it. If you pause “the CMMC project,” don’t pause the security underneath it. That work counts no matter what the report says.


Start with a conversation, not a contract. 
Cybersecurity data analysis supporting CMMC Level 2 audit preparation for defense contractors

Evidence Review

Thorough examination of your compliance evidence. We verify documentation completeness.
Don't miss these

What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.
What Does the Government Actually Require of You Today?
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
CMMC Backup Requirements and The Myths Worth Ignoring
Server backup drives in a dark data center supporting CMMC backup requirements for a defense contractor
CMMC Backup Requirements and The Myths Worth Ignoring
How to Prepare for a DIBCAC High Assessment
Analyst reviewing evidence on dark dual monitors while preparing for a DIBCAC High assessment
How to Prepare for a DIBCAC High Assessment
Out of Scope Assets - What the Final Rule Actually Changed
Abstract data cityscape tied to out of scope assets in a CMMC assessment by Kieri Solutions
Out of Scope Assets - What the Final Rule Actually Changed
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
Dark cybersecurity image with glowing data illustrating CMMC final rule compliance for defense contractors
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
Analyst reviewing code while working toward CMMC and NIST 800-171 compliance
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
CUI Assets - What Assessors Actually Evaluate
Abstract network of nodes tied to CUI assets and CMMC scope assessed by Kieri Solutions
CUI Assets - What Assessors Actually Evaluate
Do I Even Have CUI? Understanding What You Need to Protect
Abstract data network tied to finding CUI on a defense contractor network with Kieri
Do I Even Have CUI? Understanding What You Need to Protect
Why the DoD Wants Security Protection Data Protected Like CUI
Abstract data network tied to security protection data and CMMC scope assessed by Kieri
Why the DoD Wants Security Protection Data Protected Like CUI
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Cybersecurity professional conducting CMMC gap analysis for a defense contracting organization
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Network architecture visualization for a CMMC Level 2 reference architecture built on Microsoft 365 GCC High
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Why Most CMMC Documentation Fails and How to Fix It
CMMC compliance documentation policies and procedures
Why Most CMMC Documentation Fails and How to Fix It
What Passed a DOD Assessment for System Baselining and Inventories
CMMC system inventory and baseline configuration monitoring dashboard
What Passed a DOD Assessment for System Baselining and Inventories
How to Implement Mobile Code Requirements for CMMC Level 2
CMMC mobile code security controls and technical implementation
How to Implement Mobile Code Requirements for CMMC Level 2
What Does "Monitor" Actually Mean in CMMC Requirements?
CMMC monitoring requirements - access control and password security verification
What Does "Monitor" Actually Mean in CMMC Requirements?
The Version 20 Problem and How to Avoid It
CMMC compliance documentation sequence - cybersecurity program management
The Version 20 Problem and How to Avoid It
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
CMMC Level 2 compliant environment security controls and access management
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
Inside the KCD - What Makes This Documentation Different
CMMC compliance documentation templates digital security
Inside the KCD - What Makes This Documentation Different
How the Kieri Compliance Documentation and Reference Architecture Work Together
Kieri Compliance Documentation and Reference Architecture working together for CMMC Level 2 compliance
How the Kieri Compliance Documentation and Reference Architecture Work Together
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC compliance documentation and reference architecture security controls - fingerprint scanning and access management
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC Assessments by Kieri Solutions
Global cybersecurity compliance support for defense contractors under DFARS
CMMC Assessments by Kieri Solutions
CMMC Education: User vs Network Session Termination
Secure IT infrastructure design supporting CMMC Level 2 compliance for defense contractors
CMMC Education: User vs Network Session Termination
CMMC Proposed Rule has been released! 
Cybersecurity threat - CMMC compliance
CMMC Proposed Rule has been released! 
Interested in the Kieri Compliance Documentation?
Secure data transmission within CMMC compliant network architecture
Interested in the Kieri Compliance Documentation?
How to fix Outlook missing Friday January 13 2023
Interconnected defense contractor networks requiring CMMC Level 2 cybersecurity certification
How to fix Outlook missing Friday January 13 2023
C3PAO Meeting - July 26, 2021 12-1 pm EDT
NIST SP 800-171 DoD Self Assessment Services
DFARS 252.204-7012 and NIST SP 800-171 requirements
NIST SP 800-171 DoD Self Assessment Services
vSphere Health detected new issues in your environment 6.7
vcenter 6.7 alarm displays vsphere health detected new issue
vSphere Health detected new issues in your environment 6.7
vCenter Health Warning: External Platform Services Controller
Synology storage latency and disconnects on VMware
Windows Stuck in Recovery Mode Datto driver signing
Office 365 MFA App Password Missing Fix
Microsoft Teams Conference Calls & Dial-In Numbers
C: Drive Full Exchange
Exchange server very slow, services and network blank
Exchange 2016 DAG - 3 servers 2 sites
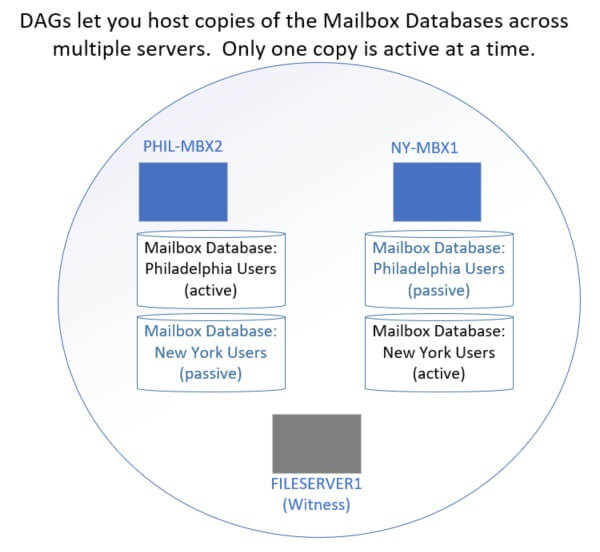
Diagram showing mailbox servers with active and passive databases. Each database is only active on one server.
Exchange 2016 DAG - 3 servers 2 sites
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
Kieri Solutions partnering with defense contractors to achieve CMMC Level 2 certification
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
warning vsphere health detected new issue memory exhaustion 6.7 vcenter
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
Step by Step: Upgrade vCenter VCSA 6.0 (or 6.5) to 6.7
How to prepare for a DoD CMMC audit and certification
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
How to prepare for a DoD CMMC audit and certification
Fix Expired vCenter Root Password (6.5 & 6.7)
How to rename Windows Server 2016 Domain Controller
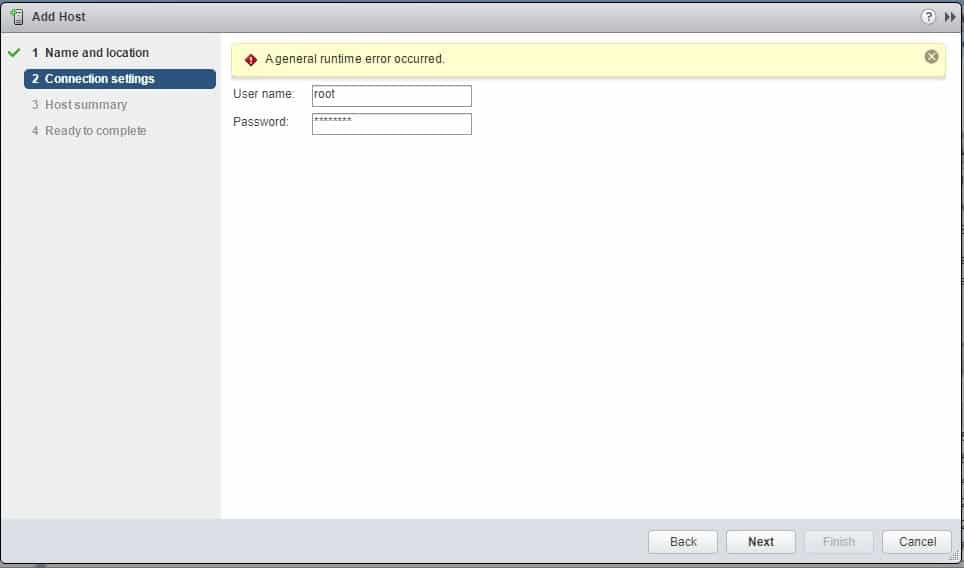
Runtime Error Adding Host in VMware vCenter & ESXi
add host a general runtime error occurred vcenter 6.5 6.7
Runtime Error Adding Host in VMware vCenter & ESXi
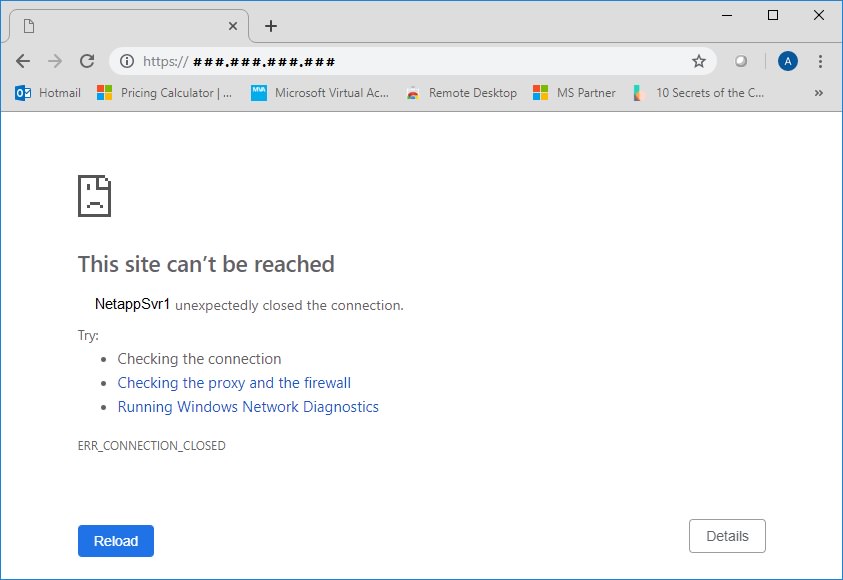
How to fix Netapp expired self-signed certificate by creating a new one
netapp certificate expired install site cant be reached
How to fix Netapp expired self-signed certificate by creating a new one
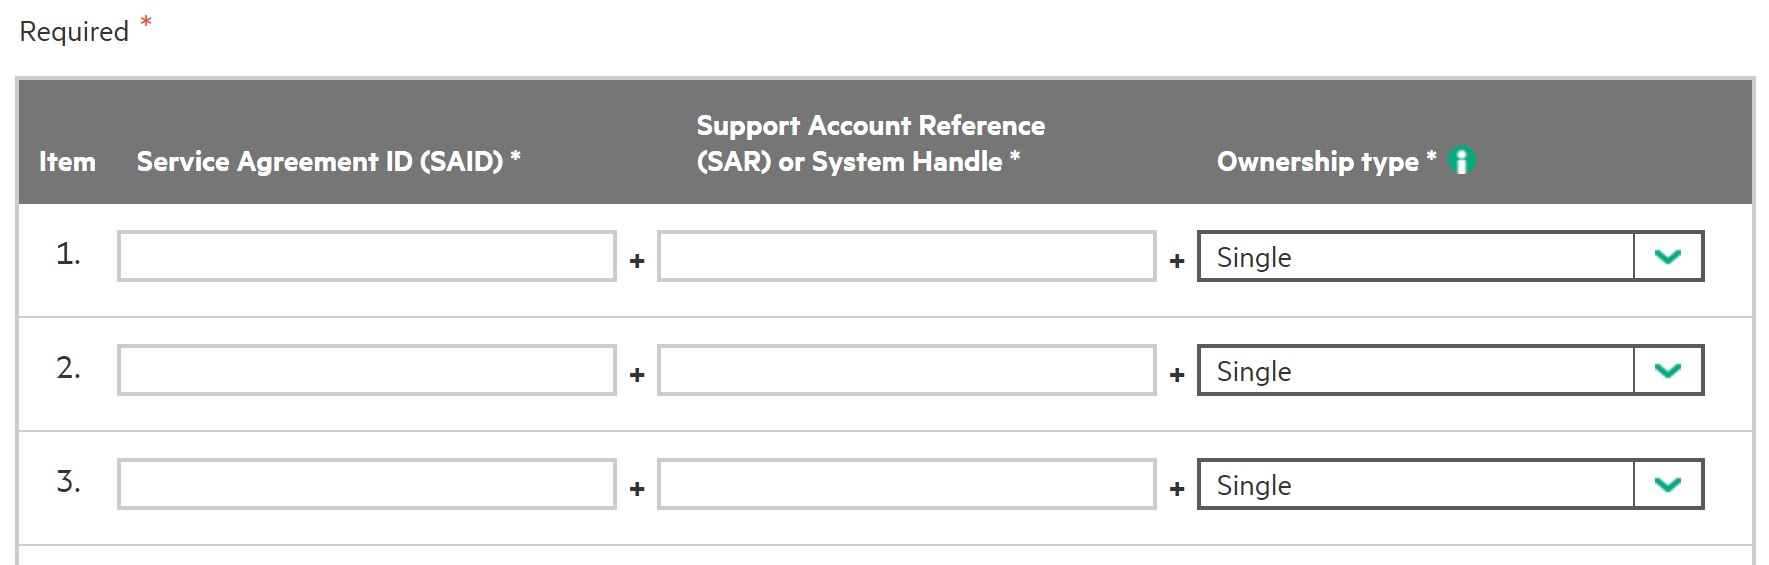
How to register a warranty or service agreement on HPE website
hpe hp register account SAR ID service agreement warranty how accept
How to register a warranty or service agreement on HPE website
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
vcenter ip address no dns
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
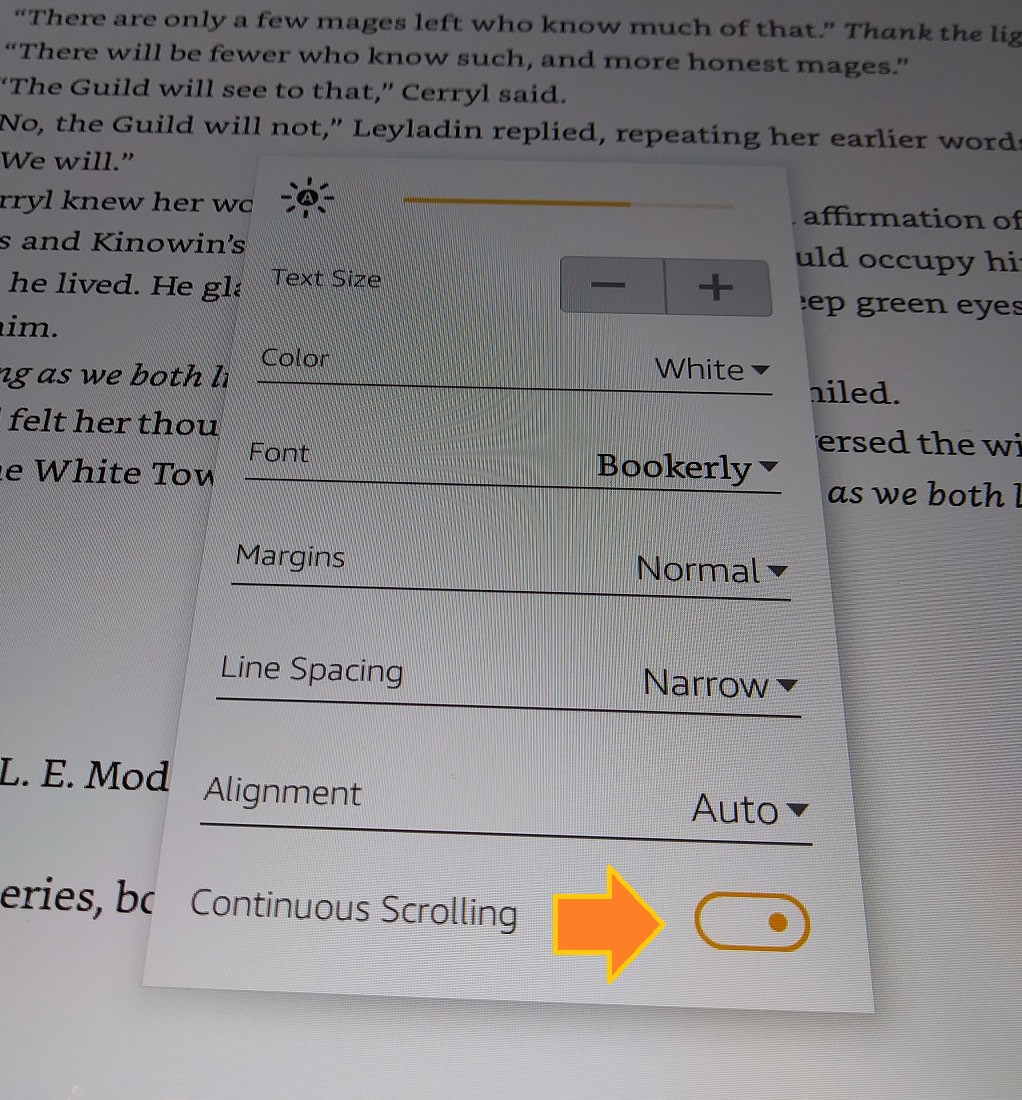
How to disable continuous scrolling on Kindle - turn on page flip
disable continuous scrolling option displays
How to disable continuous scrolling on Kindle - turn on page flip
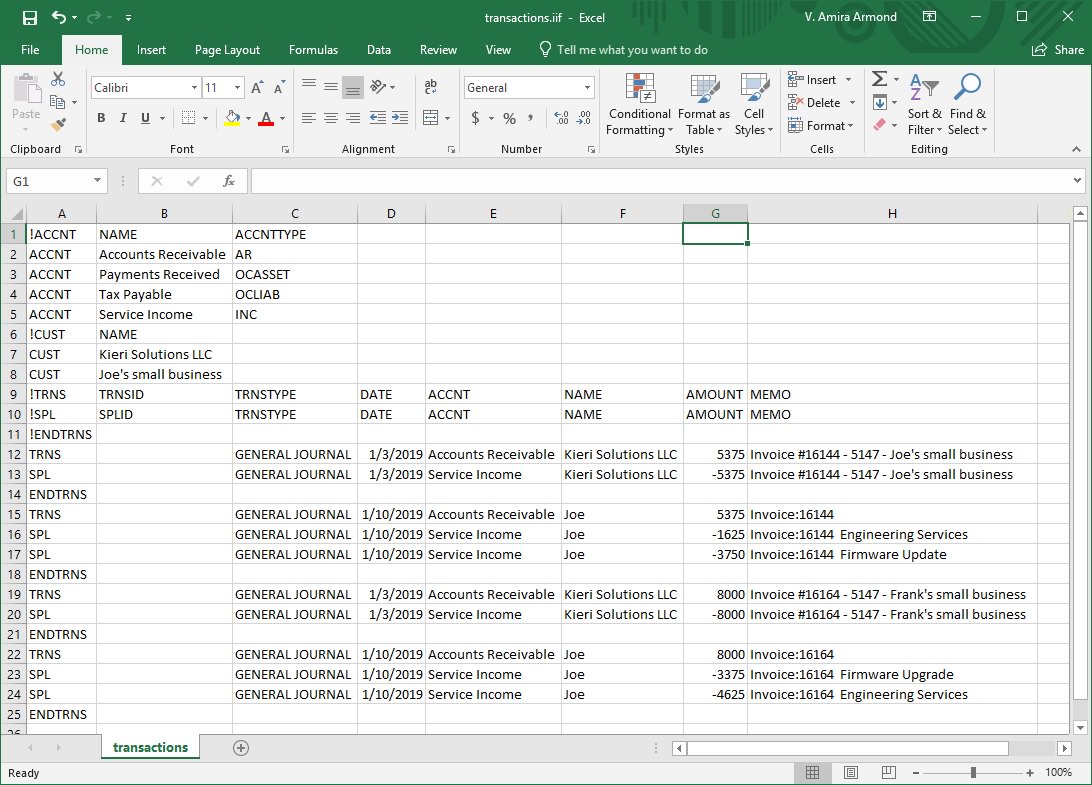
17hats how to export or convert to Excel CSV TAB XLS workbook
17hats export convert iff to csv tab excel
17hats how to export or convert to Excel CSV TAB XLS workbook
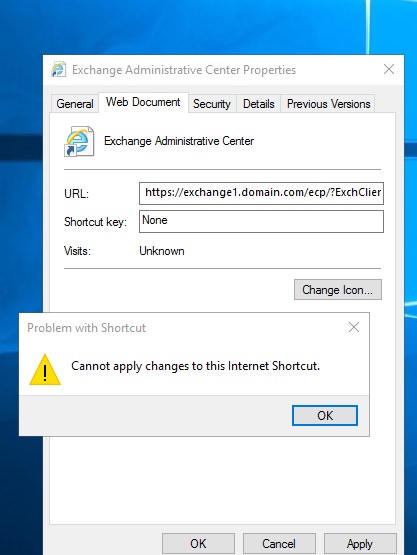
How to fix "Cannot apply changes to this Internet Shortcut" Windows
cannot apply changes to this internet shortcut 2016 2019
How to fix "Cannot apply changes to this Internet Shortcut" Windows
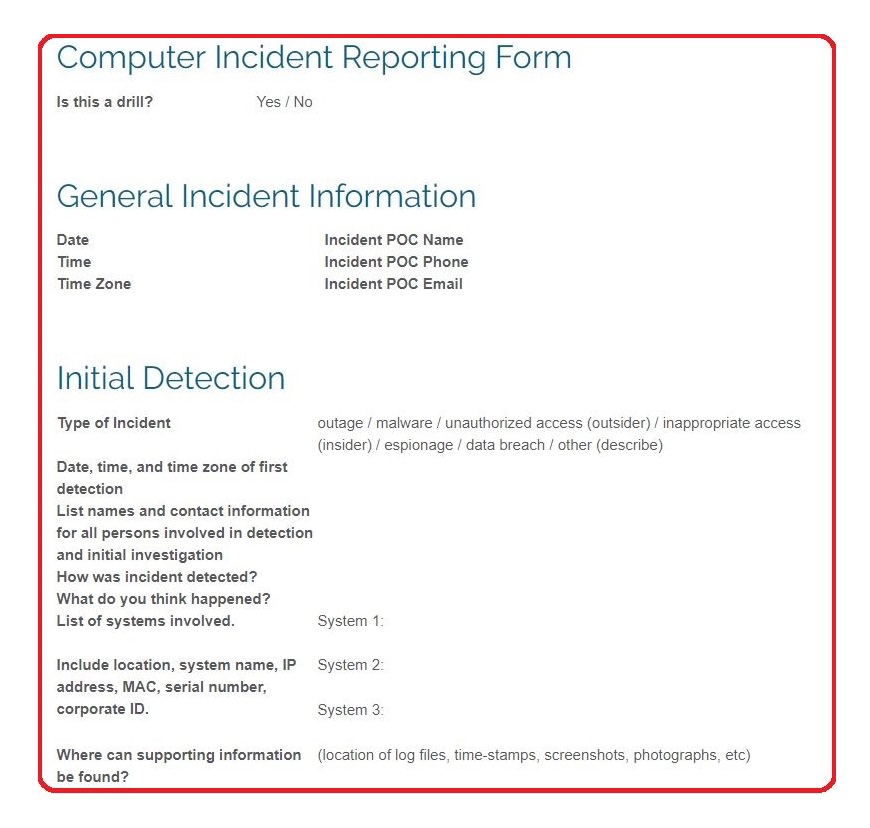
Best Free Computer Incident Response Templates and Scenarios
best free incident response reporting form cybersecurity IT
Best Free Computer Incident Response Templates and Scenarios
Firmware & System Patching Services | DC & Maryland
poweredge server raid reconfigure add disks 1 5
Firmware & System Patching Services | DC & Maryland
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
Best practice network segmentation and hardening prevents pivot attacks NIST
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Best practices and how to install esxi vsphere vcenter vmware and troubleshooting problems during the migration
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Disaster Recovery & Business Continuity in DC & Maryland
disaster recovery drp bcp hipaa frederick columbia gaithersburg baltimore rockville
Disaster Recovery & Business Continuity in DC & Maryland
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
installation services netapp disk shelf baltimore columbia rockville
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
SBDC - Intro to GDPR training - Frederick MD
intro gdpr overall sbdc fitci frederick
SBDC - Intro to GDPR training - Frederick MD
GDPR and Human Resources
cybersecurity cyber security hardening compliance firewall design frederick
GDPR and Human Resources
No, your computer isn't slow.
why slow computer pc repair frederick damascus mt airy md
No, your computer isn't slow.
Why you should consider a credit freeze - EquiFax hack
credit freeze equifax hack how to breach innovis
Why you should consider a credit freeze - EquiFax hack
Virtual Servers, Storage, and SAN - Why your servers are slow
cybersecurity compliance design consulting engineering
Virtual Servers, Storage, and SAN - Why your servers are slow
How to un-freeze your laptop like a pro
pc or computer problem repair damascus lisbon mt airy laytonsville
How to un-freeze your laptop like a pro
Upgrade your IT Services for the New Year
managed services it department outsource company frederick columbia germantown gaithersburg
Upgrade your IT Services for the New Year
Dell PowerEdge R730 PERC RAID online reconfiguration
poweredge server raid reconfigure add disks 1 5
Dell PowerEdge R730 PERC RAID online reconfiguration
Dreamhost HTTP error Wordpress media upload and library
dreamhost http error picture disappear upload shared wordpress
Dreamhost HTTP error Wordpress media upload and library
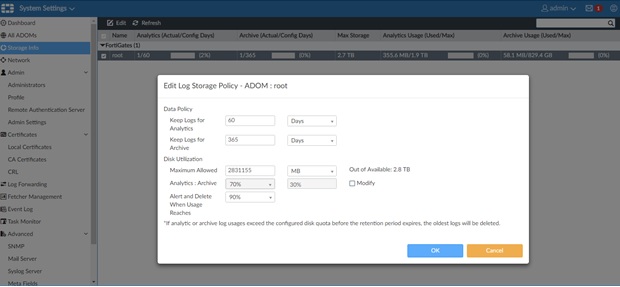
FortiAnalyzer Configuration problems after initial deploy
FortiAnalyzer 5.4 Storage Quota Limits for ADOM root
FortiAnalyzer Configuration problems after initial deploy
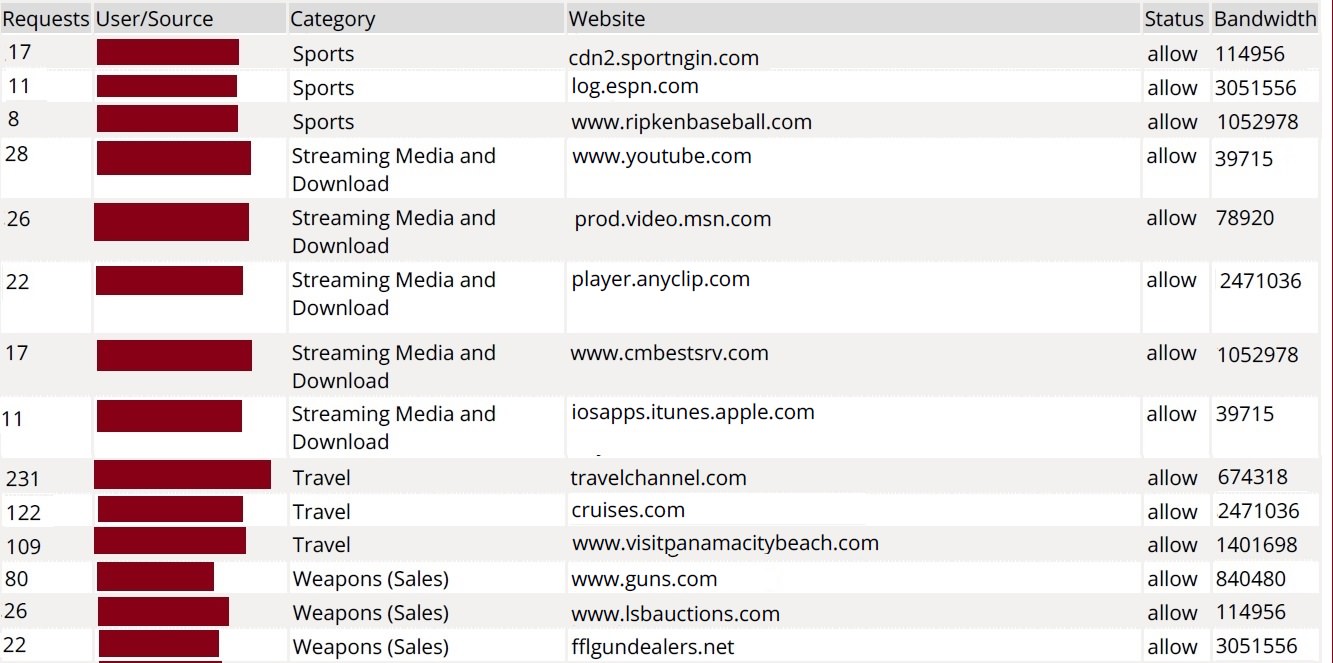
FortiAnalyzer Report: User Web Browsing by Category
fortianalyzer custom report users by category who is browsing web goofing off
FortiAnalyzer Report: User Web Browsing by Category
GDPR Consulting - What you need to know
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
GDPR Consulting - What you need to know
The #1 Computer Security Threat Just Evolved - RCE Worm
cybersecurity cyber security compliance firewall frederick md
The #1 Computer Security Threat Just Evolved - RCE Worm
Fix vSphere & vCenter Datastore Size Reverting
security design cybersecurity consulting services compliance
Fix vSphere & vCenter Datastore Size Reverting
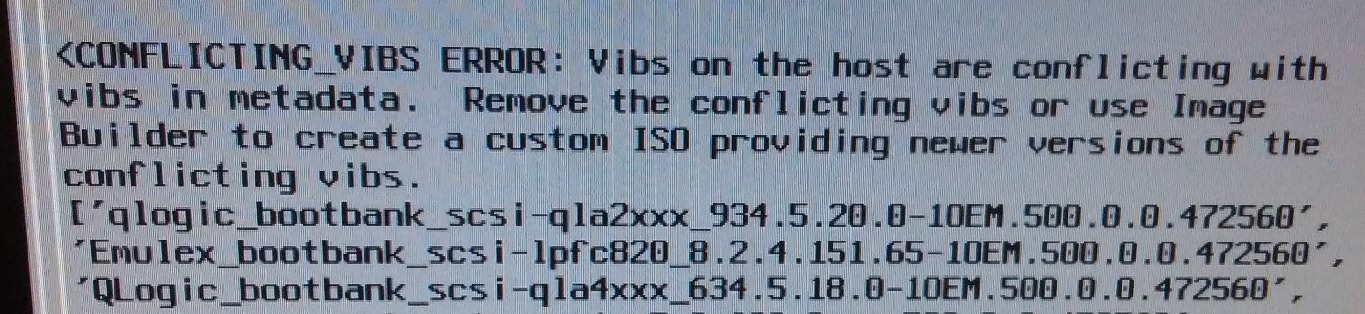
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
conflicting vibs error vsphere upgrade metadata consultant vmware
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
Is your IT person holding the network hostage?
Server Upgrade Cybersecurity Consultant SAN Netapp Frederick
Is your IT person holding the network hostage?
4 Hiring Mistakes When Choosing an IT Company
mistakes when hire IT consultant MSP managed service provider computer support outsourcing
4 Hiring Mistakes When Choosing an IT Company
What you should know about Cloud Computing and Office 365
cloud IT department migration Office 365 Frederick Baltimore Columbia MD
What you should know about Cloud Computing and Office 365
Can You Make Our Nation Safe from Hackers?
The Ultimate Way to Protect Against Computer Theft
Kieri Solutions site icon
The Ultimate Way to Protect Against Computer Theft
Small / medium business security concerns
managed services it department outsource company frederick columbia germantown gaithersburg
Small / medium business security concerns
Approaches to security policy
cybersecurity cyber security hardening compliance firewall design frederick
Approaches to security policy

Article

What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.

Article

NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3

Article

CMMC Backup Requirements and The Myths Worth Ignoring
Server backup drives in a dark data center supporting CMMC backup requirements for a defense contractor

No one wants to start from blank templates.

No one wants to start from
blank templates.

Stop starting from blank templates. Get documentation proven through actual CMMC Level 2 assessment.