Open navigation menu - Kieri Solutions
CMMC Phase 2 Suspended and What Defense Contractors Need to Know

CMMC Phase 2 Suspended and What Defense Contractors Need to Know

Analyst reviewing code while working toward CMMC and NIST 800-171 compliance

In this article

On July 13, 2026 the Department of War suspended CMMC Phase 2, the stage of the rollout that would have required a third-party assessment as a condition of contract award beginning November 10, 2026. Phase 1 self-assessment, NIST 800-171, and the underlying DFARS obligations all remain in force. A reform task force is reviewing the program and will report within 60 days. The legal duty to protect defense information did not change.

The announcement moved quickly through the defense industrial base, and much of the early commentary framed it as the end of CMMC. It is not. The suspension affects one phase of the rollout, and the requirement it exists to enforce has been in federal contracts for years.

The following is a precise account of what the memo changes, what it leaves untouched, and how contractors should respond.

What did the CMMC Phase 2 suspension actually change?

Phase 2 was the planned expansion of DFARS clause 252.204-7021 into a broader set of contracts. That clause directs a contractor to demonstrate CMMC compliance, which is an assessment of the security requirements already imposed elsewhere. Phase 2 would have moved many contractors from a self-assessment reported through SPRS to a third party assessment performed by a Certified Third Party Assessment Organization, or C3PAO, as a condition of award.

That expansion is what has been suspended. The Department also paused the pending and future CMMC milestones across its solicitations, including the Phase 3 introduction of government led Level 3 assessments under NIST 800-172.

What was not suspended is the substance. DFARS clause 252.204-7020 was not repealed, and the requirement to implement security controls remains exactly where it was.

Which compliance requirements remain in force?

Most of them. This is the point most likely to be misread, so it warrants a clear statement.

  • Phase 1 self-assessment remains required. The release states these requirements remain firmly in place.
  • NIST SP 800-171 Rev 2 remains enforced, through self-assessment and through government-led assessments.
  • DFARS clause 252.204-7012, which directs contractors to implement NIST 800-171, has been in defense contracts since 2017 and is untouched.
  • DFARS clause 252.204-7019 still requires a score in SPRS to be eligible to bid, and the affirming official who certifies that score remains personally accountable for its accuracy.
  • 32 CFR Part 170, the rule that established the program, remains law.

Stated plainly, the suspension changed who verifies the work, not whether the work is required.

Why the assessment was never the expensive part

A common reaction to the suspension is relief about cost. That relief is misplaced, and understanding why is central to making a sound decision.

The expensive part of compliance is implementing the security requirements, and that obligation has existed for roughly eight years. The third party assessment is the smallest cost in the process. What the suspension removed is a verification step, not the underlying program of work that a contractor must complete to protect controlled unclassified information.

The heaviest lift is rarely the technology. It is internal governance, defining how the organization handles data, and getting security, IT, contracts, and operations to work from the same requirements. None of that was affected by the memo, and it does not become easier by waiting. Kieri’s CMMC gap analysis and compliance documentation exist to carry most of that burden for you.

Why enforcement risk has increased, not decreased

Removing the third party assessment requirement returns many contractors to self-attestation, and self-attestation concentrates risk on the company and on the individual who signs it.

The record shows that a significant share of organizations were not self-assessing accurately. For years, a contractor could post a low or even negative SPRS score, on a scale that runs from 110 down to negative 203, and still win awards. Many contractors, however, posted very high scores, for fear that a low score would preclude them from winning the contract. A third party assessment exists precisely because self reported scores proved unreliable, and because an independent assessor absorbs the risk of standing behind the result.

The Department of Justice has grown materially more aggressive here. It has pursued contractors under the False Claims Act for posting inflated scores, and it has begun pursuing the affirming officials who certified them. A suspended assessment phase does not reduce that exposure. It increases it, because the layer of independent validation between a contractor and the government is now optional rather than required.

Why did the Department of War suspend Phase 2?

The stated reasons concern cost and capacity rather than any judgment that the security requirements are wrong. The Department cited compliance costs pricing small businesses out of defense work, projected future costs in the billions for small and mid sized firms, and a shortage of assessment capacity. A March 2026 GAO report had already warned that the standards could prove too costly for some small businesses.

One figure in the announcement deserves correction. The Department suggested roughly 100 assessors were available against more than 100,000 companies. That understates the ecosystem. There are just over 100 authorized C3PAOs and more than a thousand certified assessors. Capacity is a genuine constraint, but it is not as severe as the stated figure implies, and it is one reason acting during the current lull is an advantage rather than a risk.

Does the suspension mean CMMC is being cancelled?

No party can guarantee the outcome of the review. The program’s history, however, is instructive and should inform any decision made in response to a headline.

CMMC has been paused or frozen five times since 2019, and it has never been cancelled. The closest parallel to the present situation is 2021, when the same concerns, small business cost and burden, produced a full review and a pause. Eleven months later the program returned as CMMC 2.0, reduced from five levels to three and permitting self-assessment at the lower tiers. It emerged narrower and later, not eliminated.

A four year interval also illustrates the pattern. From late 2021 the enforcement clause sat suspended, and much of the market treated the pause as permanent. Enforcement then began on November 10, 2025, the exact date the Department had named. Nearly every deadline in the program’s history has slipped, yet not one has been withdrawn.

One caution belongs here. The Request for Information issued with this pause asks which controls deliver the most measurable risk reduction and which impose the greatest burden for the least benefit. The control set itself may therefore be refined, not only the assessment process. What is not in question is the foundation. Every version of this program has been built on NIST 800-171, and that foundation is not going away.

How long is the CMMC pause expected to last?

Longer than the headline number suggests. The CMMC Reform Task Force convened on July 16 and has 60 days to produce recommendations. A public comment window is open until August 14. The 60-day period applies to the recommendations, not to the pause, and the suspension of further phases is open ended.

On a realistic timeline, the task force reports in late September or early October. Any change that follows must proceed through its own rulemaking, a process that has historically taken this program one to three years. Meaningful clarity is most likely to arrive in late 2026 or the first quarter of 2027, not within 60 days.

What subcontractors should expect from prime contractors

The government requirement is not the only requirement that matters. A prime contractor carries its own contractual risk when a subcontractor is not compliant, and 32 CFR Part 170 and the DFARS flow down obligations remain unchanged.

A prime may continue to require a C3PAO assessment of its subcontractors, and it may flow the requirement down exactly as written or add to it. Subcontractors should confirm expectations directly with their primes and their contracting officers. A contract that will not be awarded for another six months is unaffected by a 60 day extension, and a contractor who is not ready when the requirement returns will not win the award.

Kieri’s recommendation for contractors on the path to compliance

For contractors already progressing toward compliance, Kieri’s recommendation is to continue. The reasoning rests on three points.

  • Assessment capacity is available now. With many contractors pausing, C3PAO schedules have room. That capacity does not expand during a suspension, and demand will return in a concentrated wave once the review concludes.
  • Readiness does not remain current. Evidence ages, environments change, and staff turn over. A contractor who defers by six months will repeat work already completed and paid for.
  • Finished contractors hold a competitive position. When clarity arrives, an organization that has completed its assessment can respond to a prime’s requirements immediately, while others return to the queue.

A completed assessment also retains its value today. C3PAOs continue to operate under 32 CFR Part 170, the Cyber AB and the eMASS program office remain active, and an assessment still yields a certificate that primes recognize. At Kieri, no client on the assessment schedule has cancelled in response to the suspension.

Kieri helps defense contractors reach and maintain compliance, from a gap analysis and a reference architecture through a full CMMC assessment. Our case studies show how contractors have reached Level 2 with our support. If you are uncertain what the suspension means for your specific contract, book a consultation and we will review it with you directly.

Frequently asked questions

Is CMMC cancelled?

No. Phase 2 of the rollout, the third party assessment requirement, is suspended while the whole program is reviewed. Phase 1 of the rollout, Level 1 and 2 self-assessments, remains in effect. The program has been paused five times since 2019 and never cancelled.

Do I still need to meet NIST 800-171?

Yes. NIST 800-171 Rev 2 remains enforced through self-assessment and government led assessment, and DFARS 252.204-7012 still requires contractors to protect covered defense information.

When was Phase 2 scheduled to begin?

November 10, 2026. The November 10, 2025 date that has already passed was Phase 1, which took effect on schedule.

How long will the suspension last?

The task force has 60 days to issue recommendations, but the pause itself is open ended. Given the rulemaking required for any change, meaningful clarity is most likely to arrive in late 2026 or early 2027.

Should I cancel my assessment?

For most contractors, no. Assessments continue under 32 CFR Part 170, the certificate still uploads to eMASS, and capacity tightens once the pause ends. If timing is a genuine problem, reschedule to a specific date rather than withdrawing. Kieri can help you plan the right timing.

Will prime contractors still require a C3PAO assessment?

They may. Primes carry their own risk for noncompliant subcontractors and can require or flow down a third party assessment regardless of the government pause. Confirm expectations with your prime and contracting officer.

Can I still submit feedback to the government?

Yes. The Request for Information is open on SAM.gov, with responses due August 14, 2026.
Cybersecurity data analysis supporting CMMC Level 2 audit preparation for defense contractors

Talk to an Expert

Tell us where you are with compliance and we’ll map out the next steps for your team.
Don't miss these

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan
Is Your Security Plan Telling the Truth?
What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.
What Does the Government Actually Require of You Today?
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
CMMC Backup Requirements and The Myths Worth Ignoring
Server backup drives in a dark data center supporting CMMC backup requirements for a defense contractor
CMMC Backup Requirements and The Myths Worth Ignoring
How to Prepare for a DIBCAC High Assessment
Analyst reviewing evidence on dark dual monitors while preparing for a DIBCAC High assessment
How to Prepare for a DIBCAC High Assessment
Out of Scope Assets - What the Final Rule Actually Changed
Abstract data cityscape tied to out of scope assets in a CMMC assessment by Kieri Solutions
Out of Scope Assets - What the Final Rule Actually Changed
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
Dark cybersecurity image with glowing data illustrating CMMC final rule compliance for defense contractors
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
Analyst reviewing code while working toward CMMC and NIST 800-171 compliance
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
CUI Assets - What Assessors Actually Evaluate
Abstract network of nodes tied to CUI assets and CMMC scope assessed by Kieri Solutions
CUI Assets - What Assessors Actually Evaluate
Do I Even Have CUI? Understanding What You Need to Protect
Abstract data network tied to finding CUI on a defense contractor network with Kieri
Do I Even Have CUI? Understanding What You Need to Protect
Why the DoD Wants Security Protection Data Protected Like CUI
Abstract data network tied to security protection data and CMMC scope assessed by Kieri
Why the DoD Wants Security Protection Data Protected Like CUI
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Cybersecurity professional conducting CMMC gap analysis for a defense contracting organization
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Network architecture visualization for a CMMC Level 2 reference architecture built on Microsoft 365 GCC High
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Why Most CMMC Documentation Fails and How to Fix It
CMMC compliance documentation policies and procedures
Why Most CMMC Documentation Fails and How to Fix It
What Passed a DOD Assessment for System Baselining and Inventories
CMMC system inventory and baseline configuration monitoring dashboard
What Passed a DOD Assessment for System Baselining and Inventories
How to Implement Mobile Code Requirements for CMMC Level 2
CMMC mobile code security controls and technical implementation
How to Implement Mobile Code Requirements for CMMC Level 2
What Does "Monitor" Actually Mean in CMMC Requirements?
CMMC monitoring requirements - access control and password security verification
What Does "Monitor" Actually Mean in CMMC Requirements?
The Version 20 Problem and How to Avoid It
CMMC compliance documentation sequence - cybersecurity program management
The Version 20 Problem and How to Avoid It
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
CMMC Level 2 compliant environment security controls and access management
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
Inside the KCD - What Makes This Documentation Different
CMMC compliance documentation templates digital security
Inside the KCD - What Makes This Documentation Different
How the Kieri Compliance Documentation and Reference Architecture Work Together
Kieri Compliance Documentation and Reference Architecture working together for CMMC Level 2 compliance
How the Kieri Compliance Documentation and Reference Architecture Work Together
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC compliance documentation and reference architecture security controls - fingerprint scanning and access management
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC Assessments by Kieri Solutions
Global cybersecurity compliance support for defense contractors under DFARS
CMMC Assessments by Kieri Solutions
CMMC Education: User vs Network Session Termination
Secure IT infrastructure design supporting CMMC Level 2 compliance for defense contractors
CMMC Education: User vs Network Session Termination
CMMC Proposed Rule has been released! 
Cybersecurity threat - CMMC compliance
CMMC Proposed Rule has been released! 
Interested in the Kieri Compliance Documentation?
Secure data transmission within CMMC compliant network architecture
Interested in the Kieri Compliance Documentation?
How to fix Outlook missing Friday January 13 2023
Interconnected defense contractor networks requiring CMMC Level 2 cybersecurity certification
How to fix Outlook missing Friday January 13 2023
C3PAO Meeting - July 26, 2021 12-1 pm EDT
NIST SP 800-171 DoD Self Assessment Services
DFARS 252.204-7012 and NIST SP 800-171 requirements
NIST SP 800-171 DoD Self Assessment Services
vSphere Health detected new issues in your environment 6.7
vcenter 6.7 alarm displays vsphere health detected new issue
vSphere Health detected new issues in your environment 6.7
vCenter Health Warning: External Platform Services Controller
Synology storage latency and disconnects on VMware
Windows Stuck in Recovery Mode Datto driver signing
Office 365 MFA App Password Missing Fix
Microsoft Teams Conference Calls & Dial-In Numbers
C: Drive Full Exchange
Exchange server very slow, services and network blank
Exchange 2016 DAG - 3 servers 2 sites
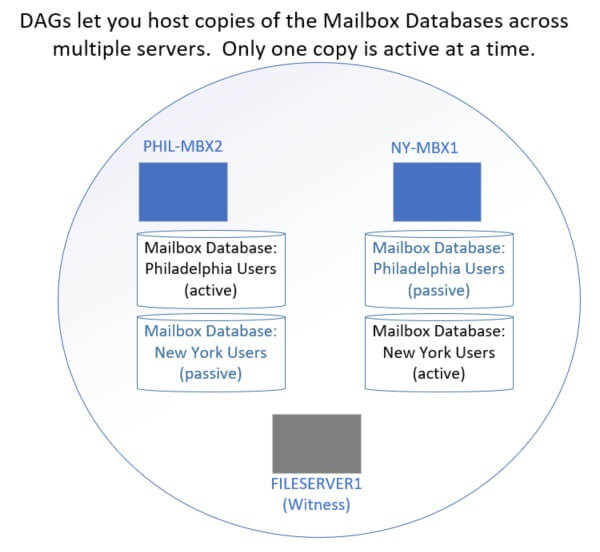
Diagram showing mailbox servers with active and passive databases. Each database is only active on one server.
Exchange 2016 DAG - 3 servers 2 sites
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
Kieri Solutions partnering with defense contractors to achieve CMMC Level 2 certification
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
warning vsphere health detected new issue memory exhaustion 6.7 vcenter
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
Step by Step: Upgrade vCenter VCSA 6.0 (or 6.5) to 6.7
How to prepare for a DoD CMMC audit and certification
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
How to prepare for a DoD CMMC audit and certification
Fix Expired vCenter Root Password (6.5 & 6.7)
How to rename Windows Server 2016 Domain Controller
Runtime Error Adding Host in VMware vCenter & ESXi
add host a general runtime error occurred vcenter 6.5 6.7
Runtime Error Adding Host in VMware vCenter & ESXi
How to fix Netapp expired self-signed certificate by creating a new one
netapp certificate expired install site cant be reached
How to fix Netapp expired self-signed certificate by creating a new one
How to register a warranty or service agreement on HPE website
hpe hp register account SAR ID service agreement warranty how accept
How to register a warranty or service agreement on HPE website
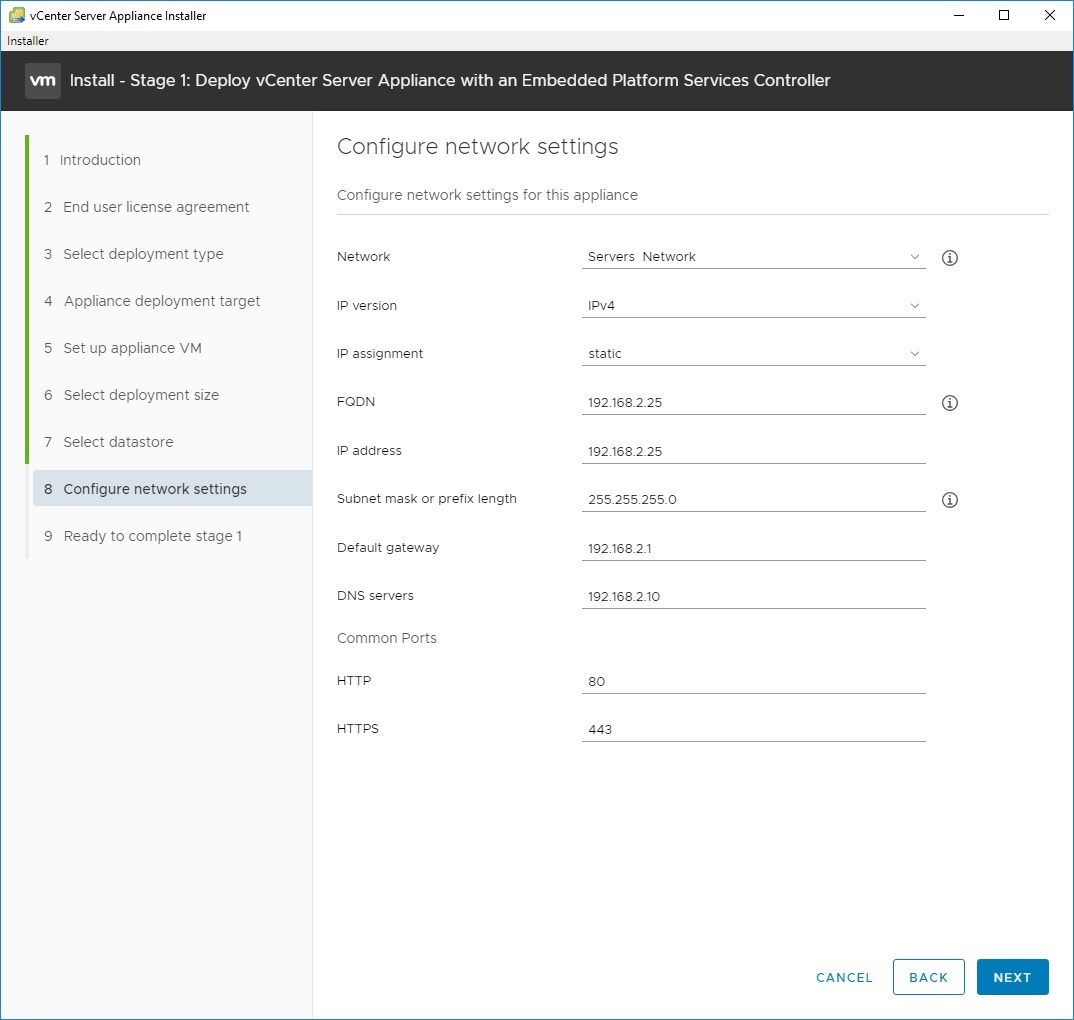
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
vcenter ip address no dns
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
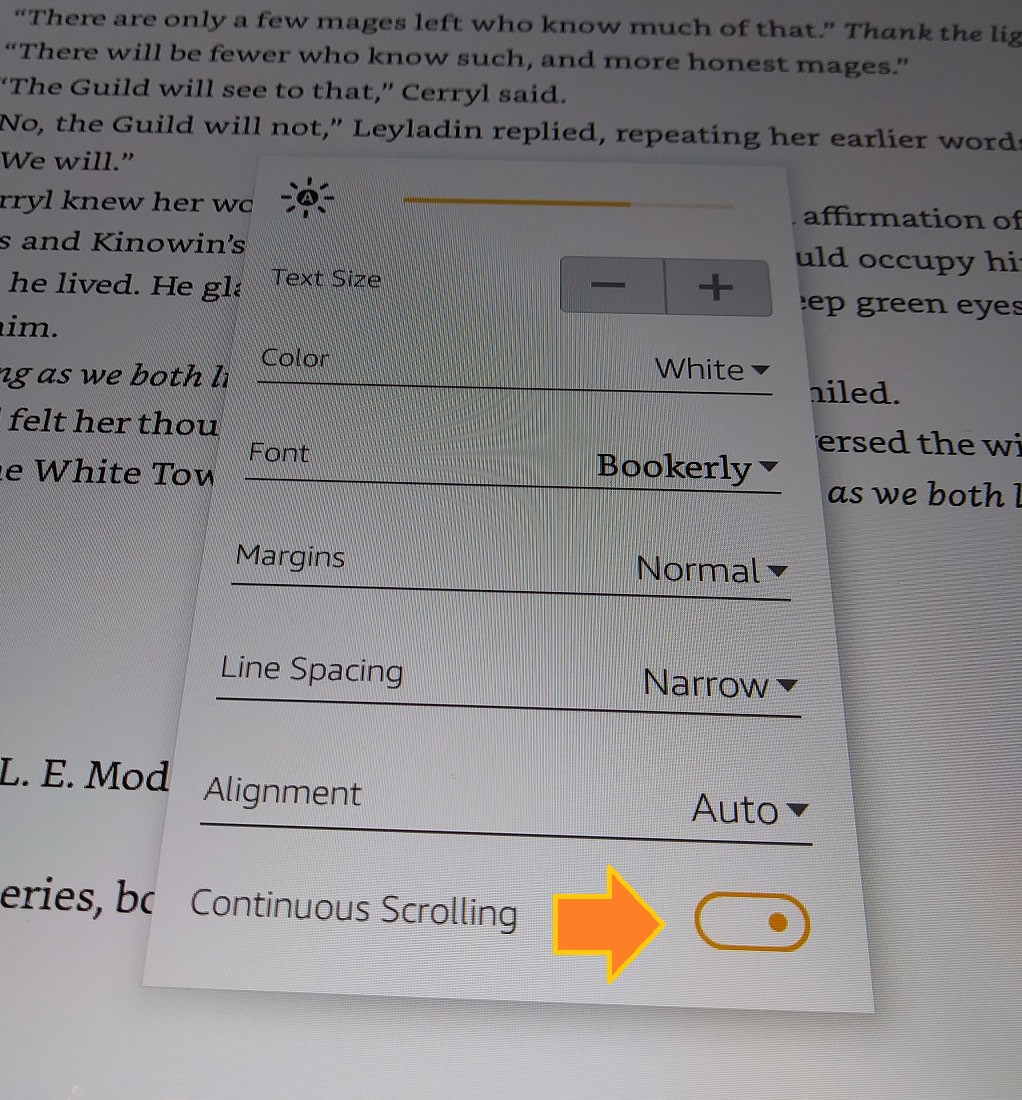
How to disable continuous scrolling on Kindle - turn on page flip
disable continuous scrolling option displays
How to disable continuous scrolling on Kindle - turn on page flip
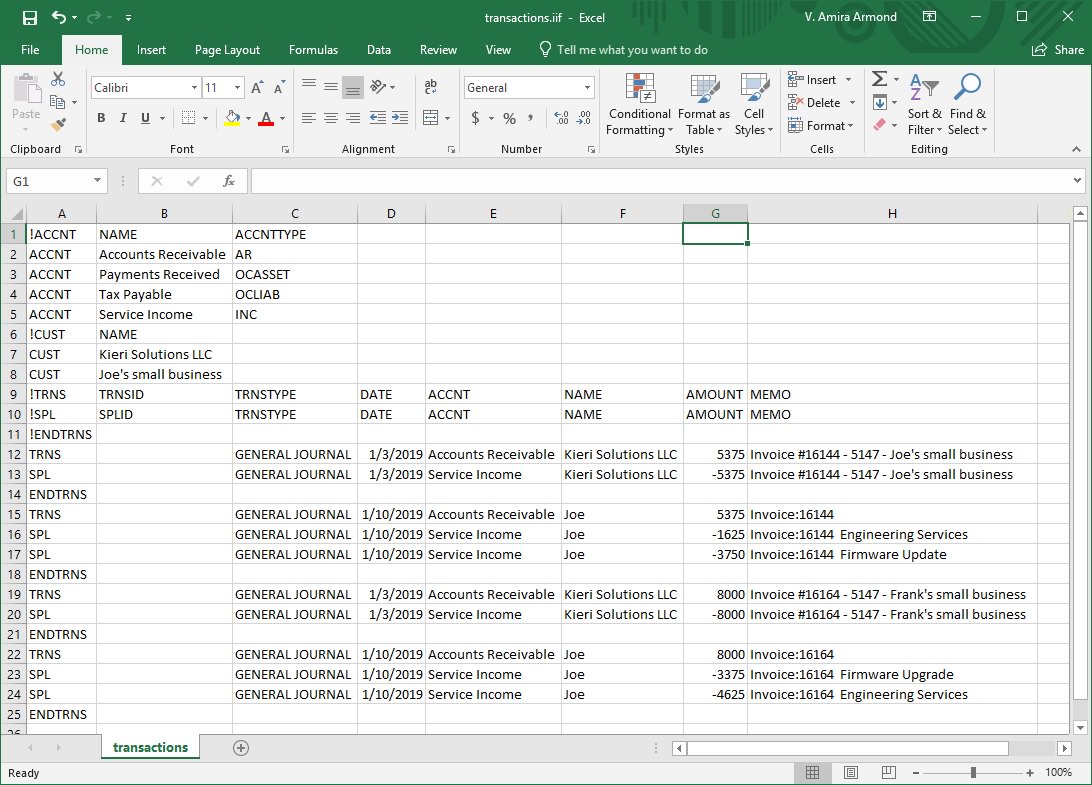
17hats how to export or convert to Excel CSV TAB XLS workbook
17hats export convert iff to csv tab excel
17hats how to export or convert to Excel CSV TAB XLS workbook
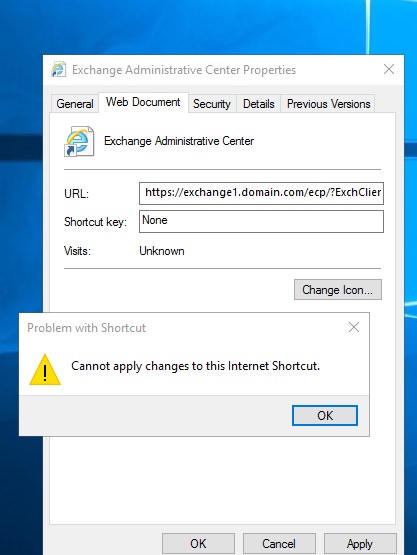
How to fix "Cannot apply changes to this Internet Shortcut" Windows
cannot apply changes to this internet shortcut 2016 2019
How to fix "Cannot apply changes to this Internet Shortcut" Windows
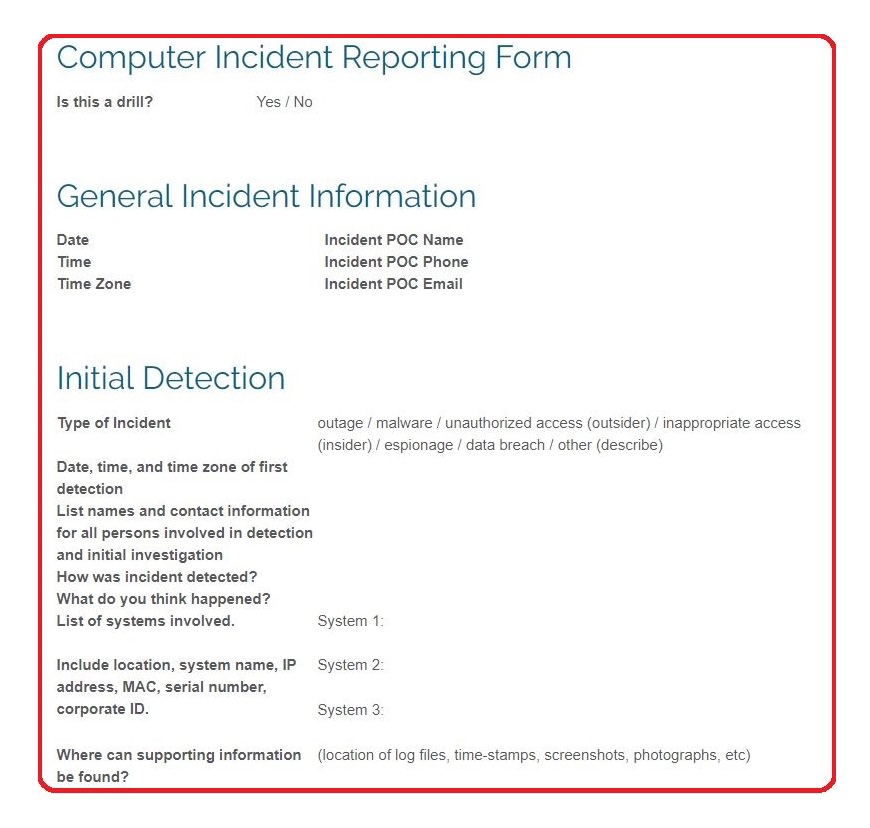
Best Free Computer Incident Response Templates and Scenarios
best free incident response reporting form cybersecurity IT
Best Free Computer Incident Response Templates and Scenarios
Firmware & System Patching Services | DC & Maryland
poweredge server raid reconfigure add disks 1 5
Firmware & System Patching Services | DC & Maryland
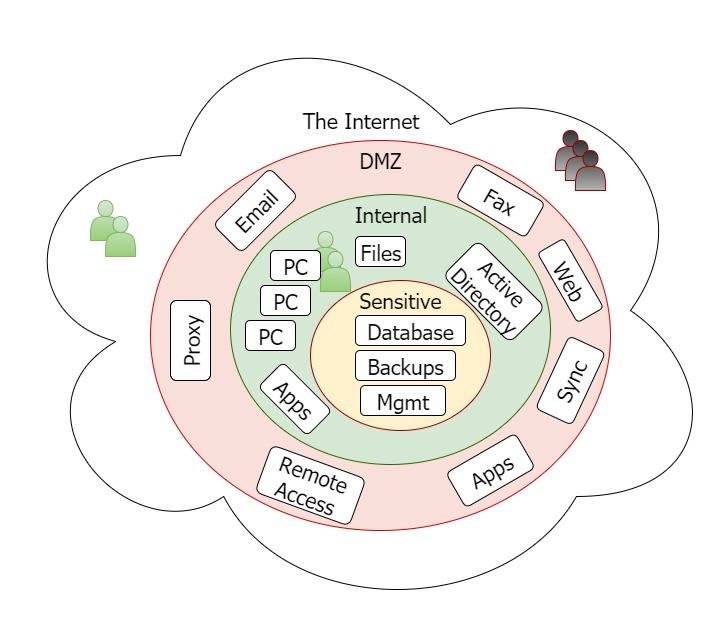
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
Best practice network segmentation and hardening prevents pivot attacks NIST
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Best practices and how to install esxi vsphere vcenter vmware and troubleshooting problems during the migration
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Disaster Recovery & Business Continuity in DC & Maryland
disaster recovery drp bcp hipaa frederick columbia gaithersburg baltimore rockville
Disaster Recovery & Business Continuity in DC & Maryland
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
installation services netapp disk shelf baltimore columbia rockville
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
SBDC - Intro to GDPR training - Frederick MD
intro gdpr overall sbdc fitci frederick
SBDC - Intro to GDPR training - Frederick MD
GDPR and Human Resources
cybersecurity cyber security hardening compliance firewall design frederick
GDPR and Human Resources
No, your computer isn't slow.
why slow computer pc repair frederick damascus mt airy md
No, your computer isn't slow.
Why you should consider a credit freeze - EquiFax hack
credit freeze equifax hack how to breach innovis
Why you should consider a credit freeze - EquiFax hack
Virtual Servers, Storage, and SAN - Why your servers are slow
cybersecurity compliance design consulting engineering
Virtual Servers, Storage, and SAN - Why your servers are slow
How to un-freeze your laptop like a pro
pc or computer problem repair damascus lisbon mt airy laytonsville
How to un-freeze your laptop like a pro
Upgrade your IT Services for the New Year
managed services it department outsource company frederick columbia germantown gaithersburg
Upgrade your IT Services for the New Year
Dell PowerEdge R730 PERC RAID online reconfiguration
poweredge server raid reconfigure add disks 1 5
Dell PowerEdge R730 PERC RAID online reconfiguration
Dreamhost HTTP error Wordpress media upload and library
dreamhost http error picture disappear upload shared wordpress
Dreamhost HTTP error Wordpress media upload and library
FortiAnalyzer Configuration problems after initial deploy
FortiAnalyzer 5.4 Storage Quota Limits for ADOM root
FortiAnalyzer Configuration problems after initial deploy
FortiAnalyzer Report: User Web Browsing by Category
fortianalyzer custom report users by category who is browsing web goofing off
FortiAnalyzer Report: User Web Browsing by Category
GDPR Consulting - What you need to know
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
GDPR Consulting - What you need to know
The #1 Computer Security Threat Just Evolved - RCE Worm
cybersecurity cyber security compliance firewall frederick md
The #1 Computer Security Threat Just Evolved - RCE Worm
Fix vSphere & vCenter Datastore Size Reverting
security design cybersecurity consulting services compliance
Fix vSphere & vCenter Datastore Size Reverting
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
conflicting vibs error vsphere upgrade metadata consultant vmware
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
Is your IT person holding the network hostage?
Server Upgrade Cybersecurity Consultant SAN Netapp Frederick
Is your IT person holding the network hostage?
4 Hiring Mistakes When Choosing an IT Company
mistakes when hire IT consultant MSP managed service provider computer support outsourcing
4 Hiring Mistakes When Choosing an IT Company
What you should know about Cloud Computing and Office 365
cloud IT department migration Office 365 Frederick Baltimore Columbia MD
What you should know about Cloud Computing and Office 365
Can You Make Our Nation Safe from Hackers?
The Ultimate Way to Protect Against Computer Theft
Kieri Solutions site icon
The Ultimate Way to Protect Against Computer Theft
Small / medium business security concerns
managed services it department outsource company frederick columbia germantown gaithersburg
Small / medium business security concerns
Approaches to security policy
cybersecurity cyber security hardening compliance firewall design frederick
Approaches to security policy

Article

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan

Article

What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.

Article

NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3

No one wants to start from blank templates.

No one wants to start from
blank templates.

Stop starting from blank templates. Get documentation proven through actual CMMC Level 2 assessment.