Open navigation menu - Kieri Solutions
CMMC Proposed Rule Analysis – What Defense Contractors Need to Know

CMMC Proposed Rule Analysis - What Defense Contractors Need to Know

Dark cybersecurity image with glowing data illustrating CMMC final rule compliance for defense contractors

In this article

Four Certified CMMC Assessors break down the major changes, the harder requirements, and the practical implications.

The CMMC rule is final. After years of speculation, interim guidance, and leaked drafts, defense contractors can now read exactly what the Department of War requires.

Four Certified CMMC Assessors from Kieri Solutions worked through the rule together: Amira Armond, Vince Scott, Brian Hubbard, and Jill Wright. Their combined experience includes dozens of assessments, hundreds of consulting engagements, and training more than 400 CMMC professionals.

Their conclusion was simple. CMMC got harder, in several unexpected ways.

POA&M Limitations Changed Dramatically

The common understanding was that you could fail up to a certain threshold of requirements and still get certified with a Plan of Action and Milestones.

That understanding was wrong.

The final rule limits POA&Ms to one-point requirements only. You have to implement every three-point and five-point requirement before the assessment. There’s one narrow exception. CUI encryption (SC.L2-3.13.11) can go on a POA&M if you’re already encrypting but the cryptography isn’t FIPS-validated yet.

On top of that, six specific one-point requirements are excluded from POA&M eligibility by name, even though they still score as one point.

Here’s what that adds up to. That leaves 63 of the 110 Level 2 requirements that cannot go on a POA&M. You have to implement them before the assessment.

Even if you qualify for a POA&M on the requirements that remain, you get 180 days to close it. Miss that window and your conditional certification expires, which makes you ineligible for the contract.

The Practical Impact

As one panelist put it, this sets a higher bar for a small machine shop than the Department sets for itself. A 2025 Inspector General report found the Department itself reaches only 70 to 79 percent implementation on these requirements.

Defense contractors have to hit near 100 %.

External Service Provider Requirements

This is where the rule delivered real surprises.

If you use an external service provider that handles CUI, that provider has to be covered under CMMC, either with its own Level 2 certification or by being assessed inside your boundary. A provider self-assessment on its own doesn’t satisfy the requirement.

This affects managed service providers, managed security service providers, and potentially Registered Practitioner Organizations.

The rule defines security protection data broadly. It covers log data, configuration data, passwords, network architecture, system security plans, vulnerability reports, antivirus information, and asset inventories. If your MSP touches CUI or that security protection data, it falls into your assessment scope, and you can’t take a self-attestation at face value.

The Cascading Effect

The panel raised a real concern. MSPs often use other service providers. An MSP might outsource SIEM analysis to an MSSP, and that MSSP now needs to be covered too.

The rule creates cascading certification requirements that weren’t in the Department’s cost estimates. One panelist estimated 5,000 to 10,000 additional companies need certification beyond the 220,000 defense contractors already counted.

The Timing Problem

There’s a dependency problem. Service providers that handle CUI generally need to be covered before their clients can certify.

When the panel first reviewed the rule, C3PAO assessments weren’t authorized yet, and joint surveillance assessments were funded only for defense contractors, not their service providers. That made the dependencies hard to satisfy. C3PAO assessments are authorized and underway now, but the practical bottleneck remains. Assessment capacity is limited, and many service providers are still early in their own compliance.

Cloud Service Provider Requirements

Cloud providers storing CUI or security protection data have to be FedRAMP Moderate authorized or FedRAMP Moderate equivalent.

Equivalency isn’t a paperwork exercise. The bar is high. The cloud provider has to hit 100 percent compliance with the FedRAMP Moderate baseline, get assessed by a FedRAMP-recognized third-party assessor, and produce a full body of evidence. That means the System Security Plan, the Security Assessment Plan, the Security Assessment Report, and continuous monitoring evidence. No POA&Ms from the third-party assessment. Everything has to be closed and validated.

You then hand that body of evidence to your C3PAO during your own CMMC Level 2 assessment, and they review it as part of your certification.

So there’s no self-attestation shortcut for equivalent clouds. If a provider gives you a marketing claim or an unvalidated SSP, that doesn’t meet the standard, and it puts your certification at risk. Check the FedRAMP Marketplace first. If your provider isn’t listed, ask for the full body of evidence before you trust the claim.

Security Protection Assets Now Fully Assessed

The earlier industry understanding was that security protection assets, your SIEM, antivirus server, and monitoring tools, were assessed for their security function but not necessarily against all 110 requirements.

The rule confirms that security protection assets are assessed against all requirements.

That expands scope a lot. Vulnerability scans of your SIEM. Audit logs from your antivirus server. Multifactor authentication for your logging infrastructure.

The panel estimated 50 to 80 percent additional assessment effort to cover this properly.

The Tool Availability Problem

One panelist raised a concern the Department may not have weighed.

Most security tools went cloud-native over the past decade. It’s hard to buy on-premises security appliances anymore. Almost everything has a cloud component.

The FedRAMP marketplace has roughly 300 authorized offerings. That’s a tiny slice of the security tools on the market.

By requiring FedRAMP for security protection data, the rule takes most security tools off the table. Small and medium businesses have the hardest time here, since many vendors only want to sell to large federal agencies.

The unintended consequence is real. Forcing companies to drop good security tools may actually increase risk to the Defense Industrial Base.

Joint Surveillance Assessment Reciprocity

Good news for early adopters. Joint surveillance assessments translate into CMMC Level 2 certifications.

A few conditions apply.

  • You need a perfect score with no open POA&Ms
  • The assessment has to align with CMMC Level 2 scoping
  • The certification is valid for three years from the original DIBCAC assessment

Companies that went through joint surveillance carry that certification for the full three years, which pushes many of them well into the later phases of the rollout before they need to recertify.

One catch the panel flagged. DIBCAC changed its policy and no longer performs POA&M closeouts. If you fail a requirement during joint surveillance, you can self-assess after remediation, but DIBCAC won’t come back to verify.

Timeline and Phases

The rule runs on a four-phase rollout, and each phase lasts a year.

Phase 1 started November 10, 2025. Most contracts in this phase call for Level 1 or Level 2 self-assessments, though contracting officers can require a Level 2 third-party assessment at their discretion.

Phase 2 begins November 10, 2026. Level 2 third-party certification becomes the standard for applicable contracts that involve CUI.

Phase 3 begins November 10, 2027, and brings Level 3 assessments into the mix.

Phase 4 begins November 10, 2028. From there, CMMC requirements are expected across all applicable contracts.

The endpoint looks a lot like the original 2019 and 2020 projections. Despite all the delays, where this lands hasn’t changed much.

Flow-Down Requirements

If a prime contractor needs Level 2 certification, its subcontractors that handle CUI need Level 2 certification too.

That sounds simple until you look at real supply chains.

A subcontractor might serve 10 primes and 20 subs of primes. If any of those primes carries a certification requirement, the subcontractor needs one.

The panel expected that while some primes may qualify for self-assessment, their subs will get hit hard with certification requirements because of how much supply chains cross over.

NIST SP 800-171 Rev 2 Locked In

The rule points to NIST SP 800-171 Rev 2 throughout. Not “current version.” Not “as updated.” Specifically Rev 2.

That takes some anxiety off the table. The requirements are locked.

It also means moving to Rev 3 would take new rulemaking. During the comment period, one panelist pushed for language that would let the revision number float with NIST updates instead of hardcoding Rev 2. The final rule kept Rev 2, and the panel doesn’t expect Rev 3 to be assessed for years.

Practical Recommendations

The panel offered several recommendations.

Evaluate your external service providers now. Figure out which ones handle CUI or security protection data. Start the conversation about their certification plans. If a provider won’t certify in time, consider bringing the service in-house.

Move to FedRAMP clouds. Ask any cloud you use for its System Security Plan and the full body of evidence. Don’t assume a commercial tier meets the requirement.

Talk to your C3PAO about scoping. With near-perfect implementation required, scoping decisions matter more than ever. Ask about specialized asset categories for systems you can’t fully secure.

Consider an enclave. Building a small, certifiable enclave and moving contract work into it is often more practical than certifying your whole corporate network.

Build the cost into your bids. The Department expects cybersecurity costs to show up in contract pricing. Raise your bids when CMMC requirements appear in the solicitation.

The Bottom Line

CMMC got harder. The external service provider requirements, the security protection asset scope, the POA&M limits, and the near-perfect self-assessment bar all add to the compliance load.

Companies that felt like they were in good shape may run into new problems. If you lean on MSPs or cloud-based security tools, you have real work ahead.

The phased timeline gives you some runway. Early joint surveillance adopters have years before they recertify. But the rule is final and in effect now, so the time to plan is already here.

Start now. Evaluate your providers. Plan your enclave. Get your scope in front of a C3PAO.

Kieri Solutions fields one of the deepest teams of certified assessors in the ecosystem. The Kieri Compliance Documentation and Kieri Reference Architecture give defense contractors scalable options for working through these requirements.
Download the KCD brochure at kieri.com/kcd

Download the KRA datasheet at kieri.com/kra

Want to talk it through? Schedule a consultation to see whether the KCD fits your compliance needs at kieri.com/schedule-consultation.


Cybersecurity data analysis supporting CMMC Level 2 audit preparation for defense contractors

Talk to an Expert

Tell us where you are with compliance and we’ll map out the next steps for your team.

Don't miss these

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan
Is Your Security Plan Telling the Truth?
What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.
What Does the Government Actually Require of You Today?
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
CMMC Backup Requirements and The Myths Worth Ignoring
Server backup drives in a dark data center supporting CMMC backup requirements for a defense contractor
CMMC Backup Requirements and The Myths Worth Ignoring
How to Prepare for a DIBCAC High Assessment
Analyst reviewing evidence on dark dual monitors while preparing for a DIBCAC High assessment
How to Prepare for a DIBCAC High Assessment
Out of Scope Assets - What the Final Rule Actually Changed
Abstract data cityscape tied to out of scope assets in a CMMC assessment by Kieri Solutions
Out of Scope Assets - What the Final Rule Actually Changed
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
Dark cybersecurity image with glowing data illustrating CMMC final rule compliance for defense contractors
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
Analyst reviewing code while working toward CMMC and NIST 800-171 compliance
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
CUI Assets - What Assessors Actually Evaluate
Abstract network of nodes tied to CUI assets and CMMC scope assessed by Kieri Solutions
CUI Assets - What Assessors Actually Evaluate
Do I Even Have CUI? Understanding What You Need to Protect
Abstract data network tied to finding CUI on a defense contractor network with Kieri
Do I Even Have CUI? Understanding What You Need to Protect
Why the DoD Wants Security Protection Data Protected Like CUI
Abstract data network tied to security protection data and CMMC scope assessed by Kieri
Why the DoD Wants Security Protection Data Protected Like CUI
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Cybersecurity professional conducting CMMC gap analysis for a defense contracting organization
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Network architecture visualization for a CMMC Level 2 reference architecture built on Microsoft 365 GCC High
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Why Most CMMC Documentation Fails and How to Fix It
CMMC compliance documentation policies and procedures
Why Most CMMC Documentation Fails and How to Fix It
What Passed a DOD Assessment for System Baselining and Inventories
CMMC system inventory and baseline configuration monitoring dashboard
What Passed a DOD Assessment for System Baselining and Inventories
How to Implement Mobile Code Requirements for CMMC Level 2
CMMC mobile code security controls and technical implementation
How to Implement Mobile Code Requirements for CMMC Level 2
What Does "Monitor" Actually Mean in CMMC Requirements?
CMMC monitoring requirements - access control and password security verification
What Does "Monitor" Actually Mean in CMMC Requirements?
The Version 20 Problem and How to Avoid It
CMMC compliance documentation sequence - cybersecurity program management
The Version 20 Problem and How to Avoid It
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
CMMC Level 2 compliant environment security controls and access management
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
Inside the KCD - What Makes This Documentation Different
CMMC compliance documentation templates digital security
Inside the KCD - What Makes This Documentation Different
How the Kieri Compliance Documentation and Reference Architecture Work Together
Kieri Compliance Documentation and Reference Architecture working together for CMMC Level 2 compliance
How the Kieri Compliance Documentation and Reference Architecture Work Together
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC compliance documentation and reference architecture security controls - fingerprint scanning and access management
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC Assessments by Kieri Solutions
Global cybersecurity compliance support for defense contractors under DFARS
CMMC Assessments by Kieri Solutions
CMMC Education: User vs Network Session Termination
Secure IT infrastructure design supporting CMMC Level 2 compliance for defense contractors
CMMC Education: User vs Network Session Termination
CMMC Proposed Rule has been released! 
Cybersecurity threat - CMMC compliance
CMMC Proposed Rule has been released! 
Interested in the Kieri Compliance Documentation?
Secure data transmission within CMMC compliant network architecture
Interested in the Kieri Compliance Documentation?
How to fix Outlook missing Friday January 13 2023
Interconnected defense contractor networks requiring CMMC Level 2 cybersecurity certification
How to fix Outlook missing Friday January 13 2023
C3PAO Meeting - July 26, 2021 12-1 pm EDT
NIST SP 800-171 DoD Self Assessment Services
DFARS 252.204-7012 and NIST SP 800-171 requirements
NIST SP 800-171 DoD Self Assessment Services
vSphere Health detected new issues in your environment 6.7
vcenter 6.7 alarm displays vsphere health detected new issue
vSphere Health detected new issues in your environment 6.7
vCenter Health Warning: External Platform Services Controller
Synology storage latency and disconnects on VMware
Windows Stuck in Recovery Mode Datto driver signing
Office 365 MFA App Password Missing Fix
Microsoft Teams Conference Calls & Dial-In Numbers
C: Drive Full Exchange
Exchange server very slow, services and network blank
Exchange 2016 DAG - 3 servers 2 sites
Diagram showing mailbox servers with active and passive databases. Each database is only active on one server.
Exchange 2016 DAG - 3 servers 2 sites
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
Kieri Solutions partnering with defense contractors to achieve CMMC Level 2 certification
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
warning vsphere health detected new issue memory exhaustion 6.7 vcenter
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
Step by Step: Upgrade vCenter VCSA 6.0 (or 6.5) to 6.7
How to prepare for a DoD CMMC audit and certification
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
How to prepare for a DoD CMMC audit and certification
Fix Expired vCenter Root Password (6.5 & 6.7)
How to rename Windows Server 2016 Domain Controller
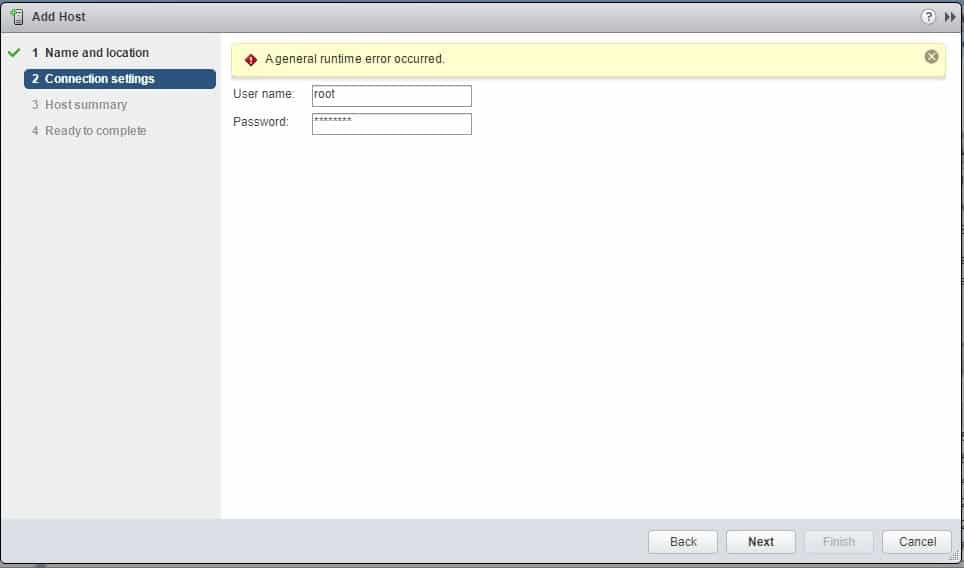
Runtime Error Adding Host in VMware vCenter & ESXi
add host a general runtime error occurred vcenter 6.5 6.7
Runtime Error Adding Host in VMware vCenter & ESXi
How to fix Netapp expired self-signed certificate by creating a new one
netapp certificate expired install site cant be reached
How to fix Netapp expired self-signed certificate by creating a new one
How to register a warranty or service agreement on HPE website
hpe hp register account SAR ID service agreement warranty how accept
How to register a warranty or service agreement on HPE website
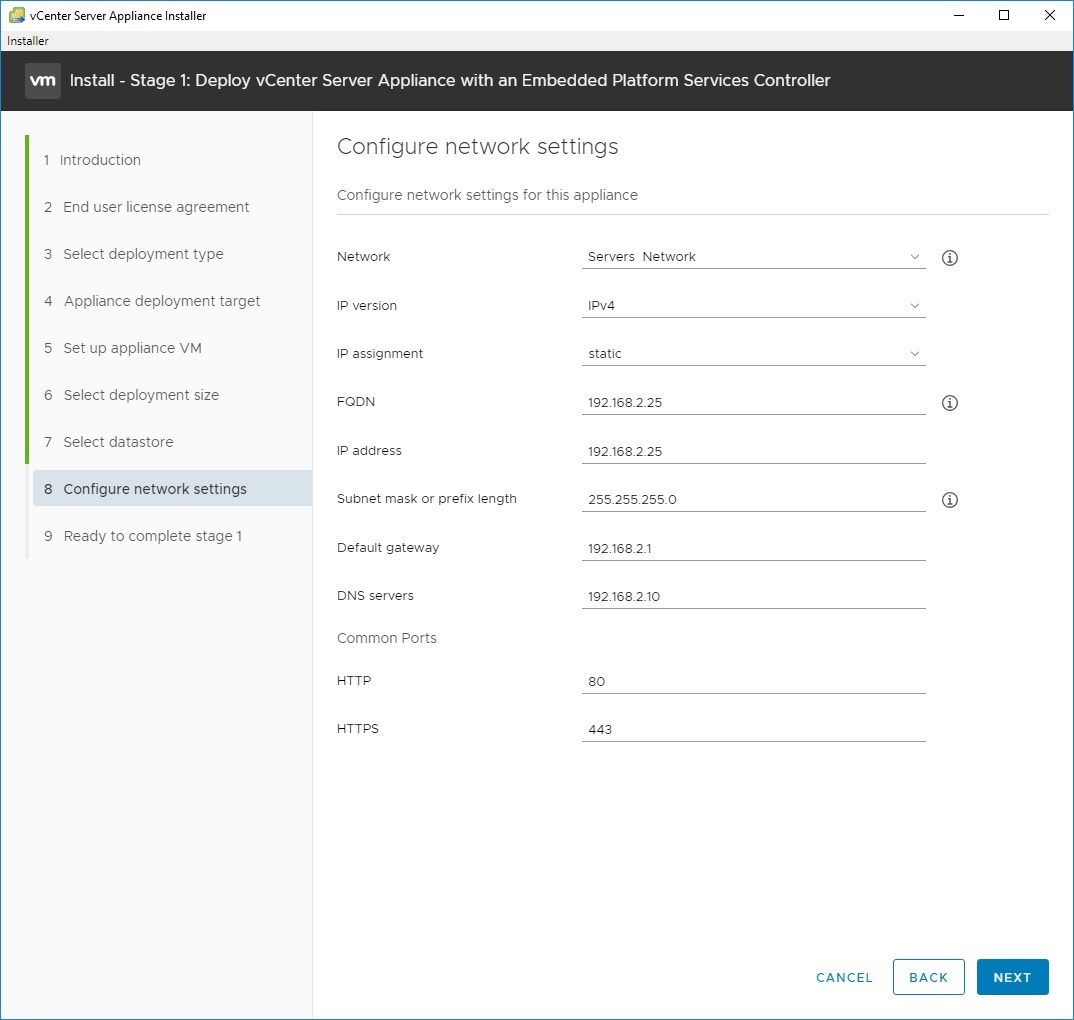
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
vcenter ip address no dns
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
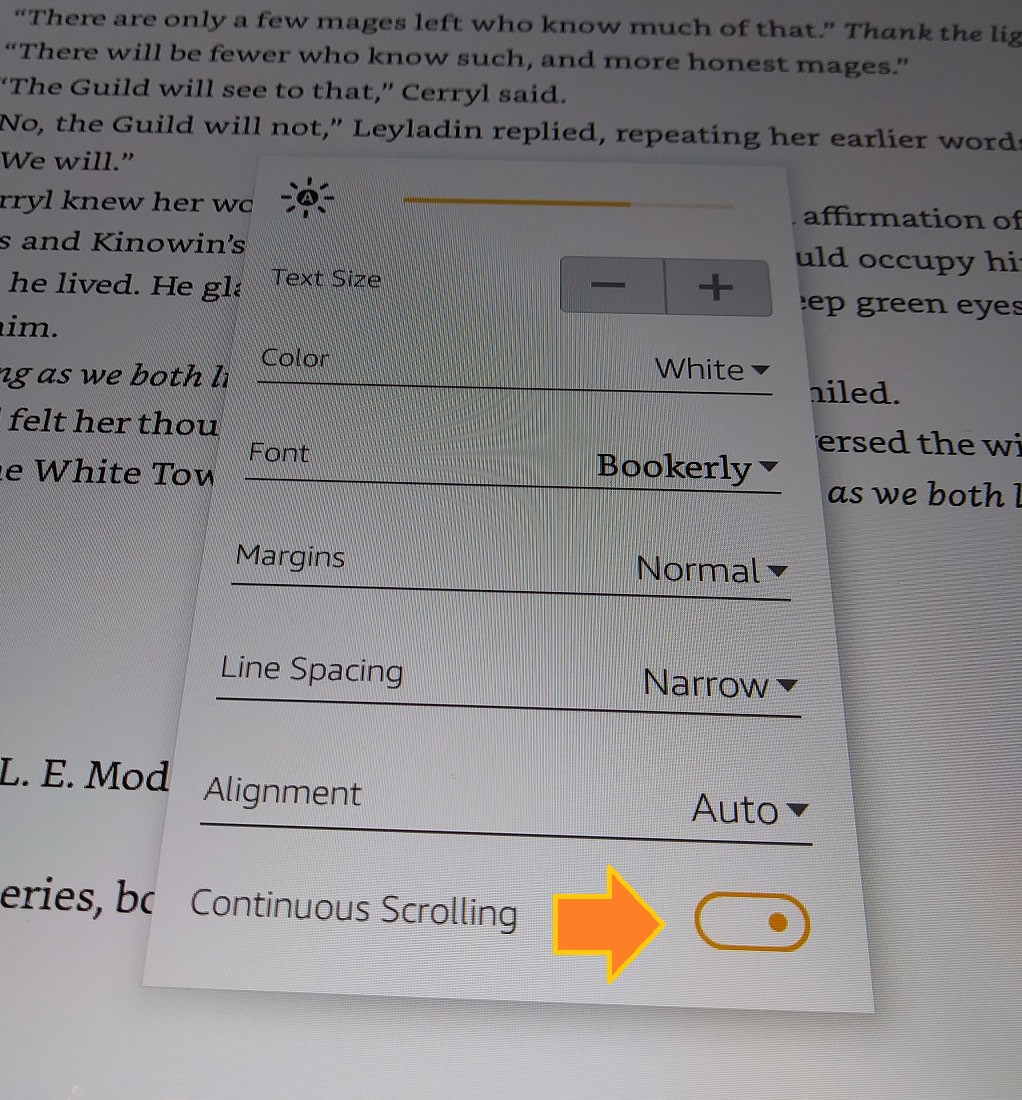
How to disable continuous scrolling on Kindle - turn on page flip
disable continuous scrolling option displays
How to disable continuous scrolling on Kindle - turn on page flip
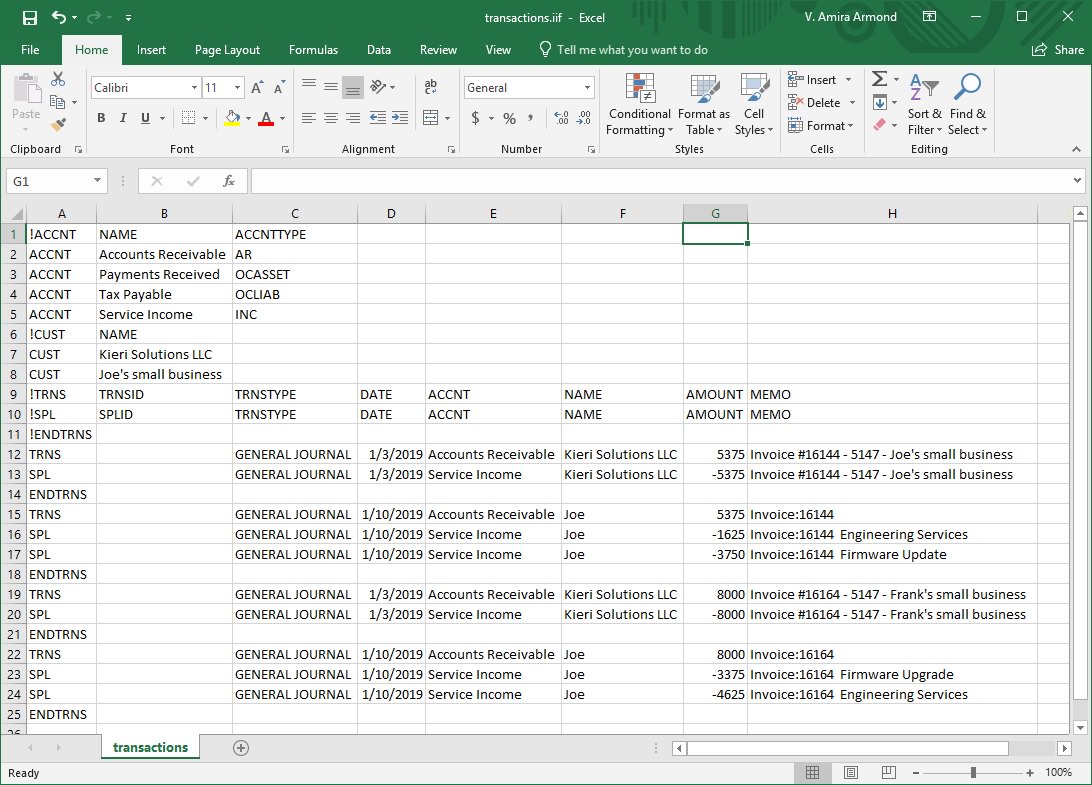
17hats how to export or convert to Excel CSV TAB XLS workbook
17hats export convert iff to csv tab excel
17hats how to export or convert to Excel CSV TAB XLS workbook
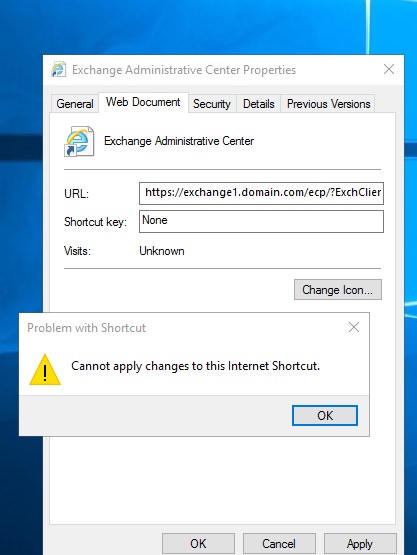
How to fix "Cannot apply changes to this Internet Shortcut" Windows
cannot apply changes to this internet shortcut 2016 2019
How to fix "Cannot apply changes to this Internet Shortcut" Windows
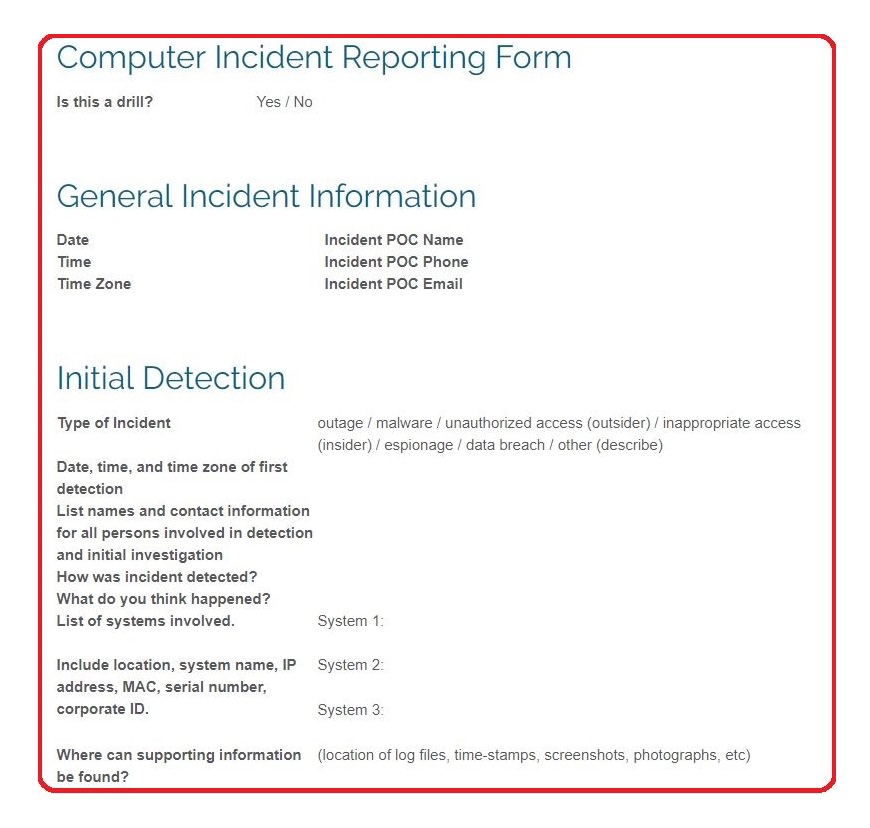
Best Free Computer Incident Response Templates and Scenarios
best free incident response reporting form cybersecurity IT
Best Free Computer Incident Response Templates and Scenarios
Firmware & System Patching Services | DC & Maryland
poweredge server raid reconfigure add disks 1 5
Firmware & System Patching Services | DC & Maryland
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
Best practice network segmentation and hardening prevents pivot attacks NIST
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Best practices and how to install esxi vsphere vcenter vmware and troubleshooting problems during the migration
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Disaster Recovery & Business Continuity in DC & Maryland
disaster recovery drp bcp hipaa frederick columbia gaithersburg baltimore rockville
Disaster Recovery & Business Continuity in DC & Maryland
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
installation services netapp disk shelf baltimore columbia rockville
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
SBDC - Intro to GDPR training - Frederick MD
intro gdpr overall sbdc fitci frederick
SBDC - Intro to GDPR training - Frederick MD
GDPR and Human Resources
cybersecurity cyber security hardening compliance firewall design frederick
GDPR and Human Resources
No, your computer isn't slow.
why slow computer pc repair frederick damascus mt airy md
No, your computer isn't slow.
Why you should consider a credit freeze - EquiFax hack
credit freeze equifax hack how to breach innovis
Why you should consider a credit freeze - EquiFax hack
Virtual Servers, Storage, and SAN - Why your servers are slow
cybersecurity compliance design consulting engineering
Virtual Servers, Storage, and SAN - Why your servers are slow
How to un-freeze your laptop like a pro
pc or computer problem repair damascus lisbon mt airy laytonsville
How to un-freeze your laptop like a pro
Upgrade your IT Services for the New Year
managed services it department outsource company frederick columbia germantown gaithersburg
Upgrade your IT Services for the New Year
Dell PowerEdge R730 PERC RAID online reconfiguration
poweredge server raid reconfigure add disks 1 5
Dell PowerEdge R730 PERC RAID online reconfiguration
Dreamhost HTTP error Wordpress media upload and library
dreamhost http error picture disappear upload shared wordpress
Dreamhost HTTP error Wordpress media upload and library
FortiAnalyzer Configuration problems after initial deploy
FortiAnalyzer 5.4 Storage Quota Limits for ADOM root
FortiAnalyzer Configuration problems after initial deploy
FortiAnalyzer Report: User Web Browsing by Category
fortianalyzer custom report users by category who is browsing web goofing off
FortiAnalyzer Report: User Web Browsing by Category
GDPR Consulting - What you need to know
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
GDPR Consulting - What you need to know
The #1 Computer Security Threat Just Evolved - RCE Worm
cybersecurity cyber security compliance firewall frederick md
The #1 Computer Security Threat Just Evolved - RCE Worm
Fix vSphere & vCenter Datastore Size Reverting
security design cybersecurity consulting services compliance
Fix vSphere & vCenter Datastore Size Reverting
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
conflicting vibs error vsphere upgrade metadata consultant vmware
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
Is your IT person holding the network hostage?
Server Upgrade Cybersecurity Consultant SAN Netapp Frederick
Is your IT person holding the network hostage?
4 Hiring Mistakes When Choosing an IT Company
mistakes when hire IT consultant MSP managed service provider computer support outsourcing
4 Hiring Mistakes When Choosing an IT Company
What you should know about Cloud Computing and Office 365
cloud IT department migration Office 365 Frederick Baltimore Columbia MD
What you should know about Cloud Computing and Office 365
Can You Make Our Nation Safe from Hackers?
The Ultimate Way to Protect Against Computer Theft
Kieri Solutions site icon
The Ultimate Way to Protect Against Computer Theft
Small / medium business security concerns
managed services it department outsource company frederick columbia germantown gaithersburg
Small / medium business security concerns
Approaches to security policy
cybersecurity cyber security hardening compliance firewall design frederick
Approaches to security policy

Article

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan

Article

What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.

Article

NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3

No one wants to start from blank templates.

No one wants to start from
blank templates.

Stop starting from blank templates. Get documentation proven through actual CMMC Level 2 assessment.