The foundation of CMMC scoping starts with knowing what CUI actually is
Before you can scope your CMMC environment, you need to answer a fundamental question: Do I even have CUI?
Most defense contractors answer this question incorrectly. They either think everything is CUI or nothing is. Both extremes create problems during an assessment.
This article breaks down what CUI actually means, how to identify it, and the three levels of expertise that separate confused contractors from confident ones.
FCI vs CUI
CMMC protects two types of information: Federal Contract Information (FCI) and Controlled Unclassified Information (CUI).
Federal Contract Information is defined in FAR Clause 52.204-21. FCI is information not intended for public release that is provided by, or generated for, the federal government under contract. FCI does not include publicly available information or simple transactional data, such as invoices or purchase orders.
If you handle data related to a federal contract that is not public and is not transactional, that data is likely FCI.
Controlled Unclassified Information is a subset of FCI. Unlike general FCI, CUI requires safeguarding or dissemination controls pursuant to applicable laws, regulations, or government-wide policies. While CUI is sensitive and should be protected, it is not classified information.
Breaking down that definition:
Controlled means we need to keep it private or maintain control over who sees it.
Unclassified means it’s not classified. This matters because some CUI looks like it should be classified. It’s right in the name—it’s not.
Information requires a certain level of detail. Simply discussing a topic related to CUI does not automatically make the conversation CUI. For example, saying “we need 15 airplane wings” is unlikely to be CUI. However, specifying the exact aluminum-carbon polymer composition, precise measurements, and manufacturing tolerances—that level of detail may elevate the information to CUI.
Understanding this distinction is critical. General discussions often do not contain enough detail to qualify as CUI, whereas documents, technical data, and detailed specifications frequently do.
Safeguarding vs Dissemination Controls
CUI becomes CUI through two mechanisms: safeguarding requirements or dissemination controls.
Safeguarding refers to the measures used to protect information from unauthorized disclosure, access, or loss. Examples include keeping documents in a locked safe, storing data in secure facilities, or implementing security controls required by NIST SP 800-171.
One common misconception is that all CUI categories have explicit safeguarding requirements. In reality, few CUI categories have explicit safeguarding requirements tied directly to the category itself. For example, Controlled Technical Information (CTI) requires protection in accordance with NIST SP 800-171, while some categories require storage within a secure facility. In practice, safeguarding-based CUI is less common than most people expect.
Dissemination controls are far more common. Dissemination means sharing. Most CUI categories exist because some law or regulation limits who can receive the information.
Common dissemination controls include:
U.S. persons only
U.S. government only
U.S. government and contractors only
No foreign nationals
When you see CUI categories in the National Archives registry, most are there because of dissemination restrictions, not safeguarding requirements.
The Three Levels of CUI Expertise
Everyone who learns about CUI progresses through three levels of understanding.
Level 1: Category List Panic
You visit the National Archives CUI category list. You scroll through dozens of categories: legal privilege, privacy information, health information, personnel records, student records, financial information.
You panic.
“My employees’ Social Security numbers are CUI! My company’s tax records are CUI! Everything is CUI!”
This is incorrect. These categories describe types of information that can be CUI when related to government contracts. Your personal employee records aren’t CUI. Government employee records you handle under contract are.
Level 2: Contract Context
You understand CUI must be provided by or generated for the government as part of a contract performance.
Not all health information is CUI—only health information you handle as part of a government contract. Not all personnel records are CUI—only government personnel records you process under contract.
This understanding dramatically reduces what you need to protect. Most of your internal business data isn’t CUI regardless of what category it might fit into.
Level 3: Legal Basis Mastery
You’ve read the actual laws and regulations behind each CUI category. You found the specific sentence requiring safeguarding or limiting dissemination. You know exactly what information qualifies and why.
This level takes years of full-time work. Most cybersecurity professionals never reach it, but it’s where true expertise lives.
To get here, you can’t stop at category descriptions. You have to follow the citation to the underlying regulation, find the specific requirement, and understand exactly what information it covers.
CUI Marking Requirements
CUI should be marked by whoever creates it.
Minimum marking: “CUI” at the top and bottom of the document.
Proper marking includes a designation indicator:
Controlled by: [Organization]
CUI Category: [Specific category]
Dissemination: [Control statement like “FEDCON” for government and contractors only]
POC: [Point of contact]
The designation indicator is critical for managing CUI effectively. Without it, you have “CUI” stamped on documents with no context about why it’s controlled, who’s responsible, or what restrictions apply.
When contractors receive CUI without proper markings, they face a choice. Technically, marking is the creator’s responsibility. If the government or your prime sends unmarked information, that’s their failure.
You’re generally justified in treating unmarked information as unmarked. But get legal guidance for your specific situation. The wrong call puts your contracts at risk.
Contract Data Requirements List (CDRL)
The CDRL specifies what controlled information a contract involves and how it should be protected.
Each page typically covers one type of sensitive information:
What data it is
What distribution statement applies
Any special handling requirements
If you receive a CDRL, you have clear guidance on what’s CUI and how to protect it. Most contractors never see one. Usually only primes receive CDRLs, and the information doesn’t always flow down properly.
If you’re a subcontractor struggling to understand what’s CUI, ask your prime for the CDRL. Push for clarity. You need this information to protect data correctly.
Controlled Technical Information: The Exception
Controlled Technical Information (CTI) breaks normal CUI rules.
CTI is technical information with military or space application that has distribution statements B through F.
Distribution Statement A means publicly releasable—not CUI.
Distribution Statements B through F impose various restrictions:
B: U.S. government agencies only
C: Government agencies and contractors
D through F: Increasingly restrictive
If a document has distribution statements B through F, treat it as CUI even without explicit CUI markings. The distribution statement itself triggers CTI status.
This catches contractors who think “it doesn’t say CUI, so it’s not CUI.” Distribution statements are CUI indicators for technical information.
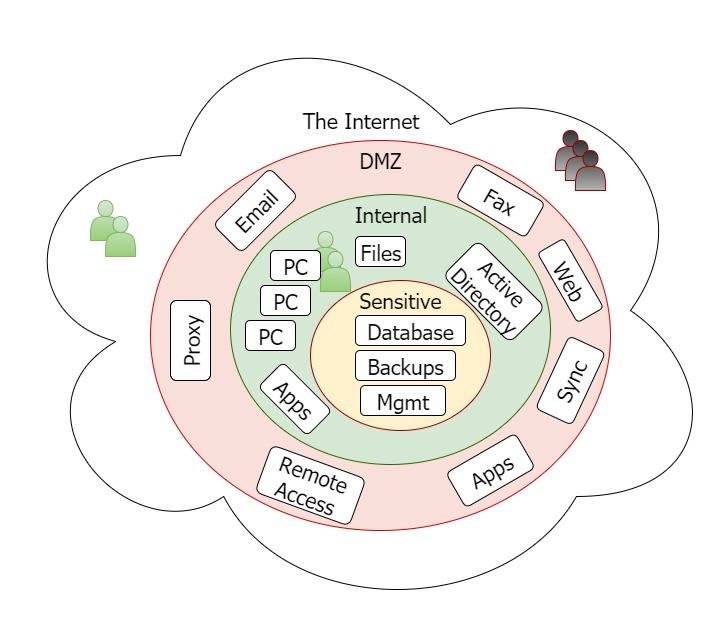
Finding CUI on Your Network
Once you understand what CUI looks like, the next step is finding it.
Where does CUI typically live?
File servers and SharePoint
User workstations (if users have opened CUI documents)
Email systems
Cloud storage applications
Databases with contract information
Physical locations with paper CUI
Who interacts with CUI?
Which employees access CUI files?
Who receives CUI via email?
Who processes CUI as part of their job function?
This inventory becomes the foundation for scoping. You can’t protect CUI if you don’t know where it is or who handles it.
Kieri Solutions helps defense contractors understand CUI requirements and build appropriate compliance programs. We’ve conducted dozens of assessments and seen every variation of CUI confusion.