Open navigation menu - Kieri Solutions
Why Your CMMC Gap Analysis Might Be Worthless – 110 Practices vs 320 Assessment Objectives

Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives

Cybersecurity professional conducting CMMC gap analysis for a defense contracting organization

In this article

If your consultant assessed you against 110 practices instead of 320 assessment objectives, you’re preparing for the wrong test


Kieri Solutions has noticed a troubling pattern.

Defense contractors approaching us for CMMC assessments have had gap analyses performed by third-party consultants. When we ask about their readiness, they reference those gap analyses with confidence.

Then we dig deeper.

We ask: did the gap analysis evaluate you against the 110 practice statements or the 320 assessment objectives?

Many folks don’t know the difference. Many have been assessed against only the practices.

Those companies think they’re ready. They’re not.

The Document Most Consultants Use

When defense contractors prepare for CMMC, they typically find NIST SP 800-171. That’s the document referenced in their DFARS contracts. It contains 110 security requirements.

Each requirement is a single sentence, generally open to interpretation.

Here’s an example from the Awareness and Training family.

“Ensure that managers, system administrators, and users of organizational systems are made aware of the security risks associated with their activities and of the applicable policies, standards, and procedures related to the security of those systems.”

That’s the entire requirement, one sentence with multiple clauses.

A weak gap analysis reads that, sees the contractor runs awareness training with a presentation on security risks, and marks it compliant.

They check the box. Move to the next requirement. Repeat 109 more times.

At the end, they feel confident. Maybe 90% ready.

The Document Assessors Actually Use

CMMC assessors don’t evaluate you against those general practice statements.

They evaluate you against 320 specific assessment objectives from NIST SP 800-171A.

Most contractors don’t even know this document exists. It’s mentioned in a small footnote on page 3 of 800-171. Four total references in the entire publication.

But 800-171A is what assessors actually use for pass/fail determinations.

That same awareness training requirement has four assessment objectives. [a] Security risks associated with organizational activities involving CUI are identified [b] Personnel are made aware of the security risks associated with their activities [c] Personnel are made aware of the applicable policies, standards, and procedures related to the security of organizational systems [d] Personnel are made aware of their responsibilities related to the security of organizational systems

Looking at the first objective. It specifically mentions CUI. The practice statement doesn’t.

If your training covers generic security risks but doesn’t specifically address CUI-related risks, you fail that objective. The practice statement alone doesn’t tell you that.

Assessment Objectives Carry the Real Detail

This pattern repeats throughout the 320 objectives. The assessment objectives in 800-171A add specificity that isn’t obvious from the practice statements.

When you read assessment objectives word by word (which is how assessors read them), you discover requirements you didn’t know existed.

“Security risks associated with organizational activities involving CUI are identified.”

An assessor looks at every word:

  • Security risks – what risks have you identified?
  • Organizational activities – what activities involve CUI in your environment?
  • Involving CUI – not generic risks, specifically CUI-related
  • Are identified – do you have documentation of this identification?

If your training doesn’t specifically identify CUI-related risks, you fail. Even if you have great generic security awareness training.

You Must Pass Every Assessment Objective

To pass a single practice (one of the 110), you must pass every assessment objective underneath it. One hundred percent.

If a practice has four assessment objectives and you pass three, you fail the practice.

Some practices have ten or more assessment objectives. You need all of them.

The math becomes brutal. At the practice level, you might feel 90% ready. At the objective level, those partial implementations become complete failures.

The Score Gap Is Devastating

Based on what we’ve observed, companies that self-assess against practice statements think they’re roughly 90% compliant.

The same companies evaluated against assessment objectives are often 50% compliant or less.

That’s not a small gap. That’s the difference between thinking you’re ready and discovering you have months of work ahead.

It’s the difference between paying for an assessment you’ll pass and paying for an assessment you’ll fail.

What Your Gap Analysis Should Include

Before paying tens of thousands for a gap analysis, ask to see a sample report.

Does it address all 320 assessment objectives individually?

Not grouped by practice. Individual evaluation of each objective with findings specific to that objective.

If the report only addresses 110 practices, shop for a different provider.

What Certified Assessors Look At

Every Certified CMMC Assessor has been trained on the assessment objectives. Not the practice statements.

During assessment, we don’t read that general sentence and make a judgment. We read each assessment objective individually. We look for evidence that specifically addresses what the objective requires.

If the objective mentions CUI specifically, we look for CUI-specific evidence. If the objective requires identification, we look for documentation of identification. If the objective requires a process, we look for evidence that process exists and is followed.

Word by word. Objective by objective. 320 times.

The CMMC Assessment Guide Adds More

Beyond 800-171A, CMMC assessors also reference the CMMC Assessment Guide.

This guide provides additional discussion, further discussion, and examples for each requirement.

The discussion sections help assessors understand intent. But they’re supplemental, not authoritative.

The assessment objectives remain the pass/fail criteria. If discussion says one thing but the objective says another, the objective governs.

Still, the Assessment Guide provides valuable context for understanding what assessors expect. Contractors preparing properly should review it alongside 800-171A.

Preparing Properly

If you’re preparing for CMMC assessment, use the right documents:

NIST SP 800-171 – The 110 requirements. Good for understanding overall scope.

NIST SP 800-171A – The 320 assessment objectives. This is what assessors actually use. Skip it and you’re not preparing for the real assessment.

CMMC Assessment Guide – Additional assessor guidance. Helpful for understanding intent.

Read each assessment objective. Ask yourself: do we have evidence that specifically addresses this? Not the general practice. This specific objective.

If you can’t point to specific evidence for a specific objective, you have a gap.

Gap Assessment Shopping List

Before engaging a gap analysis provider:

  1. Will your assessment address all 320 assessment objectives or just 110 practices?
  2. Can I see a sample report showing how you document findings per objective?
  3. Have you been through actual CMMC assessments as an assessor?
  4. What documents do you reference during your assessment?

If they only mention NIST 800-171 and not 800-171A, they’re not prepared to give you useful information.

If their sample report groups findings by practice without objective-level detail, you’re not getting what you need.

The Bottom Line

The gap between 110 practices and 320 objectives is the gap between false confidence and actual readiness.

Companies assessed at the practice level think they’re doing great. Companies assessed at the objective level discover significant work remains.

Make sure you know which assessment you’re getting. Make sure you’re preparing for the test you’ll actually take.

The certified assessor who shows up for your CMMC assessment will be reading 320 objectives, not 110 practices. Prepare accordingly.


Kieri Solutions is one of 54 authorized C3PAOs in the United States. The Kieri Compliance Documentation addresses all 320 assessment objectives, not just the 110 practice statements.
Download the KCD brochure: kieri.com/kcd

Schedule a consultation to discuss whether the KCD fits your compliance needs: kieri.com/schedule-consultation

Cybersecurity data analysis supporting CMMC Level 2 audit preparation for defense contractors

Talk to a CMMC Expert

Tell us where you are with CMMC and we’ll map out the next steps for your team.

Don't miss these

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan
Is Your Security Plan Telling the Truth?
What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.
What Does the Government Actually Require of You Today?
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
CMMC Backup Requirements and The Myths Worth Ignoring
Server backup drives in a dark data center supporting CMMC backup requirements for a defense contractor
CMMC Backup Requirements and The Myths Worth Ignoring
How to Prepare for a DIBCAC High Assessment
Analyst reviewing evidence on dark dual monitors while preparing for a DIBCAC High assessment
How to Prepare for a DIBCAC High Assessment
Out of Scope Assets - What the Final Rule Actually Changed
Abstract data cityscape tied to out of scope assets in a CMMC assessment by Kieri Solutions
Out of Scope Assets - What the Final Rule Actually Changed
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
Dark cybersecurity image with glowing data illustrating CMMC final rule compliance for defense contractors
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
Analyst reviewing code while working toward CMMC and NIST 800-171 compliance
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
CUI Assets - What Assessors Actually Evaluate
Abstract network of nodes tied to CUI assets and CMMC scope assessed by Kieri Solutions
CUI Assets - What Assessors Actually Evaluate
Do I Even Have CUI? Understanding What You Need to Protect
Abstract data network tied to finding CUI on a defense contractor network with Kieri
Do I Even Have CUI? Understanding What You Need to Protect
Why the DoD Wants Security Protection Data Protected Like CUI
Abstract data network tied to security protection data and CMMC scope assessed by Kieri
Why the DoD Wants Security Protection Data Protected Like CUI
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Cybersecurity professional conducting CMMC gap analysis for a defense contracting organization
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Network architecture visualization for a CMMC Level 2 reference architecture built on Microsoft 365 GCC High
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Why Most CMMC Documentation Fails and How to Fix It
CMMC compliance documentation policies and procedures
Why Most CMMC Documentation Fails and How to Fix It
What Passed a DOD Assessment for System Baselining and Inventories
CMMC system inventory and baseline configuration monitoring dashboard
What Passed a DOD Assessment for System Baselining and Inventories
How to Implement Mobile Code Requirements for CMMC Level 2
CMMC mobile code security controls and technical implementation
How to Implement Mobile Code Requirements for CMMC Level 2
What Does "Monitor" Actually Mean in CMMC Requirements?
CMMC monitoring requirements - access control and password security verification
What Does "Monitor" Actually Mean in CMMC Requirements?
The Version 20 Problem and How to Avoid It
CMMC compliance documentation sequence - cybersecurity program management
The Version 20 Problem and How to Avoid It
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
CMMC Level 2 compliant environment security controls and access management
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
Inside the KCD - What Makes This Documentation Different
CMMC compliance documentation templates digital security
Inside the KCD - What Makes This Documentation Different
How the Kieri Compliance Documentation and Reference Architecture Work Together
Kieri Compliance Documentation and Reference Architecture working together for CMMC Level 2 compliance
How the Kieri Compliance Documentation and Reference Architecture Work Together
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC compliance documentation and reference architecture security controls - fingerprint scanning and access management
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC Assessments by Kieri Solutions
Global cybersecurity compliance support for defense contractors under DFARS
CMMC Assessments by Kieri Solutions
CMMC Education: User vs Network Session Termination
Secure IT infrastructure design supporting CMMC Level 2 compliance for defense contractors
CMMC Education: User vs Network Session Termination
CMMC Proposed Rule has been released! 
Cybersecurity threat - CMMC compliance
CMMC Proposed Rule has been released! 
Interested in the Kieri Compliance Documentation?
Secure data transmission within CMMC compliant network architecture
Interested in the Kieri Compliance Documentation?
How to fix Outlook missing Friday January 13 2023
Interconnected defense contractor networks requiring CMMC Level 2 cybersecurity certification
How to fix Outlook missing Friday January 13 2023
C3PAO Meeting - July 26, 2021 12-1 pm EDT
NIST SP 800-171 DoD Self Assessment Services
DFARS 252.204-7012 and NIST SP 800-171 requirements
NIST SP 800-171 DoD Self Assessment Services
vSphere Health detected new issues in your environment 6.7
vcenter 6.7 alarm displays vsphere health detected new issue
vSphere Health detected new issues in your environment 6.7
vCenter Health Warning: External Platform Services Controller
Synology storage latency and disconnects on VMware
Windows Stuck in Recovery Mode Datto driver signing
Office 365 MFA App Password Missing Fix
Microsoft Teams Conference Calls & Dial-In Numbers
C: Drive Full Exchange
Exchange server very slow, services and network blank
Exchange 2016 DAG - 3 servers 2 sites
Diagram showing mailbox servers with active and passive databases. Each database is only active on one server.
Exchange 2016 DAG - 3 servers 2 sites
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
Kieri Solutions partnering with defense contractors to achieve CMMC Level 2 certification
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
warning vsphere health detected new issue memory exhaustion 6.7 vcenter
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
Step by Step: Upgrade vCenter VCSA 6.0 (or 6.5) to 6.7
How to prepare for a DoD CMMC audit and certification
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
How to prepare for a DoD CMMC audit and certification
Fix Expired vCenter Root Password (6.5 & 6.7)
How to rename Windows Server 2016 Domain Controller
Runtime Error Adding Host in VMware vCenter & ESXi
add host a general runtime error occurred vcenter 6.5 6.7
Runtime Error Adding Host in VMware vCenter & ESXi
How to fix Netapp expired self-signed certificate by creating a new one
netapp certificate expired install site cant be reached
How to fix Netapp expired self-signed certificate by creating a new one
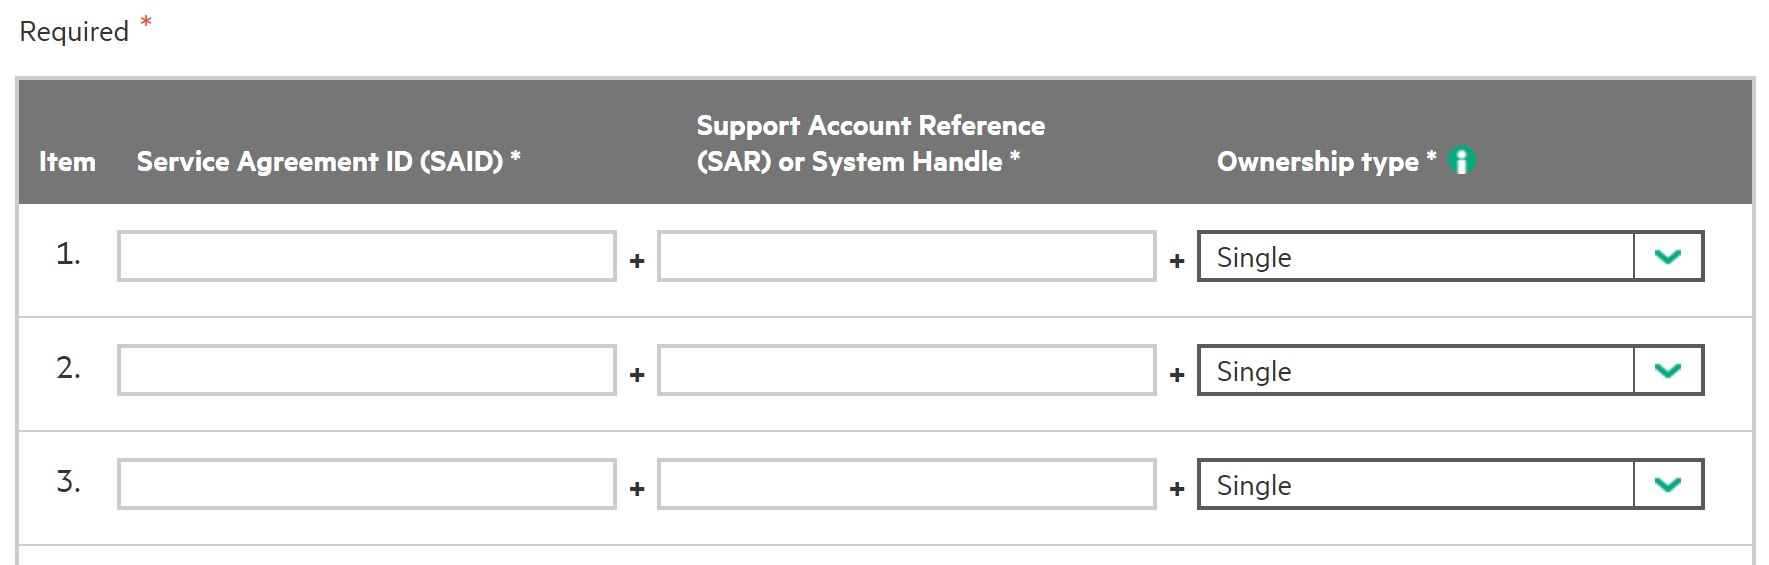
How to register a warranty or service agreement on HPE website
hpe hp register account SAR ID service agreement warranty how accept
How to register a warranty or service agreement on HPE website
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
vcenter ip address no dns
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
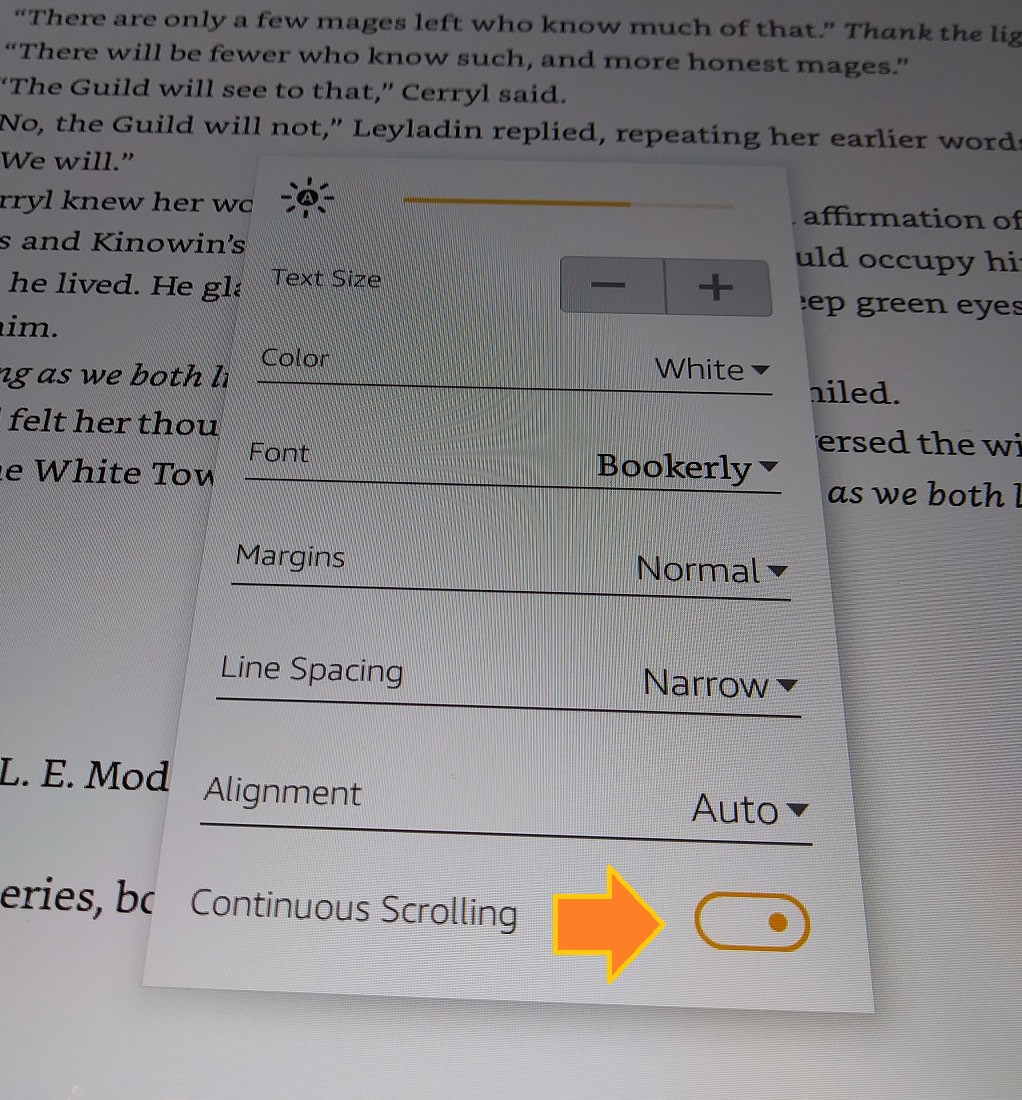
How to disable continuous scrolling on Kindle - turn on page flip
disable continuous scrolling option displays
How to disable continuous scrolling on Kindle - turn on page flip
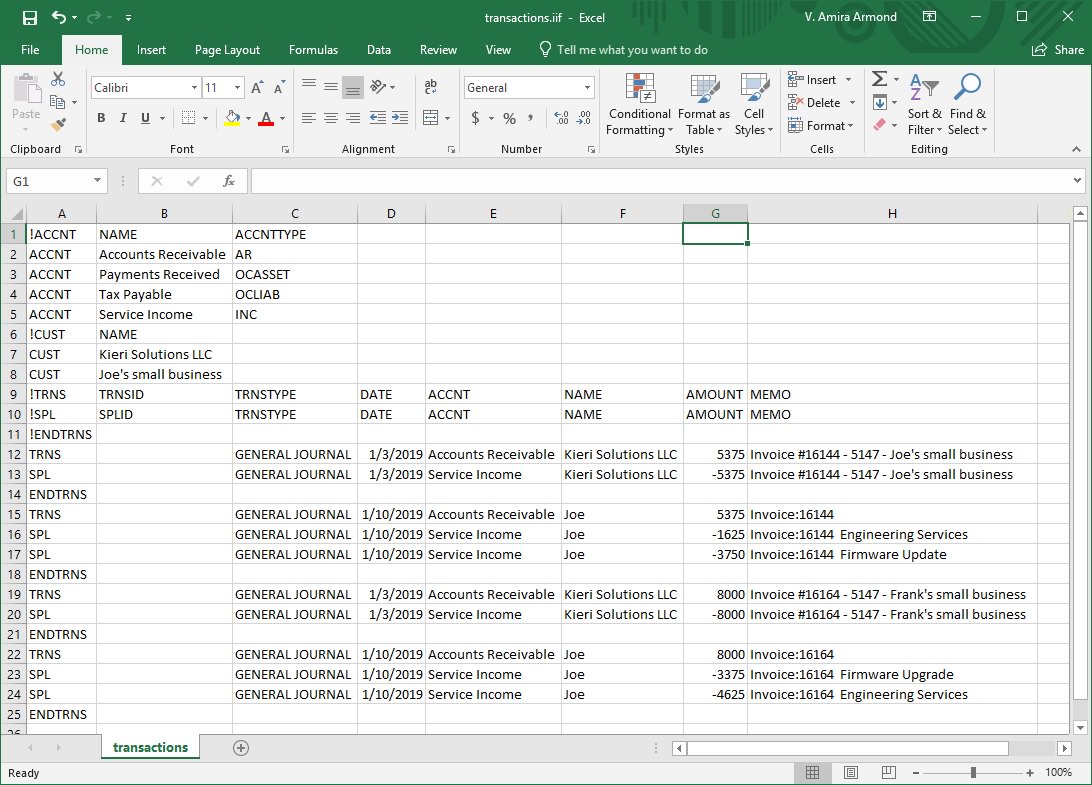
17hats how to export or convert to Excel CSV TAB XLS workbook
17hats export convert iff to csv tab excel
17hats how to export or convert to Excel CSV TAB XLS workbook
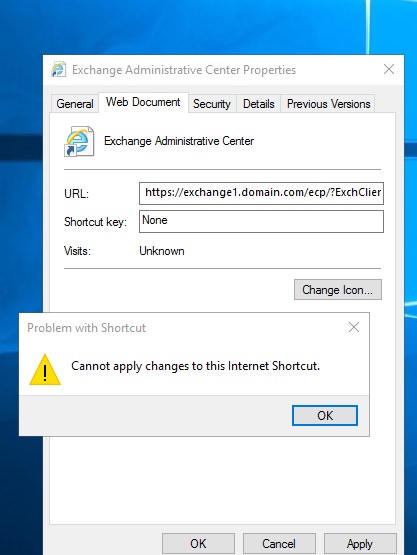
How to fix "Cannot apply changes to this Internet Shortcut" Windows
cannot apply changes to this internet shortcut 2016 2019
How to fix "Cannot apply changes to this Internet Shortcut" Windows
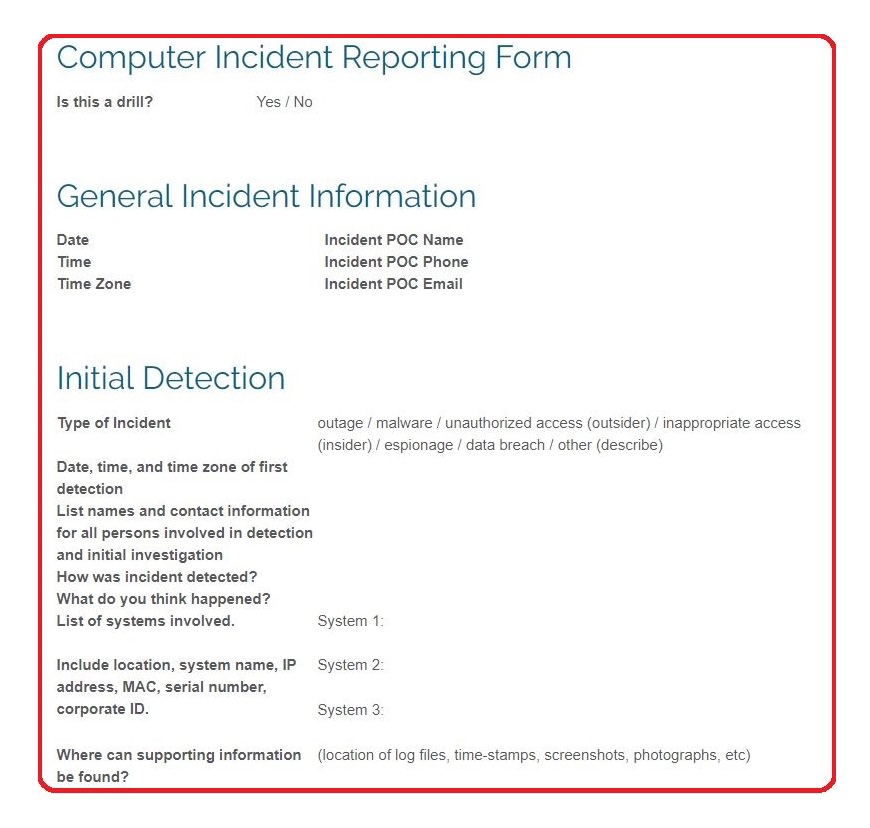
Best Free Computer Incident Response Templates and Scenarios
best free incident response reporting form cybersecurity IT
Best Free Computer Incident Response Templates and Scenarios
Firmware & System Patching Services | DC & Maryland
poweredge server raid reconfigure add disks 1 5
Firmware & System Patching Services | DC & Maryland
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
Best practice network segmentation and hardening prevents pivot attacks NIST
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Best practices and how to install esxi vsphere vcenter vmware and troubleshooting problems during the migration
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Disaster Recovery & Business Continuity in DC & Maryland
disaster recovery drp bcp hipaa frederick columbia gaithersburg baltimore rockville
Disaster Recovery & Business Continuity in DC & Maryland
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
installation services netapp disk shelf baltimore columbia rockville
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
SBDC - Intro to GDPR training - Frederick MD
intro gdpr overall sbdc fitci frederick
SBDC - Intro to GDPR training - Frederick MD
GDPR and Human Resources
cybersecurity cyber security hardening compliance firewall design frederick
GDPR and Human Resources
No, your computer isn't slow.
why slow computer pc repair frederick damascus mt airy md
No, your computer isn't slow.
Why you should consider a credit freeze - EquiFax hack
credit freeze equifax hack how to breach innovis
Why you should consider a credit freeze - EquiFax hack
Virtual Servers, Storage, and SAN - Why your servers are slow
cybersecurity compliance design consulting engineering
Virtual Servers, Storage, and SAN - Why your servers are slow
How to un-freeze your laptop like a pro
pc or computer problem repair damascus lisbon mt airy laytonsville
How to un-freeze your laptop like a pro
Upgrade your IT Services for the New Year
managed services it department outsource company frederick columbia germantown gaithersburg
Upgrade your IT Services for the New Year
Dell PowerEdge R730 PERC RAID online reconfiguration
poweredge server raid reconfigure add disks 1 5
Dell PowerEdge R730 PERC RAID online reconfiguration
Dreamhost HTTP error Wordpress media upload and library
dreamhost http error picture disappear upload shared wordpress
Dreamhost HTTP error Wordpress media upload and library
FortiAnalyzer Configuration problems after initial deploy
FortiAnalyzer 5.4 Storage Quota Limits for ADOM root
FortiAnalyzer Configuration problems after initial deploy
FortiAnalyzer Report: User Web Browsing by Category
fortianalyzer custom report users by category who is browsing web goofing off
FortiAnalyzer Report: User Web Browsing by Category
GDPR Consulting - What you need to know
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
GDPR Consulting - What you need to know
The #1 Computer Security Threat Just Evolved - RCE Worm
cybersecurity cyber security compliance firewall frederick md
The #1 Computer Security Threat Just Evolved - RCE Worm
Fix vSphere & vCenter Datastore Size Reverting
security design cybersecurity consulting services compliance
Fix vSphere & vCenter Datastore Size Reverting
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
conflicting vibs error vsphere upgrade metadata consultant vmware
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
Is your IT person holding the network hostage?
Server Upgrade Cybersecurity Consultant SAN Netapp Frederick
Is your IT person holding the network hostage?
4 Hiring Mistakes When Choosing an IT Company
mistakes when hire IT consultant MSP managed service provider computer support outsourcing
4 Hiring Mistakes When Choosing an IT Company
What you should know about Cloud Computing and Office 365
cloud IT department migration Office 365 Frederick Baltimore Columbia MD
What you should know about Cloud Computing and Office 365
Can You Make Our Nation Safe from Hackers?
The Ultimate Way to Protect Against Computer Theft
Kieri Solutions site icon
The Ultimate Way to Protect Against Computer Theft
Small / medium business security concerns
managed services it department outsource company frederick columbia germantown gaithersburg
Small / medium business security concerns
Approaches to security policy
cybersecurity cyber security hardening compliance firewall design frederick
Approaches to security policy

Article

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan

Article

What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.

Article

NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3

No one wants to start from blank templates.

No one wants to start from
blank templates.

Stop starting from blank templates. Get documentation proven through actual CMMC Level 2 assessment.