Open navigation menu - Kieri Solutions
How the Kieri Compliance Documentation and Reference Architecture Work Together

How the Kieri Compliance Documentation and Reference Architecture Work Together

Kieri Compliance Documentation and Reference Architecture working together for CMMC Level 2 compliance

In this article

A detailed walkthrough showing how technology-agnostic policies combine with Microsoft 365 GCC-High implementation for complete CMMC Level 2 compliance


CMMC compliance documentation and reference architecture are two distinct components of Level 2 compliance. Manual processes and technical configurations.

Most compliance solutions address one or the other. Documentation packages give you policies and procedures but leave technology implementation to you. Technical solutions configure systems but assume you’ll figure out the paperwork yourself.

The Kieri Compliance Documentation and Kieri Reference Architecture were designed as one package split into two pieces. They integrate at every requirement level.

This article walks through a single CMMC requirement to show exactly how that integration works.

The Split Between Manual and Technical Compliance

CMMC Level 2 has 320 assessment objectives across 110 security requirements. When you break down what those objectives actually require, a pattern emerges.

The majority are manual processes. How you authorize users. How you track changes. How you review access. How you train employees. How you document procedures.

The KCD addresses over 240 of those 320 assessment objectives. Policies, procedures, user agreements, databases, maintenance checklists. All the people-powered compliance work that applies regardless of what technology you use.

The remaining objectives are technology-specific. How your systems enforce password requirements. How your antivirus scans for threats. How your logging captures events. How your configurations restrict access.

The KRA addresses those technology objectives for a specific platform: Microsoft 365 GCC-High with Windows 10 or 11 computers.

Why Keep Them Separate

Not every organization needs the KRA.

Some companies already have established technology platforms. They’re using AWS. They have existing Azure configurations. They’ve invested in different security tools.

Those organizations still benefit from the KCD. The manual processes remain the same regardless of technology. Policies work universally. Procedures translate across platforms. The compliance workload is mostly people-powered anyway.

The KRA serves organizations wanting a proven architecture. Those who don’t want to figure out technology implementation themselves. Those who want explicit instructions based on a system that actually passed assessment.

By splitting the package, companies choose what they need. KCD for everyone. KRA for those wanting Microsoft 365 GCC-High implementation.

Mobile Code – One Requirement, Full Integration

To demonstrate how the KCD and KRA integrate, let’s walk through the mobile code requirement. It’s one of the most misunderstood CMMC requirements, making it a good example.

What Mobile Code Actually Means

Mobile code isn’t about cell phones. It’s computer code that executes inside a different application.

Office macros. Browser scripts. PowerShell scripts. PDF reader plugins. Any code that runs within the context of a trusted application.

CMMC requires you to control and monitor mobile code. That sounds simple until you try to implement it.

The KCD Approach – Manual Processes

The KCD System Security Plan starts with explanation. What mobile code means. Why it matters. How most companies approach it.

Then it provides recommended implementation language. Not blank templates. Actual statements describing how a compliant organization handles mobile code.

Software inventory tracking. The KCD says you’ll maintain a database listing what mobile code is authorized. Google Chrome authorized to run JavaScript and PDF mobile code. Microsoft Office authorized for specific macro scenarios. Everything documented.

Policy requirements. The KCD includes policies requiring identification of authorized mobile code, restrictions on unauthorized types, and antivirus configuration for mobile code control.

Database definitions. The KCD provides the structure for tracking authorized software, including mobile code authorizations. Real examples showing what documentation looks like.

This covers the manual compliance side. You know what mobile code is authorized. You have policies governing it. You maintain records proving authorization decisions.

The KRA Approach – Technical Implementation

The KRA picks up where the KCD leaves off. How do you actually configure systems to control and monitor mobile code?

Configuration instructions. The KRA includes about 350 tasks for building your Microsoft 365 tenant. Mobile code appears in antivirus policies and attack surface reduction rules.

Granular settings. The Microsoft secure configuration baselines document contains over 1,000 settings. Each setting includes the recommended configuration, the source of that recommendation (Microsoft, government guidelines, Kieri testing), and notes about functionality impact.

Specific policies created:

  • Antivirus policy evaluating mobile code and blocking malicious execution
  • Attack surface reduction blocking JavaScript and VBScript from launching executables
  • Settings preventing Adobe Reader from creating child processes
  • Browser script scanning configurations

Monitoring procedures. The KRA audit log procedure includes queries for mobile code monitoring. One query pulls all PowerShell scripts executed recently. Another shows processes started by web browsers. Copy-paste into Microsoft Defender for Endpoint and run.

Combined System Security Plan

When you merge the KCD and KRA content, your System Security Plan covers everything assessors need to see.

The non-technical portions from the KCD explain your policies, procedures, and authorization processes. You maintain a software inventory. You authorize mobile code technologies. You have policies governing mobile code use.

The technical portions from the KRA describe exact implementation. Mobile code is controlled with Defender and SmartScreen. Specific policies enforce restrictions. Browser scripts are scanned. Certain dangerous combinations are blocked. Monitoring uses Microsoft Defender for Endpoint with specific queries.

Assessors see both the manual compliance work and the technical implementation. Everything connects.

The Configuration Baselines Document

One of the most valuable components of the KRA is the Microsoft secure configuration baselines spreadsheet.

Over 1,000 settings across multiple tabs. Antivirus. Attack surface reduction. Device restrictions. Endpoint protection. Each setting documented with:

Recommended value. What the setting should be configured to.

Source. Where the recommendation comes from. Microsoft baseline. SCUBA secure technical guide. Kieri testing and least privilege analysis.

Notes. Explanation of why that value was chosen. If the recommended setting causes functionality problems, what alternative to use and why.

This document serves multiple purposes during assessment.

It proves you’re following secure configuration baselines. Assessors see you’re applying industry-standard or government-recommended settings.

It demonstrates least privilege review. Every setting was evaluated for whether it could be made more restrictive without breaking functionality.

It provides your baseline documentation. When assessors ask what your standard configuration looks like, you have 1,000+ settings documented.

Functionality Testing Built In

The KRA includes 30-40 functionality tests designed for acceptance testing.

Can you send email and have it arrive? Does FIPS mode show enabled in the registry? Do security policies apply correctly? Can users access what they need while being blocked from what they shouldn’t?

If you build the environment yourself, run every test before deploying to production. If Kieri builds it for you, they run these tests before handover.

This acceptance testing approach catches problems before they affect users. It also generates evidence showing your environment works as designed.

The Maintenance Reality

Kieri has operated on the KRA for over three years. Their maintenance reality:

One part-time system administrator. One extremely part-time virtual CISO (one meeting per month).

That’s the staffing required to keep the environment compliant and functional.

This matters because CMMC compliance isn’t a one-time achievement. You need to maintain it. If maintenance requires dedicated full-time staff, many small contractors can’t sustain it.

The KRA was designed for the staffing reality of small organizations.

Who Benefits from Each Product

KCD Only

Any company pursuing CMMC Level 2, regardless of technology platform.

Fortune 500 companies using the KCD appreciate the manual process documentation even when they have their own technology implementations. Small contractors with existing IT infrastructure use the KCD to build their compliance program around current systems.

The KCD works universally because manual compliance processes are technology-agnostic.

KCD Plus KRA

Organizations wanting complete implementation on Microsoft 365 GCC-High.

Those who don’t want to figure out technology configurations themselves. Those who want proven architecture based on a system that passed DIBCAC assessment. Those who prefer real laptops over virtual desktop solutions.

The combination provides everything needed for CMMC Level 2. Documentation plus technology. Manual processes plus technical controls. Policies plus configurations.

Getting Started

Evaluate which products fit your situation.

Already have technology platforms? Start with the KCD. Apply the manual compliance processes to your existing systems.

Need proven architecture? Consider the KCD plus KRA combination. Get both the documentation and the technical blueprint.

Want to see details? Download the KCD brochure at kieri.com/kcd and the KRA datasheet at kieri.com/kra.

Have questions? Schedule a consultation to discuss whether the KCD fits your compliance needs: kieri.com/schedule-consultation

The KCD and KRA exist because Kieri needed them first. They built the documentation. They designed the architecture. They passed assessment with both. Now they share the complete package with defense contractors facing the same compliance challenge.


Kieri Solutions is one of 54 authorized C3PAOs in the United States. Both the KCD and KRA are based on what we used to pass our own CMMC Level 2 assessment with DIBCAC. Over 100 companies use the KCD, including Fortune 100 and Fortune 500 organizations.

Ready for Assessment? Visit kieri.com/assess to learn about CMMC Level 2 certification services.

Cybersecurity data analysis supporting CMMC Level 2 audit preparation for defense contractors

Talk to an Expert

Tell us where you are with compliance and we’ll map out the next steps for your team.
Don't miss these

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan
Is Your Security Plan Telling the Truth?
What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.
What Does the Government Actually Require of You Today?
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
CMMC Backup Requirements and The Myths Worth Ignoring
Server backup drives in a dark data center supporting CMMC backup requirements for a defense contractor
CMMC Backup Requirements and The Myths Worth Ignoring
How to Prepare for a DIBCAC High Assessment
Analyst reviewing evidence on dark dual monitors while preparing for a DIBCAC High assessment
How to Prepare for a DIBCAC High Assessment
Out of Scope Assets - What the Final Rule Actually Changed
Abstract data cityscape tied to out of scope assets in a CMMC assessment by Kieri Solutions
Out of Scope Assets - What the Final Rule Actually Changed
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
Dark cybersecurity image with glowing data illustrating CMMC final rule compliance for defense contractors
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
Analyst reviewing code while working toward CMMC and NIST 800-171 compliance
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
CUI Assets - What Assessors Actually Evaluate
Abstract network of nodes tied to CUI assets and CMMC scope assessed by Kieri Solutions
CUI Assets - What Assessors Actually Evaluate
Do I Even Have CUI? Understanding What You Need to Protect
Abstract data network tied to finding CUI on a defense contractor network with Kieri
Do I Even Have CUI? Understanding What You Need to Protect
Why the DoD Wants Security Protection Data Protected Like CUI
Abstract data network tied to security protection data and CMMC scope assessed by Kieri
Why the DoD Wants Security Protection Data Protected Like CUI
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Cybersecurity professional conducting CMMC gap analysis for a defense contracting organization
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Network architecture visualization for a CMMC Level 2 reference architecture built on Microsoft 365 GCC High
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Why Most CMMC Documentation Fails and How to Fix It
CMMC compliance documentation policies and procedures
Why Most CMMC Documentation Fails and How to Fix It
What Passed a DOD Assessment for System Baselining and Inventories
CMMC system inventory and baseline configuration monitoring dashboard
What Passed a DOD Assessment for System Baselining and Inventories
How to Implement Mobile Code Requirements for CMMC Level 2
CMMC mobile code security controls and technical implementation
How to Implement Mobile Code Requirements for CMMC Level 2
What Does "Monitor" Actually Mean in CMMC Requirements?
CMMC monitoring requirements - access control and password security verification
What Does "Monitor" Actually Mean in CMMC Requirements?
The Version 20 Problem and How to Avoid It
CMMC compliance documentation sequence - cybersecurity program management
The Version 20 Problem and How to Avoid It
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
CMMC Level 2 compliant environment security controls and access management
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
Inside the KCD - What Makes This Documentation Different
CMMC compliance documentation templates digital security
Inside the KCD - What Makes This Documentation Different
How the Kieri Compliance Documentation and Reference Architecture Work Together
Kieri Compliance Documentation and Reference Architecture working together for CMMC Level 2 compliance
How the Kieri Compliance Documentation and Reference Architecture Work Together
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC compliance documentation and reference architecture security controls - fingerprint scanning and access management
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC Assessments by Kieri Solutions
Global cybersecurity compliance support for defense contractors under DFARS
CMMC Assessments by Kieri Solutions
CMMC Education: User vs Network Session Termination
Secure IT infrastructure design supporting CMMC Level 2 compliance for defense contractors
CMMC Education: User vs Network Session Termination
CMMC Proposed Rule has been released! 
Cybersecurity threat - CMMC compliance
CMMC Proposed Rule has been released! 
Interested in the Kieri Compliance Documentation?
Secure data transmission within CMMC compliant network architecture
Interested in the Kieri Compliance Documentation?
How to fix Outlook missing Friday January 13 2023
Interconnected defense contractor networks requiring CMMC Level 2 cybersecurity certification
How to fix Outlook missing Friday January 13 2023
C3PAO Meeting - July 26, 2021 12-1 pm EDT
NIST SP 800-171 DoD Self Assessment Services
DFARS 252.204-7012 and NIST SP 800-171 requirements
NIST SP 800-171 DoD Self Assessment Services
vSphere Health detected new issues in your environment 6.7
vcenter 6.7 alarm displays vsphere health detected new issue
vSphere Health detected new issues in your environment 6.7
vCenter Health Warning: External Platform Services Controller
Synology storage latency and disconnects on VMware
Windows Stuck in Recovery Mode Datto driver signing
Office 365 MFA App Password Missing Fix
Microsoft Teams Conference Calls & Dial-In Numbers
C: Drive Full Exchange
Exchange server very slow, services and network blank
Exchange 2016 DAG - 3 servers 2 sites
Diagram showing mailbox servers with active and passive databases. Each database is only active on one server.
Exchange 2016 DAG - 3 servers 2 sites
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
Kieri Solutions partnering with defense contractors to achieve CMMC Level 2 certification
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
warning vsphere health detected new issue memory exhaustion 6.7 vcenter
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
Step by Step: Upgrade vCenter VCSA 6.0 (or 6.5) to 6.7
How to prepare for a DoD CMMC audit and certification
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
How to prepare for a DoD CMMC audit and certification
Fix Expired vCenter Root Password (6.5 & 6.7)
How to rename Windows Server 2016 Domain Controller
Runtime Error Adding Host in VMware vCenter & ESXi
add host a general runtime error occurred vcenter 6.5 6.7
Runtime Error Adding Host in VMware vCenter & ESXi
How to fix Netapp expired self-signed certificate by creating a new one
netapp certificate expired install site cant be reached
How to fix Netapp expired self-signed certificate by creating a new one
How to register a warranty or service agreement on HPE website
hpe hp register account SAR ID service agreement warranty how accept
How to register a warranty or service agreement on HPE website
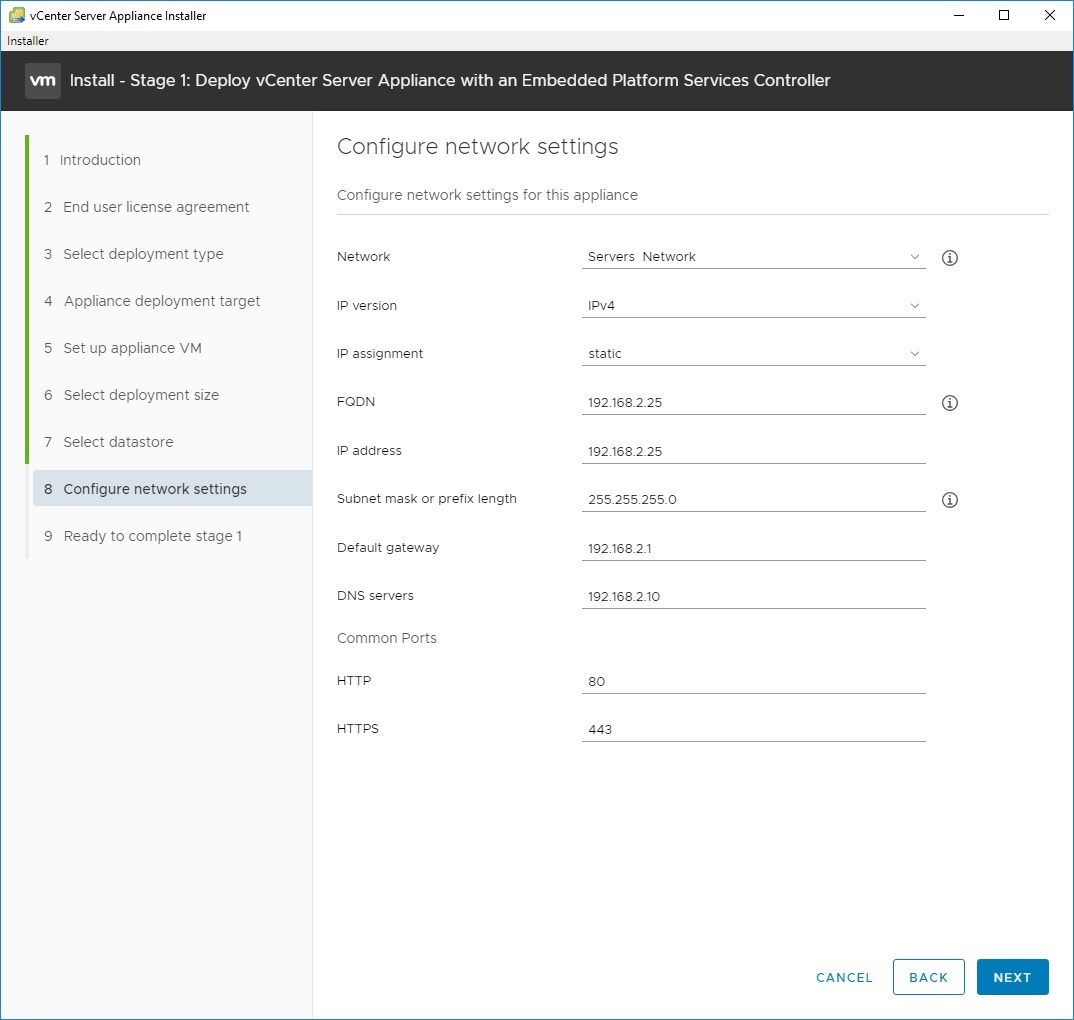
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
vcenter ip address no dns
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
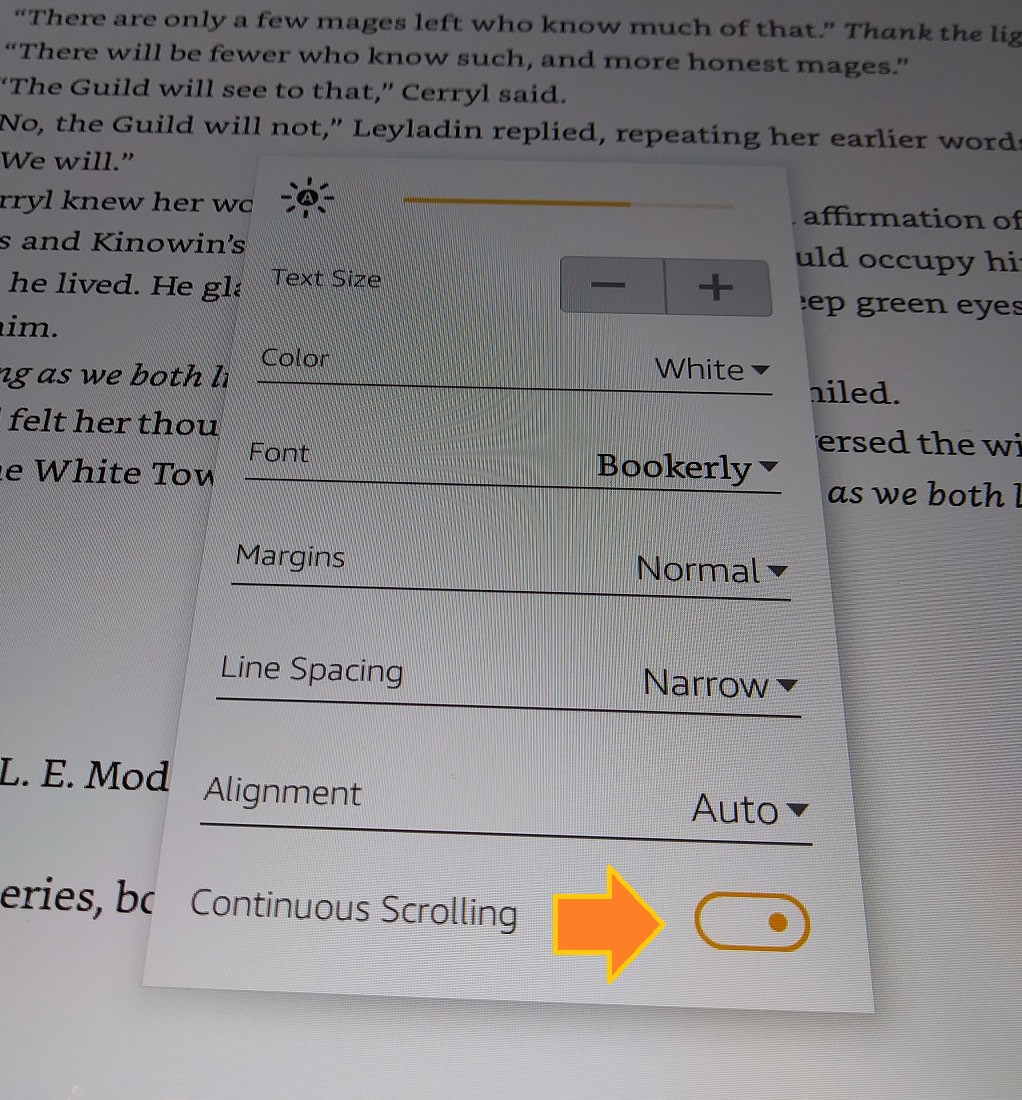
How to disable continuous scrolling on Kindle - turn on page flip
disable continuous scrolling option displays
How to disable continuous scrolling on Kindle - turn on page flip
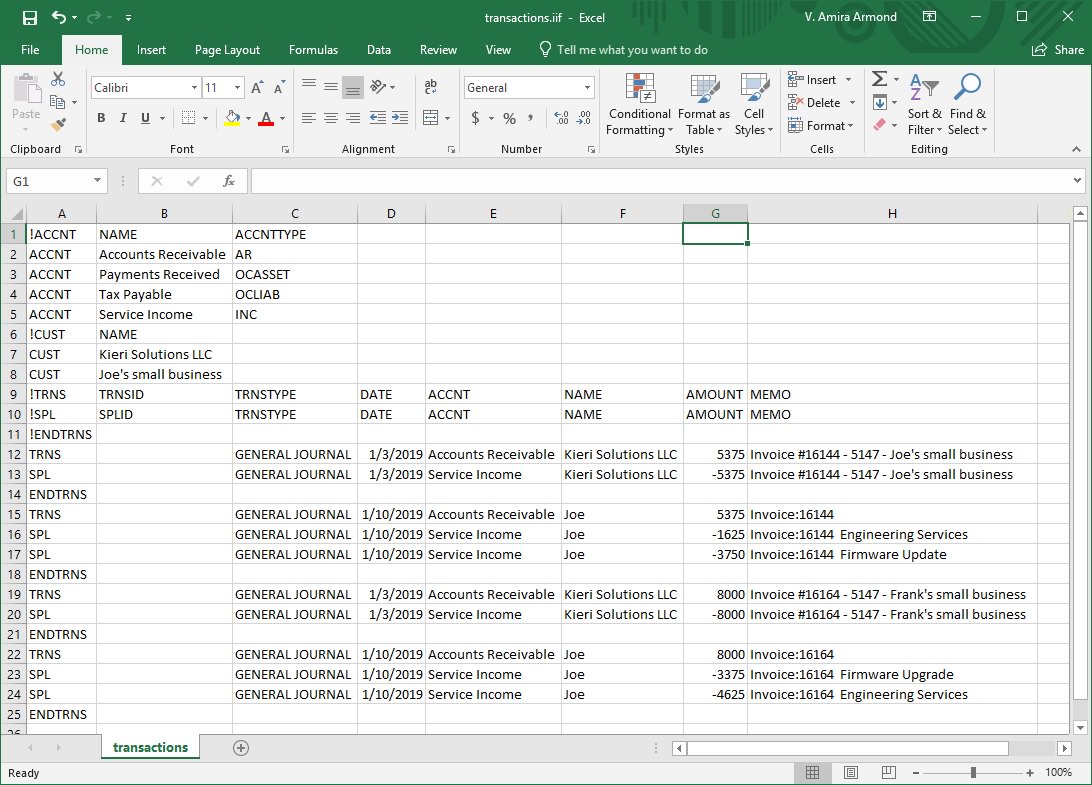
17hats how to export or convert to Excel CSV TAB XLS workbook
17hats export convert iff to csv tab excel
17hats how to export or convert to Excel CSV TAB XLS workbook
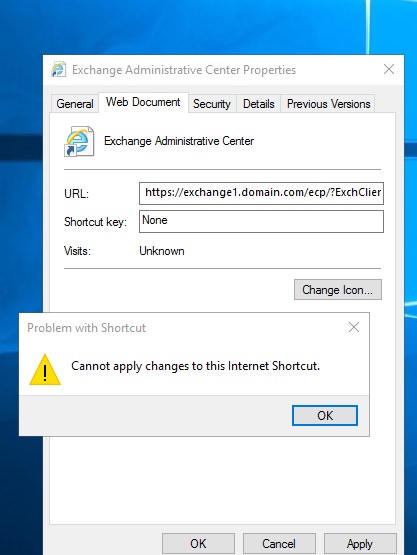
How to fix "Cannot apply changes to this Internet Shortcut" Windows
cannot apply changes to this internet shortcut 2016 2019
How to fix "Cannot apply changes to this Internet Shortcut" Windows
Best Free Computer Incident Response Templates and Scenarios
best free incident response reporting form cybersecurity IT
Best Free Computer Incident Response Templates and Scenarios
Firmware & System Patching Services | DC & Maryland
poweredge server raid reconfigure add disks 1 5
Firmware & System Patching Services | DC & Maryland
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
Best practice network segmentation and hardening prevents pivot attacks NIST
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Best practices and how to install esxi vsphere vcenter vmware and troubleshooting problems during the migration
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Disaster Recovery & Business Continuity in DC & Maryland
disaster recovery drp bcp hipaa frederick columbia gaithersburg baltimore rockville
Disaster Recovery & Business Continuity in DC & Maryland
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
installation services netapp disk shelf baltimore columbia rockville
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
SBDC - Intro to GDPR training - Frederick MD
intro gdpr overall sbdc fitci frederick
SBDC - Intro to GDPR training - Frederick MD
GDPR and Human Resources
cybersecurity cyber security hardening compliance firewall design frederick
GDPR and Human Resources
No, your computer isn't slow.
why slow computer pc repair frederick damascus mt airy md
No, your computer isn't slow.
Why you should consider a credit freeze - EquiFax hack
credit freeze equifax hack how to breach innovis
Why you should consider a credit freeze - EquiFax hack
Virtual Servers, Storage, and SAN - Why your servers are slow
cybersecurity compliance design consulting engineering
Virtual Servers, Storage, and SAN - Why your servers are slow
How to un-freeze your laptop like a pro
pc or computer problem repair damascus lisbon mt airy laytonsville
How to un-freeze your laptop like a pro
Upgrade your IT Services for the New Year
managed services it department outsource company frederick columbia germantown gaithersburg
Upgrade your IT Services for the New Year
Dell PowerEdge R730 PERC RAID online reconfiguration
poweredge server raid reconfigure add disks 1 5
Dell PowerEdge R730 PERC RAID online reconfiguration
Dreamhost HTTP error Wordpress media upload and library
dreamhost http error picture disappear upload shared wordpress
Dreamhost HTTP error Wordpress media upload and library
FortiAnalyzer Configuration problems after initial deploy
FortiAnalyzer 5.4 Storage Quota Limits for ADOM root
FortiAnalyzer Configuration problems after initial deploy
FortiAnalyzer Report: User Web Browsing by Category
fortianalyzer custom report users by category who is browsing web goofing off
FortiAnalyzer Report: User Web Browsing by Category
GDPR Consulting - What you need to know
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
GDPR Consulting - What you need to know
The #1 Computer Security Threat Just Evolved - RCE Worm
cybersecurity cyber security compliance firewall frederick md
The #1 Computer Security Threat Just Evolved - RCE Worm
Fix vSphere & vCenter Datastore Size Reverting
security design cybersecurity consulting services compliance
Fix vSphere & vCenter Datastore Size Reverting
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
conflicting vibs error vsphere upgrade metadata consultant vmware
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
Is your IT person holding the network hostage?
Server Upgrade Cybersecurity Consultant SAN Netapp Frederick
Is your IT person holding the network hostage?
4 Hiring Mistakes When Choosing an IT Company
mistakes when hire IT consultant MSP managed service provider computer support outsourcing
4 Hiring Mistakes When Choosing an IT Company
What you should know about Cloud Computing and Office 365
cloud IT department migration Office 365 Frederick Baltimore Columbia MD
What you should know about Cloud Computing and Office 365
Can You Make Our Nation Safe from Hackers?
The Ultimate Way to Protect Against Computer Theft
Kieri Solutions site icon
The Ultimate Way to Protect Against Computer Theft
Small / medium business security concerns
managed services it department outsource company frederick columbia germantown gaithersburg
Small / medium business security concerns
Approaches to security policy
cybersecurity cyber security hardening compliance firewall design frederick
Approaches to security policy

Article

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan

Article

What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.

Article

NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3

No one wants to start from blank templates.

No one wants to start from
blank templates.

Stop starting from blank templates. Get documentation proven through actual CMMC Level 2 assessment.