Open navigation menu - Kieri Solutions
Can You Make Our Nation Safe from Hackers?

Can You Make Our Nation Safe from Hackers?

In this article

Can You Make Our Nation Safe from Hackers?


This article is meant for you as a voting citizen, rather than you as a home user or business owner.  Nationally, for our own security, we need to make changes to the way our IT infrastructure is managed.


Proposal

Nationally, identify potential computer impacts in a tier structure.  Each utility, large company, and government agency is expected to report this yearly.  The idea is to measure the worst impact a complete information systems disruption could cause if it is unavailable for three weeks.  Based on the tier, the U.S. government would enforce increasing security measures with the intention of reducing risk of disruption/attack.

This should be done per segment of the enterprise.  For example, a power utility has a minimum of four segments:  a) the actual power grid  b) the customer-facing payment portal c) the internal network for communications and planning d) coordination communications to other power utilities.  If these segments were taken down entirely, they would have vastly different impacts.


Tiers:

1st tier: Isolated economic hardship, alternatives exist.  This is a service which can be temporarily ignored or bypassed.  Think of customer facing payment portals, small and medium business outages.

Security requirement for 1st level:  No requirement.  Businesses will evaluate their own threat profile to determine whether high security is necessary.

2nd tier: Economic hardship, no alternatives.  This is a service which can cause harm to our national economy or severe disruption to consumers if it is unavailable for more than a day.  A cell phone network could fit this definition, or a complete outage of Amazon.

Security requirement for 2nd level: Security engagement and Continuity Of Operations Plan (COOP) is required.  The COOP plan should describe a way to restore service from backups or other storage that would be unaffected by a malicious software attack on the main system.

3rd tier: Potential death toll of 1-10,000.  This is a service which supports food/water, health, shelter, or emergency services, but which has readily available alternatives.  An example would be a large pharmacy or hospital system – critical patients may not be able to transition in time but the majority of patients would survive.  Or loss of 911 service.  Or intersection lights becoming un-synchronized.  Using some imagination, there are many information systems that could cause deaths.

Security requirement for 3rd level: Network separation or warm secondary system, active security review is required.  Network separation means no communication between casual networks (such as the Internet or back-office network) and the critical system.  This dramatically reduces the chance of widespread network based attacks and makes intentional hacking extremely difficult.  For systems that cannot be separated, the alternative is to run warm secondary systems that can take over in case of outage.  The warm systems should be designed to be resistant to the spread of network based attacks.  It does no good to have a secondary system that is compromised at the same time as the primary system.   Active security review means that the U.S. Government performs annual security audits against the network to find weaknesses, and requires that the organization fixes these weaknesses.

4th tier: Catastrophic death toll 10,000+.  This is a service which supports food/water, health, shelter, or emergency services which does not have alternatives.  Power grid or water failures fit into this category, especially if they can cascade across more than one local region.  Outages which prevent our military/government from responding to national threats also count.

Security requirement for 4th level:  Segmented network separation and second-set-of-eyes rule.   Segmented network separation means that not only is there an air-gap between the critical system and casual networks, but wherever possible the critical system should be segmented into independent pieces too.  For example, a power grid control network should be designed to be independently-operable in each geographic region.  The idea is to prevent cascading outages like the one that cut off power to the entire NorthEast United States and part of Canada in 2003.  Second-set-of-eyes rule is an extreme security measure which is intended to prevent all insider and outsider threats.  Essentially, any time the critical system is altered (such as a patch or update), the package code should be reviewed by a minimum of two people for unintended functionality such as backdoors or time bombs.  This rule requires the critical system to be very simple (think UNIX) and single-purpose, since it would be impossible to review the code on complex systems like Microsoft Servers.


What do you think?
 

Cybersecurity data analysis supporting CMMC Level 2 audit preparation for defense contractors

Talk to an Expert

Tell us where you are with compliance and we’ll map out the next steps for your team.

Don't miss these

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan
Is Your Security Plan Telling the Truth?
What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.
What Does the Government Actually Require of You Today?
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3
NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
CMMC Backup Requirements and The Myths Worth Ignoring
Server backup drives in a dark data center supporting CMMC backup requirements for a defense contractor
CMMC Backup Requirements and The Myths Worth Ignoring
How to Prepare for a DIBCAC High Assessment
Analyst reviewing evidence on dark dual monitors while preparing for a DIBCAC High assessment
How to Prepare for a DIBCAC High Assessment
Out of Scope Assets - What the Final Rule Actually Changed
Abstract data cityscape tied to out of scope assets in a CMMC assessment by Kieri Solutions
Out of Scope Assets - What the Final Rule Actually Changed
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
Dark cybersecurity image with glowing data illustrating CMMC final rule compliance for defense contractors
CMMC Proposed Rule Analysis - What Defense Contractors Need to Know
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
Analyst reviewing code while working toward CMMC and NIST 800-171 compliance
CMMC Phase 2 Suspended and What Defense Contractors Need to Know
CUI Assets - What Assessors Actually Evaluate
Abstract network of nodes tied to CUI assets and CMMC scope assessed by Kieri Solutions
CUI Assets - What Assessors Actually Evaluate
Do I Even Have CUI? Understanding What You Need to Protect
Abstract data network tied to finding CUI on a defense contractor network with Kieri
Do I Even Have CUI? Understanding What You Need to Protect
Why the DoD Wants Security Protection Data Protected Like CUI
Abstract data network tied to security protection data and CMMC scope assessed by Kieri
Why the DoD Wants Security Protection Data Protected Like CUI
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Cybersecurity professional conducting CMMC gap analysis for a defense contracting organization
Why Your CMMC Gap Analysis Might Be Worthless - 110 Practices vs 320 Assessment Objectives
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Network architecture visualization for a CMMC Level 2 reference architecture built on Microsoft 365 GCC High
Building a CMMC Level 2 Compliant Network You Can Actually Manage
Why Most CMMC Documentation Fails and How to Fix It
CMMC compliance documentation policies and procedures
Why Most CMMC Documentation Fails and How to Fix It
What Passed a DOD Assessment for System Baselining and Inventories
CMMC system inventory and baseline configuration monitoring dashboard
What Passed a DOD Assessment for System Baselining and Inventories
How to Implement Mobile Code Requirements for CMMC Level 2
CMMC mobile code security controls and technical implementation
How to Implement Mobile Code Requirements for CMMC Level 2
What Does "Monitor" Actually Mean in CMMC Requirements?
CMMC monitoring requirements - access control and password security verification
What Does "Monitor" Actually Mean in CMMC Requirements?
The Version 20 Problem and How to Avoid It
CMMC compliance documentation sequence - cybersecurity program management
The Version 20 Problem and How to Avoid It
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
CMMC Level 2 compliant environment security controls and access management
Build Your Own CMMC Level 2 Compliant Environment with the Kieri Reference Architecture
Inside the KCD - What Makes This Documentation Different
CMMC compliance documentation templates digital security
Inside the KCD - What Makes This Documentation Different
How the Kieri Compliance Documentation and Reference Architecture Work Together
Kieri Compliance Documentation and Reference Architecture working together for CMMC Level 2 compliance
How the Kieri Compliance Documentation and Reference Architecture Work Together
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC compliance documentation and reference architecture security controls - fingerprint scanning and access management
What's Actually Inside the Kieri Compliance Documentation? A Complete Walkthrough
CMMC Assessments by Kieri Solutions
Global cybersecurity compliance support for defense contractors under DFARS
CMMC Assessments by Kieri Solutions
CMMC Education: User vs Network Session Termination
Secure IT infrastructure design supporting CMMC Level 2 compliance for defense contractors
CMMC Education: User vs Network Session Termination
CMMC Proposed Rule has been released! 
Cybersecurity threat - CMMC compliance
CMMC Proposed Rule has been released! 
Interested in the Kieri Compliance Documentation?
Secure data transmission within CMMC compliant network architecture
Interested in the Kieri Compliance Documentation?
How to fix Outlook missing Friday January 13 2023
Interconnected defense contractor networks requiring CMMC Level 2 cybersecurity certification
How to fix Outlook missing Friday January 13 2023
C3PAO Meeting - July 26, 2021 12-1 pm EDT
NIST SP 800-171 DoD Self Assessment Services
DFARS 252.204-7012 and NIST SP 800-171 requirements
NIST SP 800-171 DoD Self Assessment Services
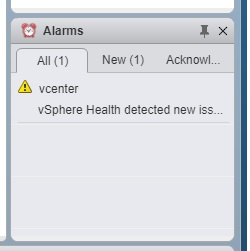
vSphere Health detected new issues in your environment 6.7
vcenter 6.7 alarm displays vsphere health detected new issue
vSphere Health detected new issues in your environment 6.7
vCenter Health Warning: External Platform Services Controller
Synology storage latency and disconnects on VMware
Windows Stuck in Recovery Mode Datto driver signing
Office 365 MFA App Password Missing Fix
Microsoft Teams Conference Calls & Dial-In Numbers
C: Drive Full Exchange
Exchange server very slow, services and network blank
Exchange 2016 DAG - 3 servers 2 sites
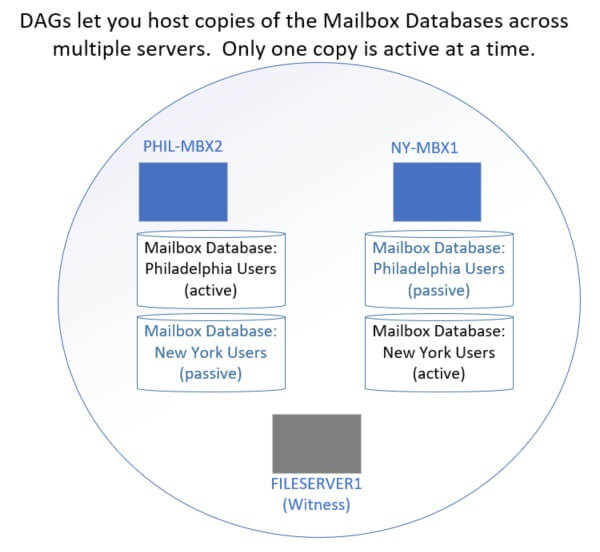
Diagram showing mailbox servers with active and passive databases. Each database is only active on one server.
Exchange 2016 DAG - 3 servers 2 sites
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
Kieri Solutions partnering with defense contractors to achieve CMMC Level 2 certification
Netapp 3rd-party CA certificates expiring DeutscheTelekomRootCA2
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
warning vsphere health detected new issue memory exhaustion 6.7 vcenter
vCenter 6.7 Memory Exhaustion and vSphere health (Tiny)
Step by Step: Upgrade vCenter VCSA 6.0 (or 6.5) to 6.7
How to prepare for a DoD CMMC audit and certification
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
How to prepare for a DoD CMMC audit and certification
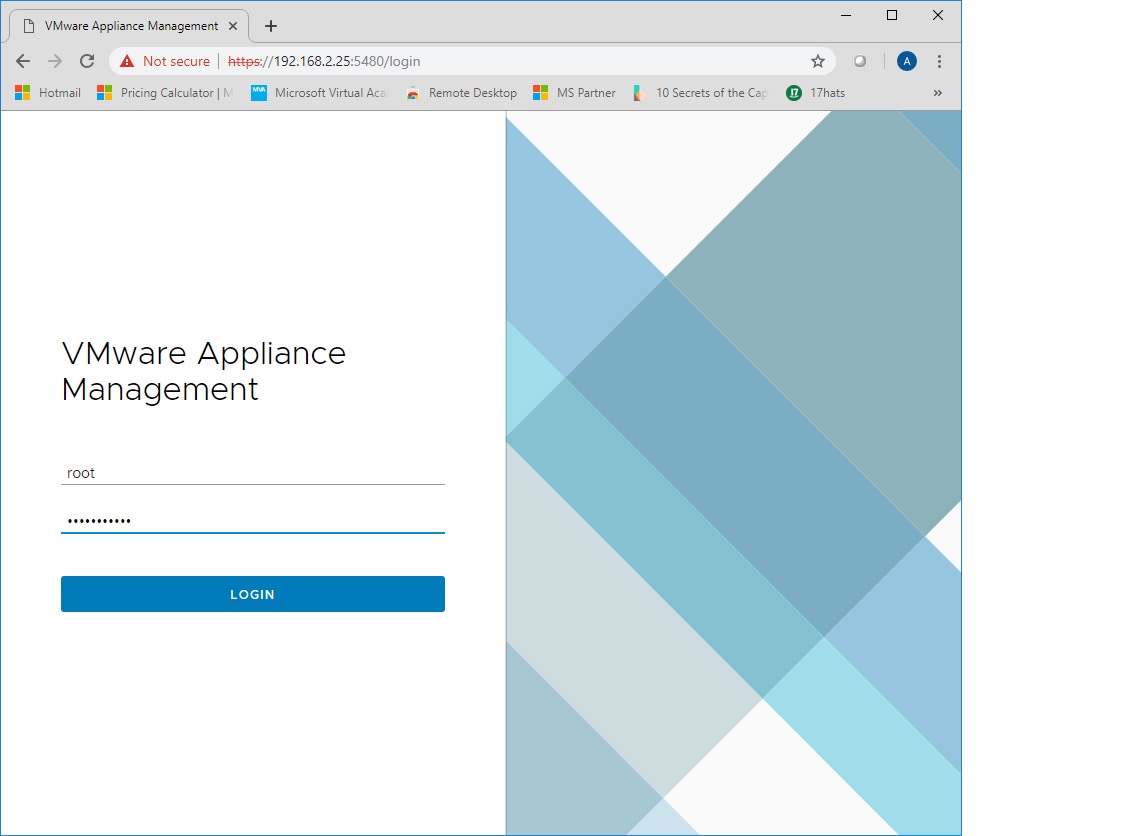
Fix Expired vCenter Root Password (6.5 & 6.7)
How to rename Windows Server 2016 Domain Controller
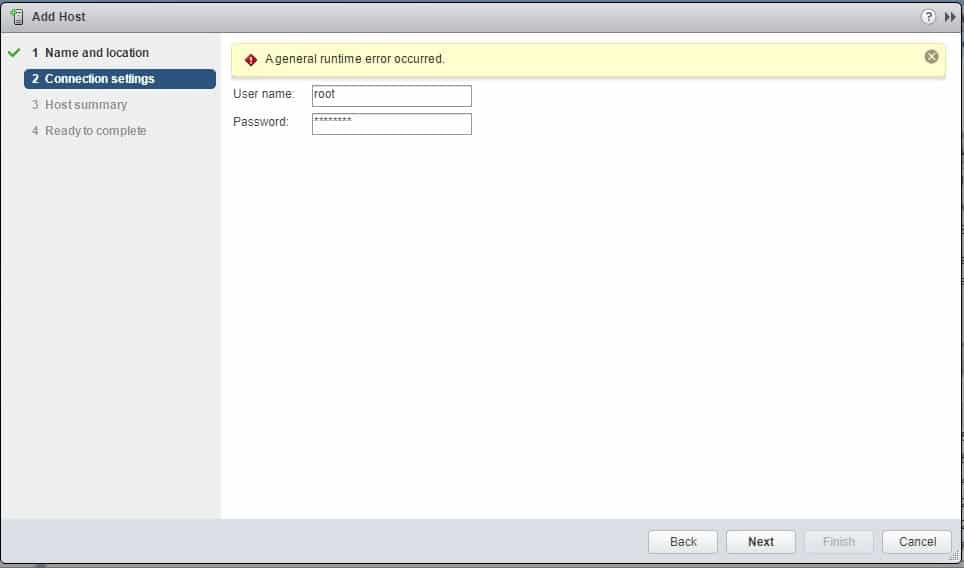
Runtime Error Adding Host in VMware vCenter & ESXi
add host a general runtime error occurred vcenter 6.5 6.7
Runtime Error Adding Host in VMware vCenter & ESXi
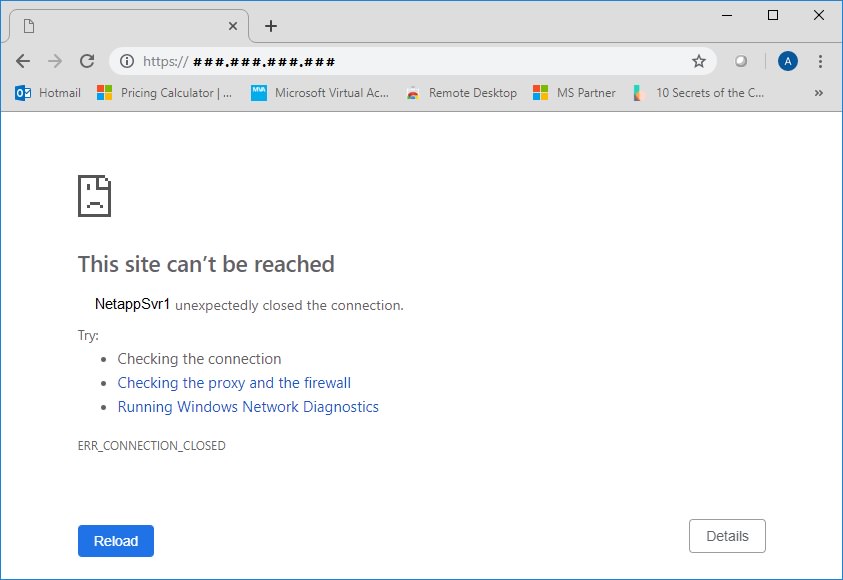
How to fix Netapp expired self-signed certificate by creating a new one
netapp certificate expired install site cant be reached
How to fix Netapp expired self-signed certificate by creating a new one
How to register a warranty or service agreement on HPE website
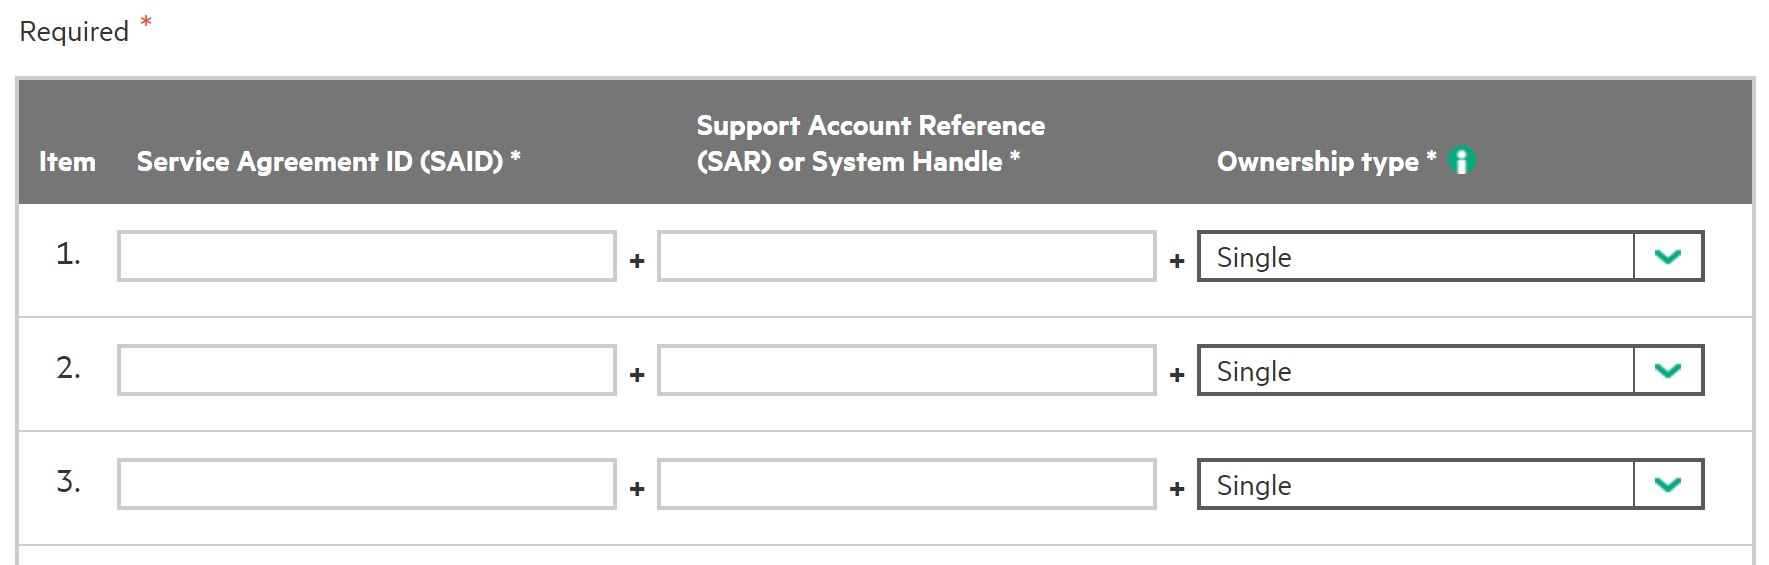
hpe hp register account SAR ID service agreement warranty how accept
How to register a warranty or service agreement on HPE website
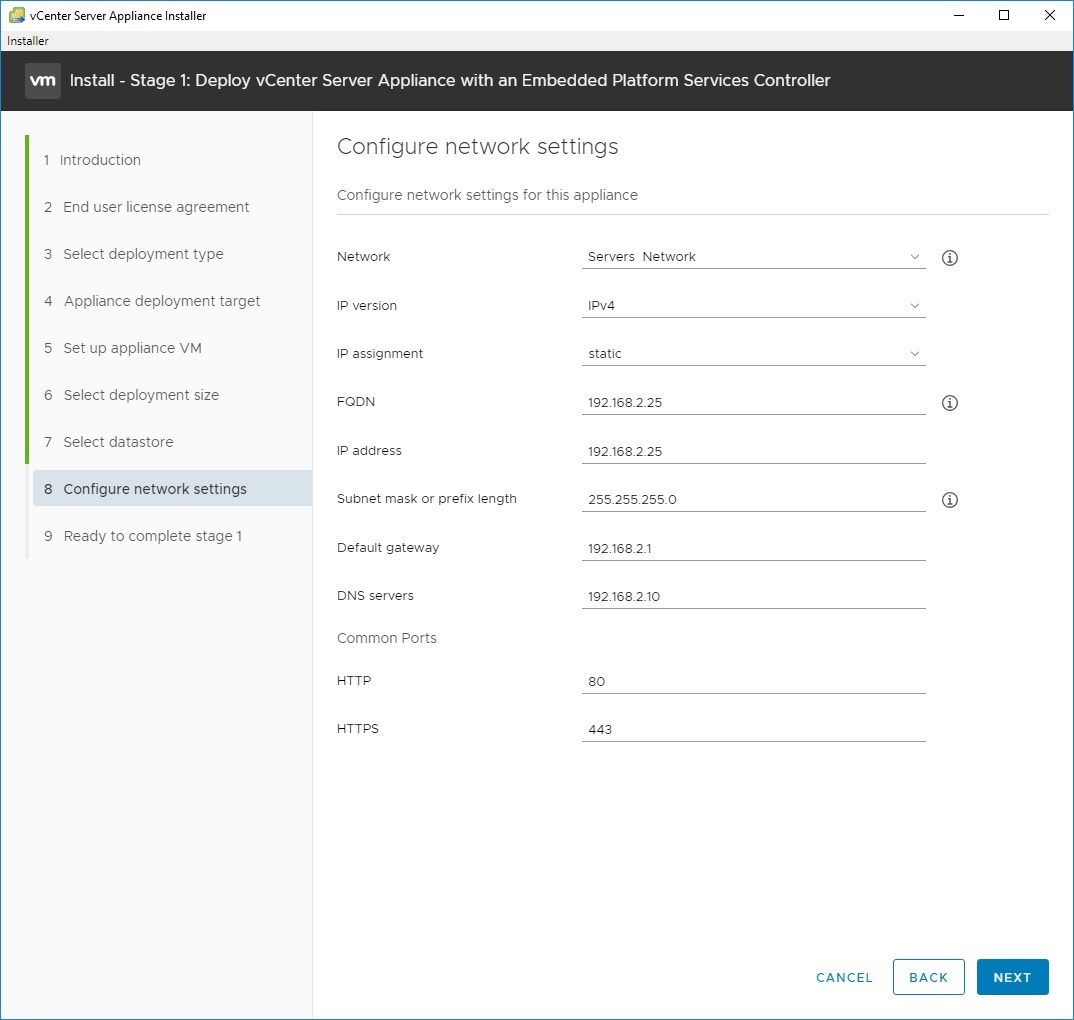
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
vcenter ip address no dns
How to install vCenter 6.7 (and 6.0 and 6.5) with no DNS, only IP address
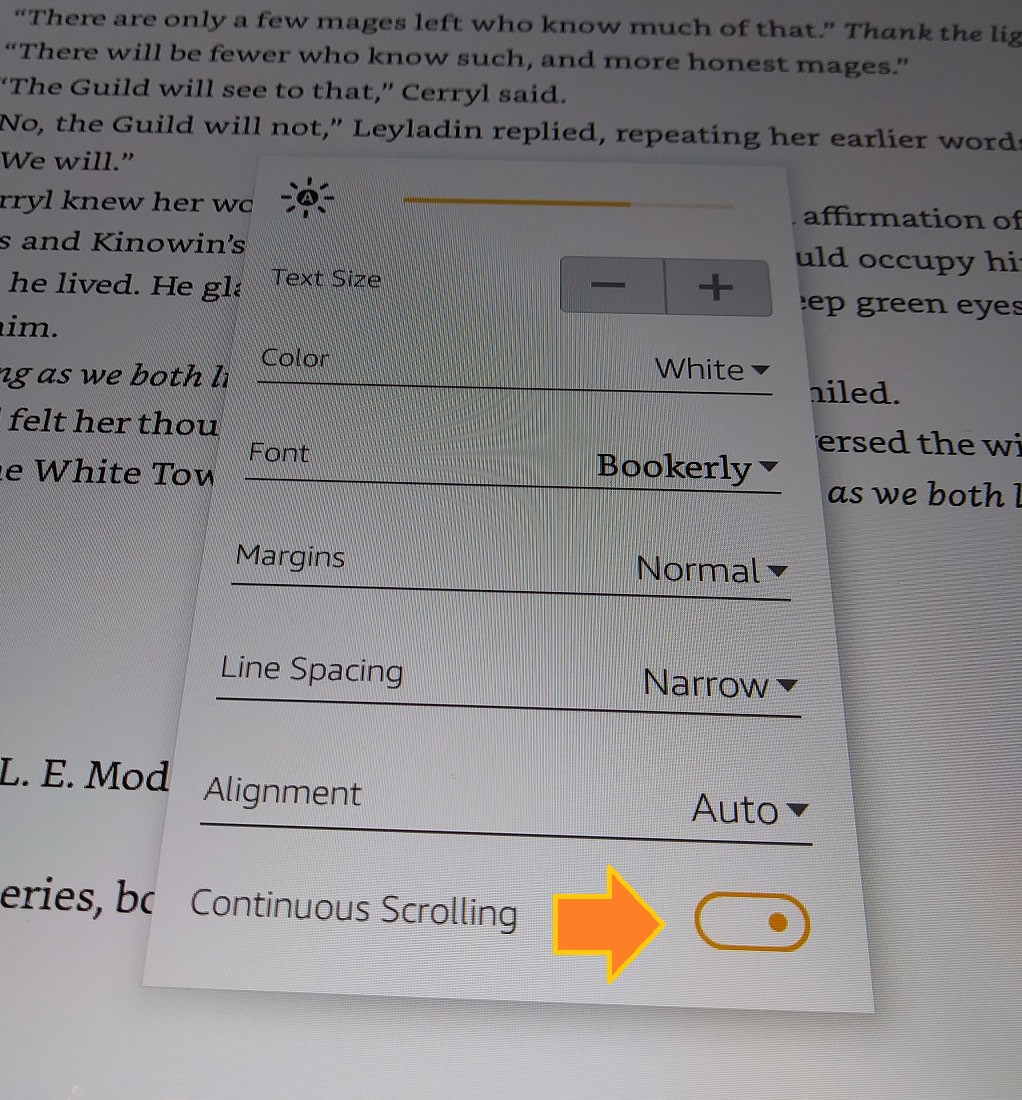
How to disable continuous scrolling on Kindle - turn on page flip
disable continuous scrolling option displays
How to disable continuous scrolling on Kindle - turn on page flip
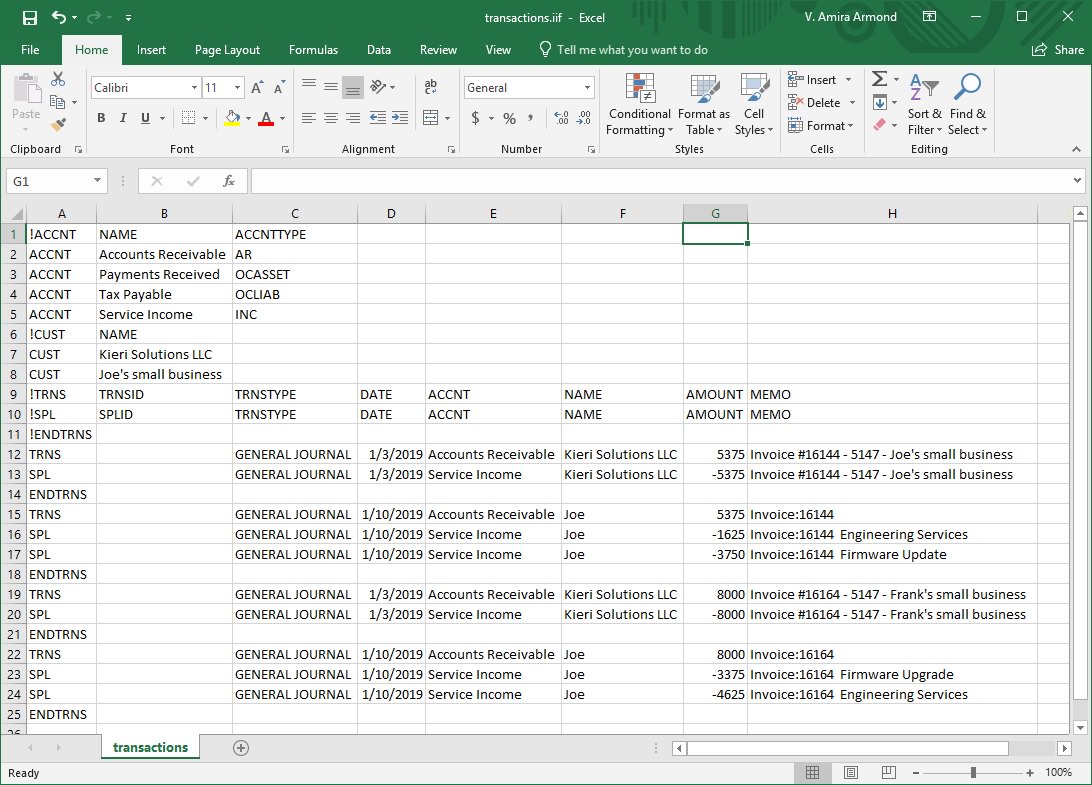
17hats how to export or convert to Excel CSV TAB XLS workbook
17hats export convert iff to csv tab excel
17hats how to export or convert to Excel CSV TAB XLS workbook
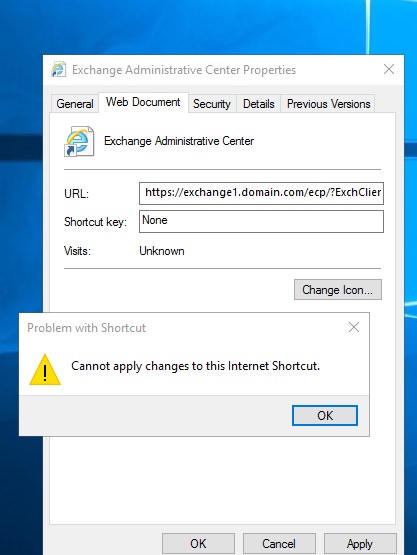
How to fix "Cannot apply changes to this Internet Shortcut" Windows
cannot apply changes to this internet shortcut 2016 2019
How to fix "Cannot apply changes to this Internet Shortcut" Windows
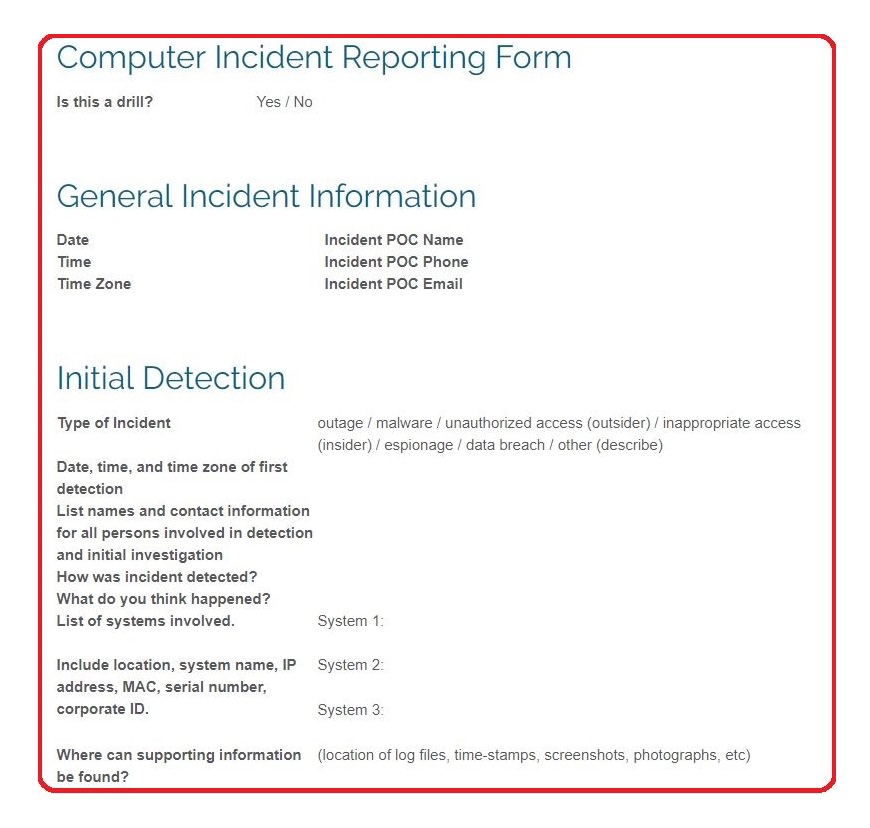
Best Free Computer Incident Response Templates and Scenarios
best free incident response reporting form cybersecurity IT
Best Free Computer Incident Response Templates and Scenarios
Firmware & System Patching Services | DC & Maryland
poweredge server raid reconfigure add disks 1 5
Firmware & System Patching Services | DC & Maryland
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
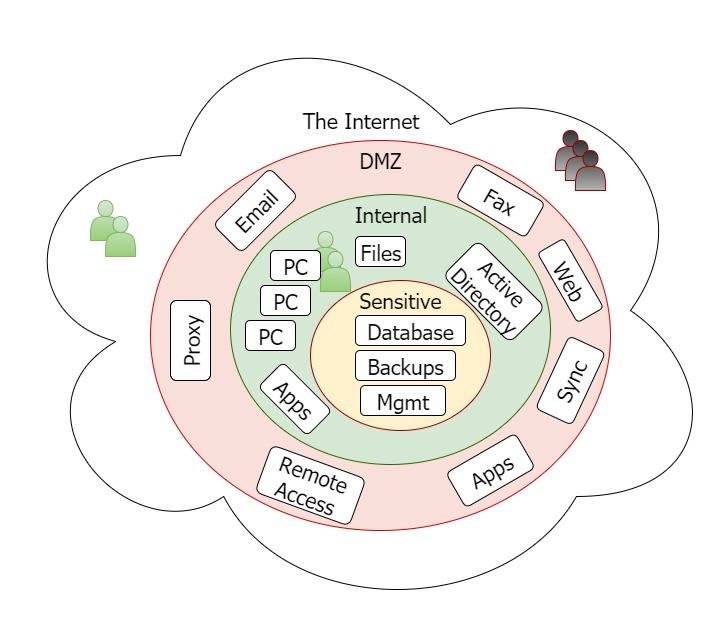
Best practice network segmentation and hardening prevents pivot attacks NIST
Network hardening near Baltimore MD, Frederick, Rockville, Gaithersburg and DC
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Best practices and how to install esxi vsphere vcenter vmware and troubleshooting problems during the migration
VMware vSphere ESX and vCenter Upgrade 5.5 to 6.0 or 6.5 or 6.7 best practices
Disaster Recovery & Business Continuity in DC & Maryland
disaster recovery drp bcp hipaa frederick columbia gaithersburg baltimore rockville
Disaster Recovery & Business Continuity in DC & Maryland
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
installation services netapp disk shelf baltimore columbia rockville
VMWare and Netapp consultant in DC, Baltimore, Columbia, Frederick, and Rockville MD
SBDC - Intro to GDPR training - Frederick MD
intro gdpr overall sbdc fitci frederick
SBDC - Intro to GDPR training - Frederick MD
GDPR and Human Resources
cybersecurity cyber security hardening compliance firewall design frederick
GDPR and Human Resources
No, your computer isn't slow.
why slow computer pc repair frederick damascus mt airy md
No, your computer isn't slow.
Why you should consider a credit freeze - EquiFax hack
credit freeze equifax hack how to breach innovis
Why you should consider a credit freeze - EquiFax hack
Virtual Servers, Storage, and SAN - Why your servers are slow
cybersecurity compliance design consulting engineering
Virtual Servers, Storage, and SAN - Why your servers are slow
How to un-freeze your laptop like a pro
pc or computer problem repair damascus lisbon mt airy laytonsville
How to un-freeze your laptop like a pro
Upgrade your IT Services for the New Year
managed services it department outsource company frederick columbia germantown gaithersburg
Upgrade your IT Services for the New Year
Dell PowerEdge R730 PERC RAID online reconfiguration
poweredge server raid reconfigure add disks 1 5
Dell PowerEdge R730 PERC RAID online reconfiguration
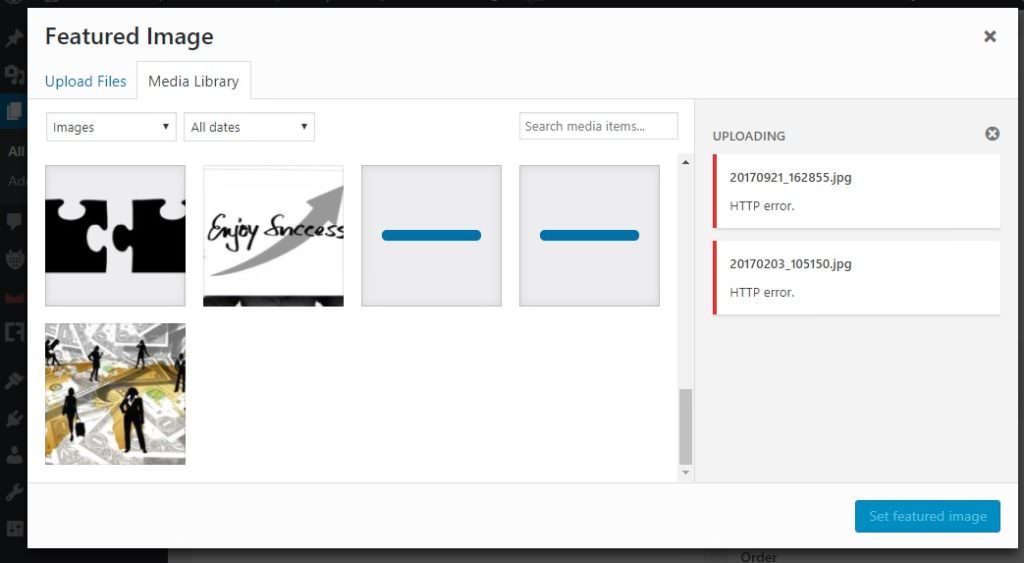
Dreamhost HTTP error Wordpress media upload and library
dreamhost http error picture disappear upload shared wordpress
Dreamhost HTTP error Wordpress media upload and library
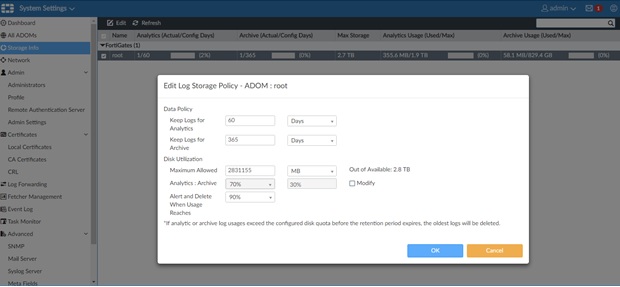
FortiAnalyzer Configuration problems after initial deploy
FortiAnalyzer 5.4 Storage Quota Limits for ADOM root
FortiAnalyzer Configuration problems after initial deploy
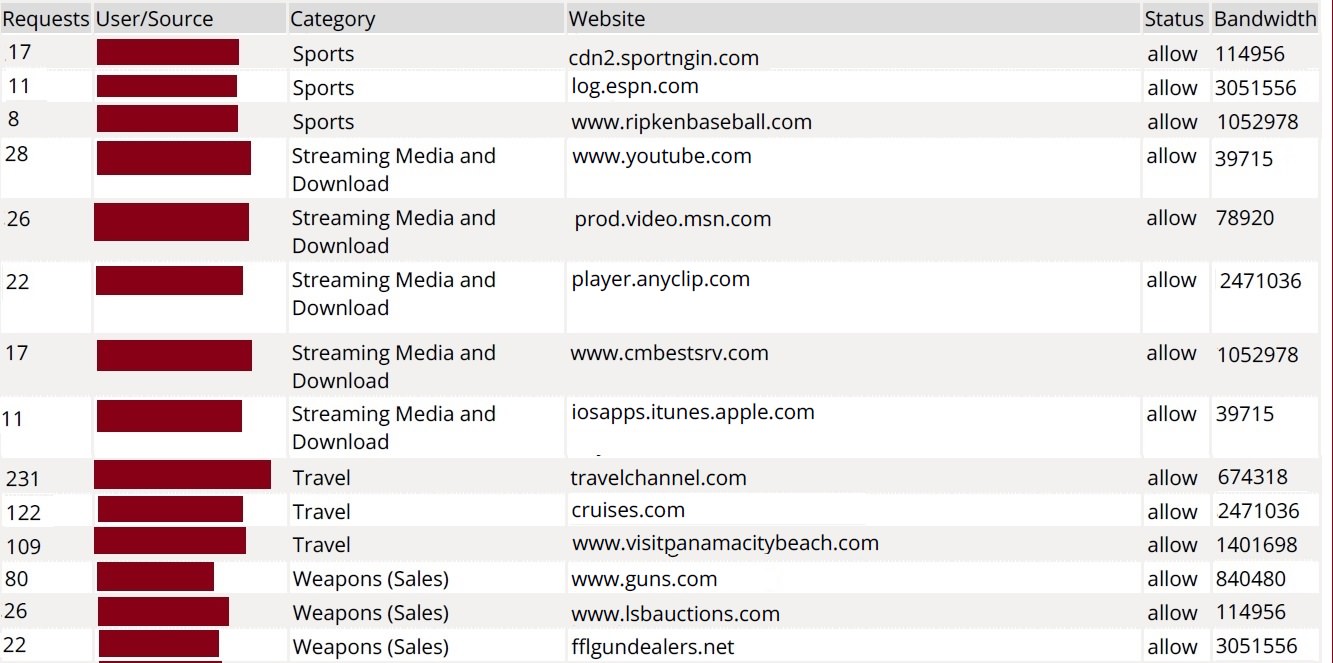
FortiAnalyzer Report: User Web Browsing by Category
fortianalyzer custom report users by category who is browsing web goofing off
FortiAnalyzer Report: User Web Browsing by Category
GDPR Consulting - What you need to know
cybersecurity CMMC DoD NIST 800-171 compliance nist 800-53
GDPR Consulting - What you need to know
The #1 Computer Security Threat Just Evolved - RCE Worm
cybersecurity cyber security compliance firewall frederick md
The #1 Computer Security Threat Just Evolved - RCE Worm
Fix vSphere & vCenter Datastore Size Reverting
security design cybersecurity consulting services compliance
Fix vSphere & vCenter Datastore Size Reverting
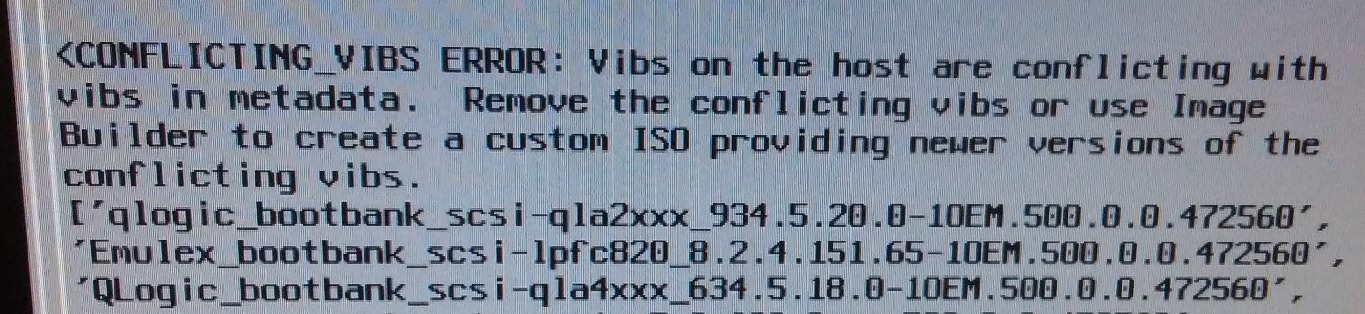
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
conflicting vibs error vsphere upgrade metadata consultant vmware
HP DL360p g8 ESXi 5.5 to 6.5 upgrade conflicting_vibs_error
Is your IT person holding the network hostage?
Server Upgrade Cybersecurity Consultant SAN Netapp Frederick
Is your IT person holding the network hostage?
4 Hiring Mistakes When Choosing an IT Company
mistakes when hire IT consultant MSP managed service provider computer support outsourcing
4 Hiring Mistakes When Choosing an IT Company
What you should know about Cloud Computing and Office 365
cloud IT department migration Office 365 Frederick Baltimore Columbia MD
What you should know about Cloud Computing and Office 365
Can You Make Our Nation Safe from Hackers?
The Ultimate Way to Protect Against Computer Theft
Kieri Solutions site icon
The Ultimate Way to Protect Against Computer Theft
Small / medium business security concerns
managed services it department outsource company frederick columbia germantown gaithersburg
Small / medium business security concerns
Approaches to security policy
cybersecurity cyber security hardening compliance firewall design frederick
Approaches to security policy

Article

Is Your Security Plan Telling the Truth?
Server room corridor lined with racks in a data center covered by a System Security Plan

Article

What Does the Government Actually Require of You Today?
A network of yellow lines connecting round nodes against a dark background.

Article

NIST SP 800-171 Rev 3, What Changed and What It Means for Your CMMC Timeline
Man at a desk in a dark office reading text on a computer monitor, NIST SP 800-171 Rev 3

No one wants to start from blank templates.

No one wants to start from
blank templates.

Stop starting from blank templates. Get documentation proven through actual CMMC Level 2 assessment.