Official CMMC Level 2 Certification From Authorized Assessors

Comprehensive assessment from an authorized C3PAO with a readiness check before you start and remediation close-out to fix small problems afterward. Our assessment teams are Kieri employees, not subcontractors.

Assessment Failures Delay Certification for Months

Pre-assessment Process To Ensure Readiness Before Certification

Why Kieri
for Your CMMC Assessment

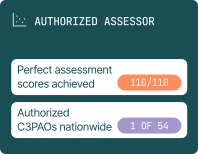
50+ assessments completed since CMMC went live, led by certified assessors who are Kieri employees

Readiness Verification Included

We review your scope and implementation at a high level before formal assessment begins. If there’s a problem, we’ll let you know before you’re on the clock.

We can Conduct Both a Mock and Certification Assessment

We can issue your official CMMC Level 2 certification. No need to coordinate with separate assessment organizations.

Experienced Assessment Teams

Over 20 certified assessors averaging 21 years of cybersecurity experience. Our assessors are Kieri employees, not 1099 subcontractors, so you get consistent quality across every engagement.

Assessment Process

We Develop Your CMMC Roadmap Together

  • Immediate download of all policies, procedures, System Security Plans, and templates.
  • Everything mapped to CMMC and NIST SP 800-171 requirements.

Documentation That Passes Real Assessments

  • Pre-written policies, procedures, and System Security Plans based on our own CMMC Level 2 certification
  • Built for organizations under 1,000 users, not downsized enterprise frameworks
Kieri Compliance Documentation features including NIST SP 800-171 and identity verification

From Preparation to Certification

  • Gap analysis, consulting, documentation leading to CMMC Level 2 assessment
  • Every engagement led by certified CMMC assessors with real assessment experience
NIST SP 800-171 compliance solutions for small defense contractors

Comprehensive CMMC Assessment Services

Mock Assessment

Readiness Verification

Formal CMMC Assessment

Official CMMC Level 2 assessment conducted by authorized C3PAO. Comprehensive evaluation of all controls with detailed findings for each assessment objective.

Evidence Review

Thorough examination of your compliance evidence. We verify documentation completeness and validate that evidence demonstrates sustained compliance.

Technical Testing

Hands-on verification of technical control implementations. We test configurations, review system settings, and validate security measures.

Interview Process

Structured interviews with your team to understand processes and validate implementations. We assess organizational understanding of compliance obligations.

Close-Out Assessment

We include up to 4 hours of virtual Close-Out Assessment so you can resolve any gaps and complete your certification. Most clients fix small issues quickly, and we schedule a POA&M re-assessment within a few days.


Certification Issuance

Official CMMC Level 2 certification and Letter of Attestation upon successful completion. Documentation you can share with customers and prime contractors.

What Sets Our
Assessments Apart

Technical
Depth

Our assessors are more technical than average. We handle complex environments including cloud services, distributed systems, and specialized manufacturing networks.

Reasonable
Interpretation

We advocate for common sense assessments and practical scoping. Our approach balances security requirements with operational reality.


Transparent
Communication

You understand exactly what we’re evaluating and why. We explain our interpretation of gray areas and discuss precedents from previous assessments.

“In our own compliance journey of trying to figure out what we are required to do, even with consultants that helped us along the way, the MOST useful resource that we have found to date has been the KCD.”

Melissa Kimball

, Director

University of Maine

“My team and I have been using the KCD for about a week now, and I have to say, it’s been a breath of fresh air compared to our previous approach. It has made several processes much easier for us, and for that, we’re truly grateful. You have a fantastic product that far exceeds our expectations.”

Daniel Martinez

, Director of Cybersecurity

nDepth Security

Custom Pricing Based on Your Environment

Assessment complexity varies by organization size, system architecture, and implementation maturity. We provide firm fixed-price quotes after understanding your specific environment.

FAQ

A formal CMMC Level 2 assessment takes four days on-site. Before that, we conduct a readiness check to review your scope and implementation at a high level. If issues are found during the assessment, most clients resolve them quickly and we schedule a POA&M re-assessment within a few days.

Start with a gap analysis. Our certified assessors will evaluate your current compliance status against all NIST SP 800-171 requirements, including scoping review, cloud vendor evaluation, and CUI data flow review. You’ll get detailed findings with a prioritized remediation roadmap so you know exactly what to fix before scheduling your formal assessment.

No. We consider the sale of compliance documentation to be consulting, and we don’t provide both consulting and formal assessments to the same client. If you’ve purchased the KCD or KRA, we’ll connect you with other qualified C3PAOs who can perform your certification assessment.

Every assessment includes a detailed findings report for each assessment objective, describing why a requirement wasn’t met, which system is involved, and exactly what part of the objective wasn’t performed. We include a remediation close-out with every formal assessment, so most clients fix issues quickly and we schedule a POA&M re-assessment within a few days.

Once you contact us, we’ll send a questionnaire about your readiness and environment complexity. After a call with our team to review it, we’ll send you a firm fixed-price quote. We recommend reaching out once you’ve identified your scope and aren’t planning to add new systems. We have multiple assessment teams available and are growing to meet demand. If you sign up and you’re ready, we’ll guarantee your schedule.

Yes. We support organizations throughout the United States for CMMC assessments. Our assessment teams travel nationwide.

Organizations that deploy Kieri​

Ready to Schedule Your CMMC Assessment?

Ready to Schedule
Your CMMC Assessment?

Work with an authorized C3PAO that includes a readiness check before you start and remediation close-out afterward. 50+ assessments completed since CMMC went live.